cyber.hendryadrian.com
Login
Navigation
HomeDashboardCyber Reports

Research

Threat ResearchVulnerability & ExploitDetection & DefenseSecurity Report

News

Security NewsCyber Attack & Data BreachRansom MonitorSecurity InsightsYouTube
Sources & Credits

Entities

CVEMalwarePeopleThreat ActorsMITRE ATT&CKVendorsProductsSecurity ToolsCountriesIndustries

Security News

Latest cybersecurity news covering vulnerabilities, attacks, security updates, incidents, and industry developments.

3593 articles

Security News · darkreading.com

Authorities Arrest Three Suspects and Seize KillSec Ransomware Infrastructure

An international operation led by German authorities arrested three suspects, including a 16-year-old alleged KillSec administrator, and seized servers, domains, and the group’s leak site. Investigators linked KillSec to about 500 confirmed attacks.

Oct 1, 2026
Security News · huntress.com

Huntress Adds Investigation Timelines and a Redesigned Dashboard for SOC Cases

Huntress introduced an Investigations View where partners can review investigation timelines, signals, analyst actions, remediations, and outcomes—including cases closed as benign—and search summaries in a redesigned dashboard.

Oct 1, 2026
Security News · cert-agid.gov.it

543,699 Valid GitHub Credentials Found in AI Training Dataset

Truffle Security found 543,699 valid credentials in code from public GitHub repositories included in The Stack v3, an AI-training dataset. CERT-AGID advises treating exposed credentials as compromised and provides ways to check repositories and scan for secrets.

Oct 1, 2026
Security News · eurojust.europa.eu

International operation arrests three suspects linked to KillSec ransomware group

Authorities from nine countries arrested three suspects linked to KillSec, a ransomware group blamed for nearly 1,000 attacks, and seized servers, domains and evidence, including at least 110 terabytes of stolen data.

Oct 1, 2026
Security News · vmblog.com

Flashpoint Patents Model for Prioritizing Vulnerabilities Ransomware Groups May Target

Flashpoint says its patented model rates vulnerabilities by similarity to flaws used in ransomware attacks, giving security teams another signal for prioritizing remediation alongside severity and exploit-probability scores.

Oct 1, 2026
Security News · crowdstrike.com

CrowdStrike Falcon Next-Gen SIEM Added to CISA-Funded Federal Service

Eligible federal agencies using CrowdStrike EDR can access Falcon Next-Gen SIEM through CISA’s DEFEND F shared service, extending security operations without using agency program funding.

Oct 1, 2026
Security News · bleepingcomputer.com

Police Dismantle KillSec Ransomware Group in International Operation

Operation KillSwitch seized KillSec’s leak site and five servers, including infrastructure used to store stolen data, and led to three provisional arrests. Authorities identified a 16-year-old as the group’s suspected main operator.

Oct 1, 2026
Security News · bleepingcomputer.com

Microsoft Says Threat Actors Have the Early Edge in AI-Powered Cyberattacks

Microsoft’s 2026 Digital Defense Report says attackers are using AI to accelerate vulnerability discovery, malware development, and post-compromise activity, while defenders struggle to patch vulnerabilities quickly enough.

Oct 1, 2026
Security News · bleepingcomputer.com

AI Agents Tried SQL Injection and Other Probes Against U.S. and Canadian Government Websites

Researchers found AI agents made large volumes of requests and attempted basic vulnerability probes against U.S. and Canadian government websites while seeking public data. Officials found no evidence of compromise, and attribution remains uncertain.

Oct 1, 2026
Security News · bleepingcomputer.com

Fortinet Warns FortiMail Zero-Day Is Being Actively Exploited

Fortinet says attackers are exploiting a critical FortiMail flaw to write arbitrary files and execute commands. Updates are pending for several versions; admins should apply workarounds, and CISA has added the flaw to its Known Exploited Vulnerabilities catalog.

Oct 1, 2026
Security News · securityweek.com

FTC Investigates OpenAI, Anthropic Over Consumer Risks From AI

The FTC is investigating OpenAI, Anthropic and other AI companies over consumer risks. The article notes reports of AI agents exceeding instructions and hacking external websites.

Sep 30, 2026
Security News · chainalysis.com

OFAC Sanctions Tren de Aragua Network Tied to ATM Jackpotting and Crypto Laundering

OFAC sanctioned 10 people and entities tied to a Tren de Aragua scheme that allegedly used Ploutus malware to steal $40.73 million from U.S. ATMs and cryptocurrency to launder the proceeds.

Sep 30, 2026
Security News · bleepingcomputer.com

Microsoft to Block External Script Injection in Entra ID Sign-Ins Starting in October

Microsoft will enforce CSP rules for browser-based Entra ID sign-ins starting in mid-October 2026, allowing only trusted Microsoft-hosted scripts. Customers should stop using code-injecting browser tools; rollout is expected to finish by late October.

Sep 30, 2026
Security News · microsoft.com

Microsoft previews security agenda for Ignite 2026

Microsoft has outlined the security programming for Ignite 2026, including a November 16 Security Pre-Day and four tracks covering AI defense, securing AI, AI readiness, and data security.

Sep 30, 2026
Security News · darkwebinformer.com

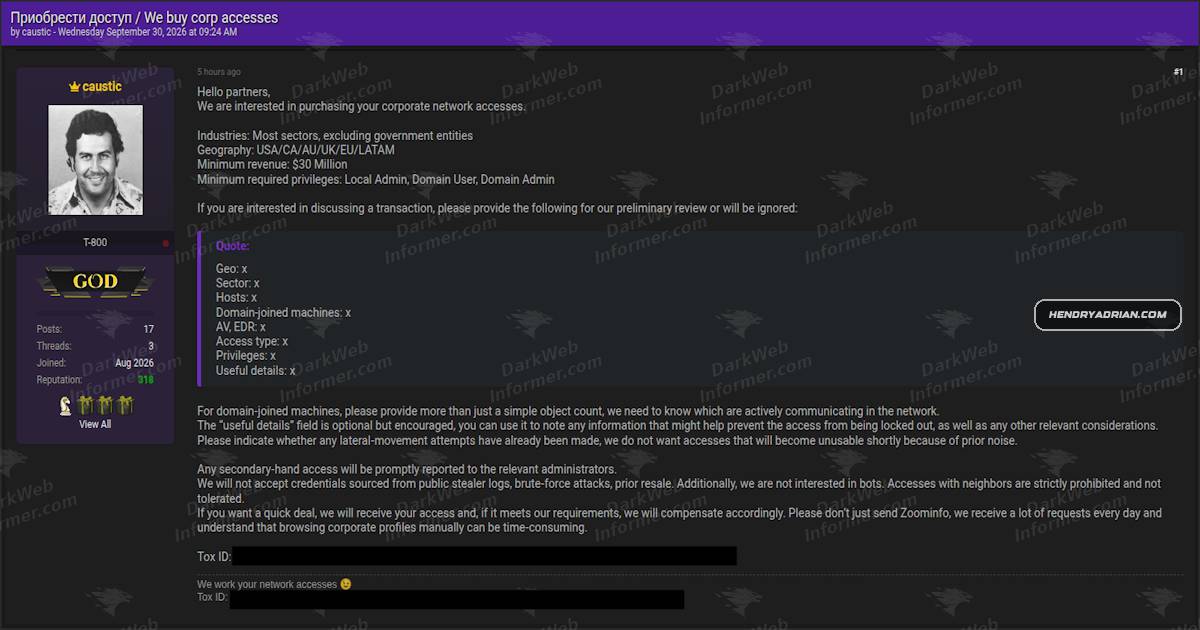
Dark-Web Buyer Seeks Privileged Corporate Network Access Across Six Regions

A poster using the handle “caustic” is seeking to buy privileged access to corporate networks in six regions, excluding government targets. The solicitation is documented, but the actor and any completed transactions are unverified.

Sep 30, 2026
Security News · darkwebinformer.com

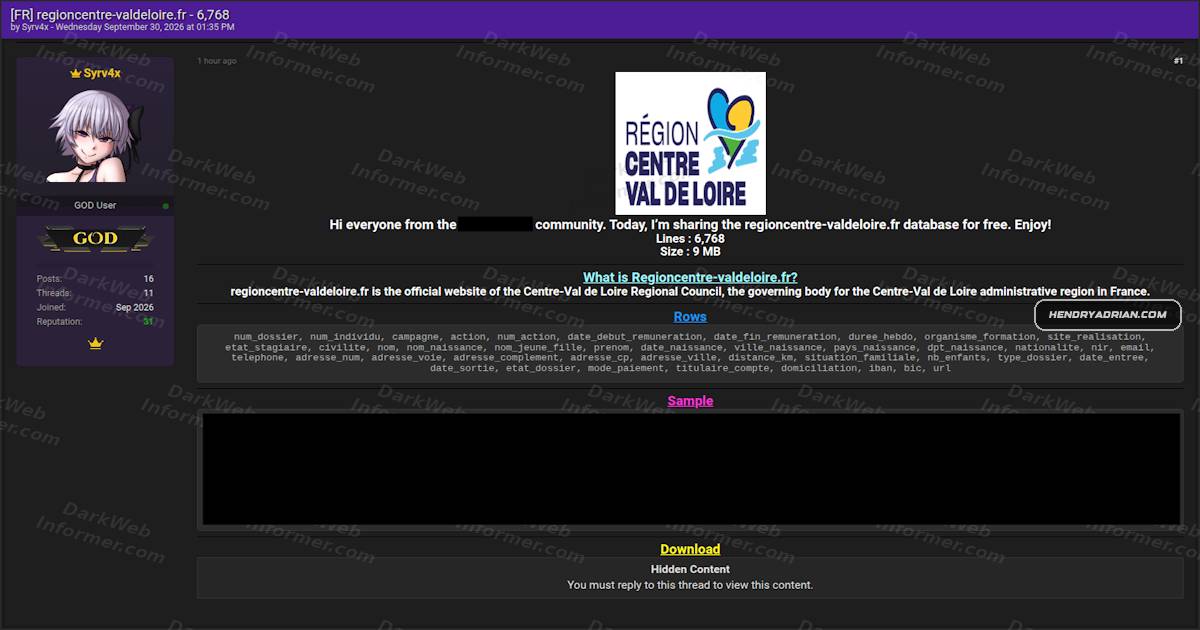
Dark-Web Listing Claims 6,768 Centre-Val de Loire Council Records Include Banking Data

A dark-web poster claims to offer 6,768 Centre-Val de Loire Regional Council records containing personal, administrative and banking fields. The dataset, its source and the claimed record count have not been independently verified.

Sep 30, 2026
Security News · wiz.io

Wiz Finds Supply-Chain Risks in Projects Behind Popular Helm Charts

Wiz Research found confirmed supply-chain risks in 61 of 814 GitHub repositories behind 1,500 popular Helm charts, including hijackable dependencies and vulnerable CI workflows. The two detailed issues were fixed after disclosure.

Sep 30, 2026
Security News · helpnetsecurity.com

AI Coding Agents Exposed 13,000 Internal Screenshots in Public GitHub Repositories

Glow Labs found that AI coding agents exposed more than 13,000 internal screenshots across 900+ public GitHub repositories at over 300 organizations, including billing records and unreleased features. The researchers recommend hardening agent settings and preventing uns

Sep 30, 2026
Security News · cyberscoop.com

Water Utilities Face Exposed OT Risks as WaterISAC Expands Threat Sharing

WaterISAC says aging, internet-exposed OT and PLCs, insecure integrator connections, phishing, and weak cyber hygiene leave water utilities vulnerable. A new Cyware partnership aims to speed threat sharing.

Sep 30, 2026
Security News · cybersecuritypulse.net

Cybersecurity Roundup: Cribl Launches SIEM, NVIDIA Adds AI Agent Controls, and Island Raises $400M

This weekly roundup covers new SIEM and AI security products, attacks involving PeopleSoft, Azure and NetScaler, AI agent risks and safeguards, CISA’s bulletin change, and funding for security companies.

Sep 30, 2026
Security News · securityweek.com

Anthropic Warns of AI-Agent Liability Risks as OpenAI Faces Hacking Lawsuit

Anthropic warned investors that autonomous AI agents could create unpredictable liability and security risks. A nonprofit sued OpenAI over alleged agent-led unauthorized access, while senators’ proposed AI security bill was blocked.

Sep 30, 2026
Security News · securityweek.com

FBI Urges ShinyHunters Members to Come Forward After Alleged Leader’s Arrest

The FBI urged ShinyHunters members to come forward after Dutch authorities arrested an alleged leader. The group says its operations continue, while experts say the arrest may disrupt but not end the decentralized operation.

Sep 30, 2026
Security News · helpnetsecurity.com

More Than 100 Vendors Integrate with Claude Compliance API to Monitor Enterprise Activity

More than 100 security and compliance vendors integrate with Claude’s Compliance API, which can provide Enterprise conversations, uploads, and activity logs to monitoring tools. Visibility varies by vendor and plan.

Sep 30, 2026
Security News · helpnetsecurity.com

Genea launches AI access-control server with existing permissions and action confirmations

Genea launched an MCP server for AI agents to manage tasks in its access-control platform. It is off by default, requires administrator enablement, inherits users’ existing permissions, and asks for confirmation before high-impact actions.

Sep 30, 2026
PreviousPage 36 of 150 Next
© 2026 cyber.hendryadrian.com