Dark-Web Buyer Seeks Privileged Corporate Network Access Across Six Regions
Summary
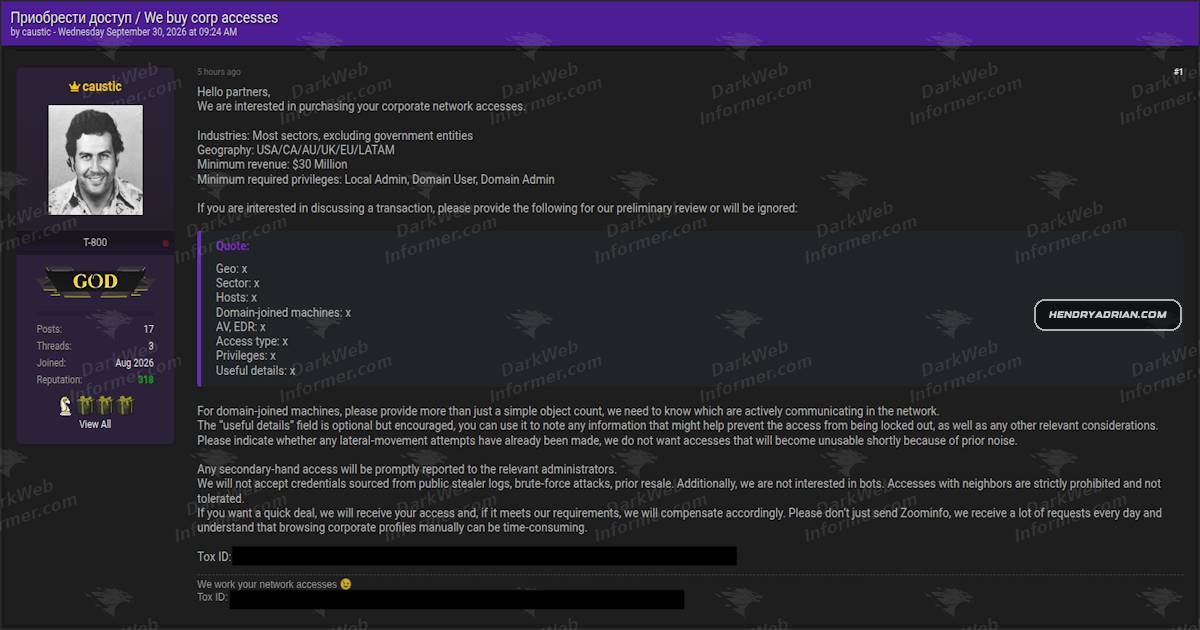
A poster using the handle “caustic” is seeking to buy privileged access to corporate networks in six regions, excluding government targets. The solicitation is documented, but the actor and any completed transactions are unverified.
Key points
- The post seeks Local Administrator, Domain User, or Domain Administrator access to corporate networks; it does not specify an access vector.
- Target regions are the United States, Canada, Australia, the United Kingdom, the European Union, and Latin America; government entities are excluded.
- The buyer sets a $30 million minimum company revenue threshold and requests details including host counts, domain-joined systems, AV/EDR products, and any lateral-movement history.
- The poster rejects public stealer-log credentials, brute-forced or previously resold access, and bot access.
- If valid access is acquired, it could enable further activity such as lateral movement, data theft, extortion, or ransomware deployment.
- The screenshot documents the solicitation, but the actor’s identity, purchasing capability, and any resulting transactions have not been independently verified.
Article Details
- Event Type
- Observed solicitation to purchase privileged access to corporate networks
- Impact
- No completed purchase or intrusion was verified. If valid access were purchased, it could provide a foothold for credential abuse, lateral movement, data theft, extortion, or ransomware deployment.
MITRE ATT&CK
Threat Actors
Countries
AustraliaThe post says most industries are in scope except government entities and lists the United States, Canada, Australia, United Kingdom, European Union and Latin America as target geographies.CanadaThe post says most industries are in scope except government entities and lists the United States, Canada, Australia, United Kingdom, European Union and Latin America as target geographies.United KingdomThe post says most industries are in scope except government entities and lists the United States, Canada, Australia, United Kingdom, European Union and Latin America as target geographies.United StatesThe post says most industries are in scope except government entities and lists the United States, Canada, Australia, United Kingdom, European Union and Latin America as target geographies.