Microsoft to Block External Script Injection in Entra ID Sign-Ins Starting in October
Summary
Microsoft will enforce CSP rules for browser-based Entra ID sign-ins starting in mid-October 2026, allowing only trusted Microsoft-hosted scripts. Customers should stop using code-injecting browser tools; rollout is expected to finish by late October.
Key points
- The update adds Content Security Policy (CSP) enforcement to browser-based Entra ID sign-ins, blocking unauthorized external scripts.
- Only scripts from trusted Microsoft CDN domains will be allowed during authentication.
- Microsoft expects the rollout to begin in mid-October 2026 and finish by late October; the change is enabled by default and requires no tenant configuration.
- Microsoft advises customers to stop using browser extensions or tools that inject code into sign-in pages and to test sign-in flows for dependencies.
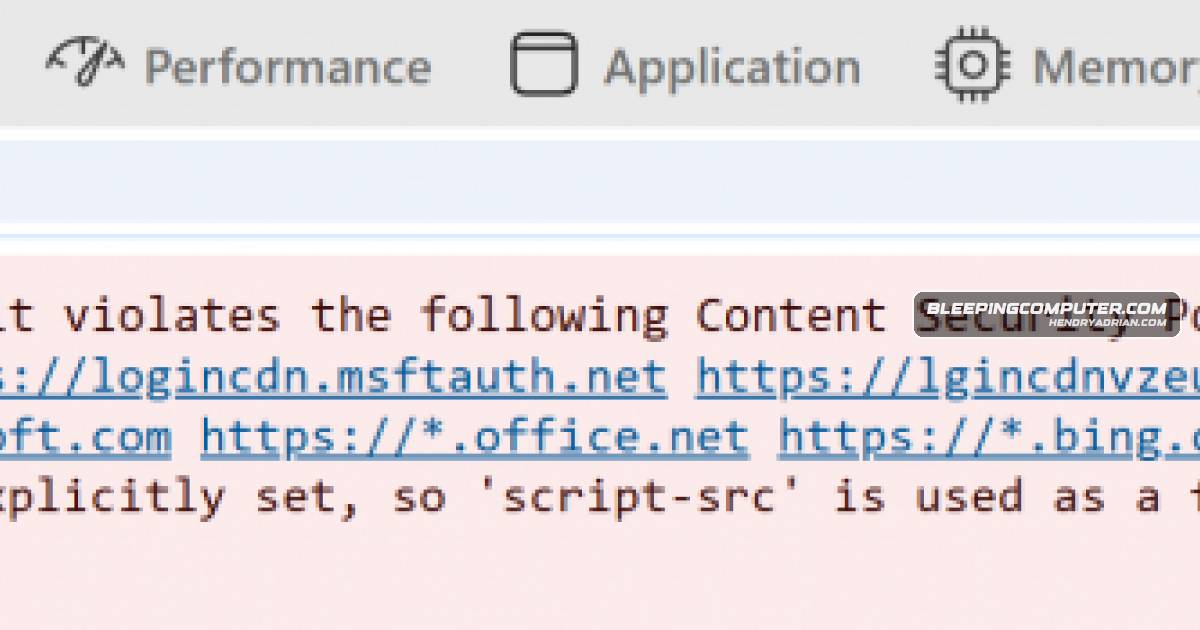
- Administrators can use browser developer-console CSP violation messages to identify blocked scripts.
- MSAL and API-based authentication flows are not affected; enforcement applies to browser-based sign-ins at login[.]microsoftonline[.]com.
Article Details
- Event Type
- Microsoft Entra ID security update adding Content Security Policy enforcement against external script injection during browser-based sign-ins.
- Impact
- The policy will allow only trusted Microsoft-hosted scripts during Entra ID browser sign-ins, blocking unauthorized or externally injected scripts and reducing risks such as cross-site scripting and credential theft. Microsoft says sign-in remains available if unsupported script-injection tools stop working; Microsoft Authentication Library and API-based authentication flows are unaffected.
Vendors
Products
Entra IDMicrosoft says Entra ID will gain stronger protection against external script injection attacks, with new Content Security Policy rules starting in mid-October 2026.Microsoft 365 Apps for EnterpriseAs part of the same initiative, Microsoft also disabled all ActiveX controls in Windows versions of Microsoft 365 and Office 2024 apps, and it updated Microsoft 365 security defaults to block access to Office,Microsoft Authentication Library (MSAL)“Microsoft Authentication Library (MSAL) and API-based authentication flows are not affected because CSP enforcement applies only to browser-based sign-in experiences using login.microsoftonline.com.”Microsoft OneDrive2024 apps, and it updated Microsoft 365 security defaults to block access to Office, SharePoint, and OneDrive files via legacy authentication protocols.Microsoft SharePoint365 and Office 2024 apps, and it updated Microsoft 365 security defaults to block access to Office, SharePoint, and OneDrive files via legacy authentication protocols.Office 2024same initiative, Microsoft also disabled all ActiveX controls in Windows versions of Microsoft 365 and Office 2024 apps, and it updated Microsoft 365 security defaults to block access to Office, SharePoint, and