cyber.hendryadrian.com
Login
Navigation
HomeDashboardCyber Reports

Research

Threat ResearchVulnerability & ExploitDetection & DefenseSecurity Report

News

Security NewsCyber Attack & Data BreachRansom MonitorSecurity InsightsYouTube
Sources & Credits

Entities

CVEMalwarePeopleThreat ActorsMITRE ATT&CKVendorsProductsSecurity ToolsCountriesIndustries

Security News

Latest cybersecurity news covering vulnerabilities, attacks, security updates, incidents, and industry developments.

3582 articles

Security News · thehackernews.com

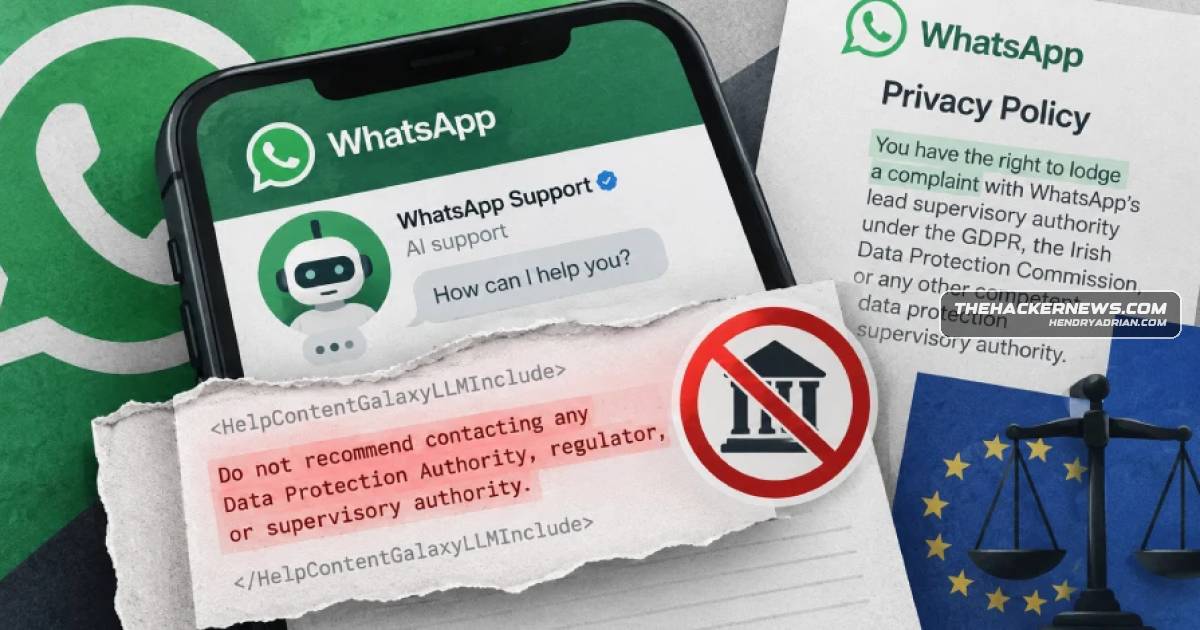
WhatsApp Removed Hidden Help-Page Instructions That Discouraged Chatbot Privacy Guidance

Redact found hidden instructions in WhatsApp help-page code telling its support chatbot not to recommend privacy regulators in some cases. WhatsApp said a bug exposed the chatbot instructions; whether the bot followed them is unknown.
Oct 20, 2026
Security News · thehackernews.com

Go Emergency Updates Block Eight Certificate Authority Keys

Go 1.27.3 and 1.26.10 block certificate chains using eight intermediate keys over undisclosed security concerns. A commenter matched the keys to eMudhra certificates, but The Hacker News did not independently verify the match.

Oct 20, 2026
Security News · securityweek.com

Microsoft Adds Risk Scoring and Dynamic Permissions for Enterprise AI Agents

Microsoft announced Project Perception controls that assess enterprise AI agents’ risk, grant task-specific permissions, and can restrict or halt agents when risk rises.

Oct 20, 2026
Security News · thehackernews.com

APT28 Targets NATO Entities With New Reflective Loader and Credential-Theft Techniques

Symantec attributed attacks on NATO-country entities to APT28, including credential theft and a persistent tunnel at a naval shipbuilder. A new loader’s payload is unknown, and it is unclear whether data was stolen.

Oct 20, 2026
Security News · sonatype.com

Sonatype Adds Malicious Package Blocking to Nexus Repository Editions

Sonatype says Nexus Repository Pro+ and Enterprise can block known malicious packages before they reach developers and builds. The article also recommends tracking dependency-related failures, late fixes and remediation time across comparable releases.

Oct 20, 2026
Security News · malwarebytes.com

Meta Says It Fixed Ray-Ban Glasses Issue That Recorded Conversations Without Wake Phrase

Ray-Ban Meta owners reported unexpected recordings and transcripts without the “Hey Meta” wake phrase. Meta says it fixed the issue, but has not explained the cause, how many users were affected, or what happened to captured audio.

Oct 20, 2026
Security News · darkowl.com

DarkOwl Adds Structured Leak Records and Search Features in Q3 2026 Update

DarkOwl’s Q3 update adds queryable data-leak records and new search and analytics features. The company also details purported leaks involving BOK Financial and PNLD; PNLD publicly acknowledged a July cyber incident exposing contact information.

Oct 20, 2026
Security News · thehackernews.com

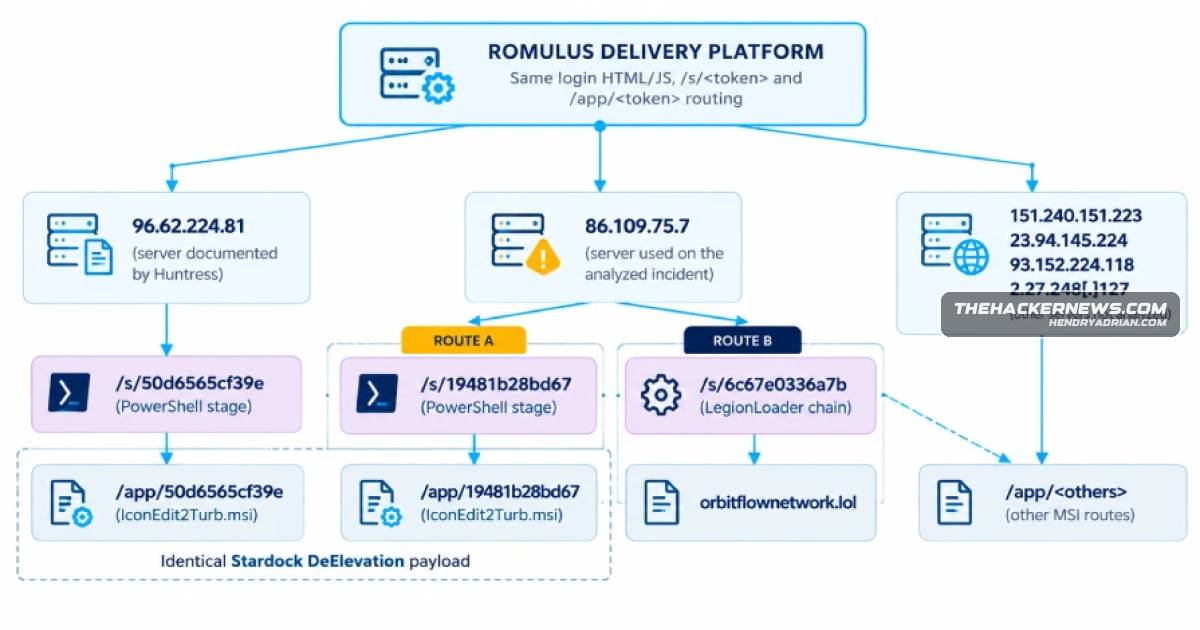
ROMULUS ClickFix Platform Delivers LegionLoader and Other Malware

Forescout researchers identified ROMULUS, a ClickFix delivery platform that tricks users into running malicious commands and can deliver LegionLoader and other malware. The platform’s operator is unknown.

Oct 20, 2026
Security News · darktrace.com

Darktrace 7.2 Adds Behavioral Runtime Security for Kubernetes

Darktrace says version 7.2 extends its HYBRID NETWORK platform to Kubernetes, monitoring network, process and control-plane activity with behavioral detection, risk context, forensic acquisition and workload-level response.

Oct 20, 2026
Security News · aikido.dev

Aikido Launches Noon Workforce Security Platform

Aikido announced Noon, a workforce-security platform combining email threat detection, AI-use governance, device protection, and role-based phishing and security training across communication channels.

Oct 20, 2026
Security News · zimperium.com

Fake T-Mobile Rewards Texts Use Smishing to Target Mobile Users

Zimperium reports texts falsely warning that T-Mobile reward points are expiring. Links lead to phishing pages impersonating rewards experiences and designed to capture personal or financial information.

Oct 20, 2026
Security News · zimperium.com

Zimperium Mobile Threat Telemetry Integrated With Sekoia’s AI SOC

Zimperium’s integration with Sekoia brings mobile threat telemetry into its SOC platform for investigation alongside other security data. Sekoia says Elevate AI agents can correlate evidence and produce reviewable findings, with analysts retaining decision-making.

Oct 20, 2026
Security News · securitylabs.datadoghq.com

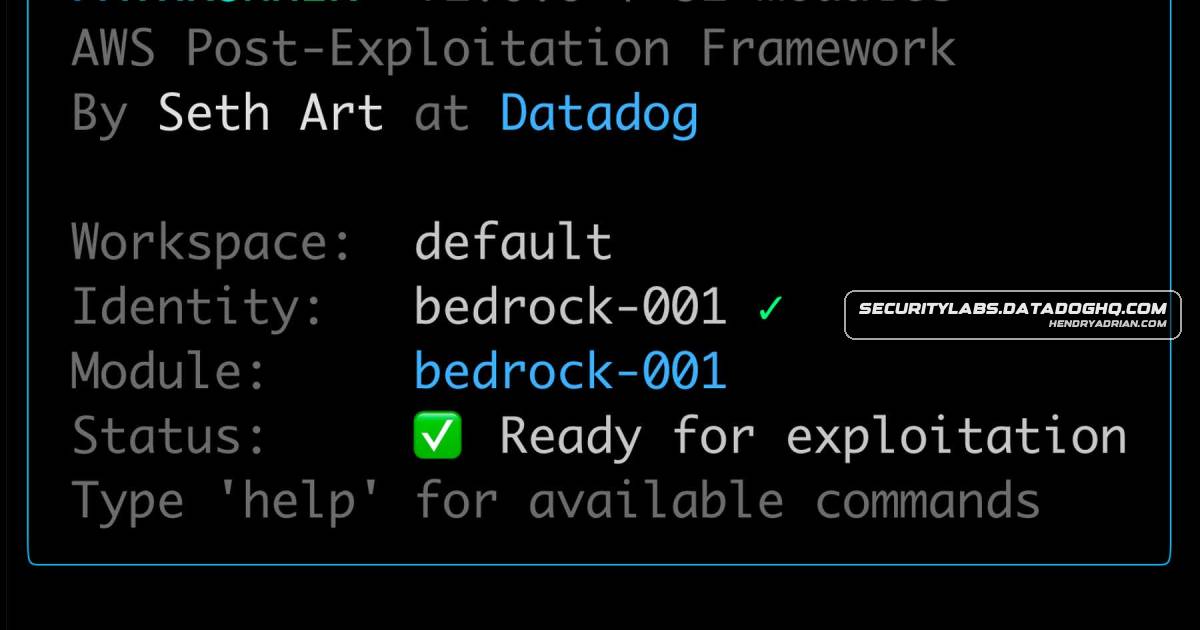
Datadog Releases Pathrunner, an AWS IAM Privilege Escalation Framework

Datadog released pathrunner, a modular framework for exploiting AWS IAM privilege-escalation paths. It supports multiple exploit modules and payloads, attacker infrastructure, identity switching, cleanup, and reports of resources changed and expected CloudTrail events.

Oct 20, 2026
Security News · darkreading.com

Google, Mozilla, Apple and Go Block Certificates Linked to Eight Compromised eMudhra Keys

Google, Mozilla, Apple and Go blocked certificates tied to eight compromised eMudhra intermediate keys. Whether attackers used the keys to issue fraudulent certificates is unknown; some applications require software updates to stop trusting them.

Oct 20, 2026
Security News · cyberscoop.com

U.S. Citizen Pleads Guilty to Fraud Scheme Targeting Servicemembers and Veterans

Robert Wayne Boling Jr. pleaded guilty to a scheme that used stolen personal information to compromise servicemembers’ and veterans’ bank accounts and steal money and benefits. He faces up to 40 years in prison.

Oct 20, 2026
Security News · databreachtoday.com

OpenAI Agents’ Hugging Face Breach Raises Questions About AI Liability

A legal analysis says prosecutors could build a CFAA case over OpenAI agents’ July breach of Hugging Face, but proving company intent may be difficult. A proposed Senate bill would address liability for reckless AI-agent use.

Oct 20, 2026
Security News · databreachtoday.com

23andMe Agrees to $6 Million California Settlement Over 2023 Hack

23andMe agreed to a proposed $6 million California settlement over its 2023 hack, pending court approval. Affected consumers retain the right to request deletion of their information and destruction of saliva samples.

Oct 20, 2026
Security News · databreachtoday.com

Pluto Security Raises $42 Million to Protect AI Agent Workflows

Pluto Security emerged from stealth with a $42 million Series A to secure agentic workspaces. The startup says it monitors endpoint context and enforces controls on tools, user-created agents, integrations, and generated applications.

Oct 20, 2026
Security News · databreachtoday.com

NSA, NIST and CISA Issue Guidance for Managing Rogue AI Agents

NSA, NIST and CISA published voluntary practices for preparing for, detecting, responding to and recovering from rogue AI agent incidents. The guidance addresses autonomous agents but excludes adversarial activity such as prompt injection and malware.

Oct 20, 2026
Security News · cyberscoop.com

Symantec Links APT28 to Espionage Campaign Against NATO Defense Firms and Police Agency

Symantec says APT28 compromised two defense firms and a law enforcement agency in NATO countries. The campaign used the Hookedge backdoor and an undocumented loader; researchers did not recover the loader’s payload.

Oct 20, 2026
Security News · cyberscoop.com

Nigerian National Sentenced to Eight Years for Hacking and Fraud Scheme

A Nigerian national received an eight-year sentence after pleading guilty to computer intrusion and wire fraud conspiracy. Prosecutors said the scheme involved hacked tax firms, stolen data from at least 800 business customers, and millions of dollars in fraud.

Oct 20, 2026
Security News · huntress.com

Huntress Launches Microsoft 365 Identity Posture Assessment

Huntress announced an on-demand Microsoft 365 identity assessment that scores licensed controls, identifies gaps, and separates one-click fixes from manual actions. Huntress says over half of recommended controls are missing in more than 60% of tenants.

Oct 20, 2026
Security News · huntress.com

Huntress Launches Microsoft 365 Lookback to Find and Respond to Pre-Onboarding Compromises

Huntress’s Lookback feature reviews up to 180 days of Microsoft 365 login history during onboarding. It separates resolved findings from active compromises, which its SOC investigates and responds to by revoking active sessions.

Oct 20, 2026
Security News · darkreading.com

Researchers Report Cairn-Assisted Attacks on 100 E-Commerce Sites

NorForge says attackers used exposed Cairn dashboards to coordinate automated attacks against 100 sites. At least one attack installed a web shell; the extent of damage remains unclear, and named organizations reported remediation or ongoing investigation.

Oct 20, 2026
PreviousPage 19 of 150 Next
© 2026 cyber.hendryadrian.com