
Datadog Releases Pathrunner, an AWS IAM Privilege Escalation Framework
Summary
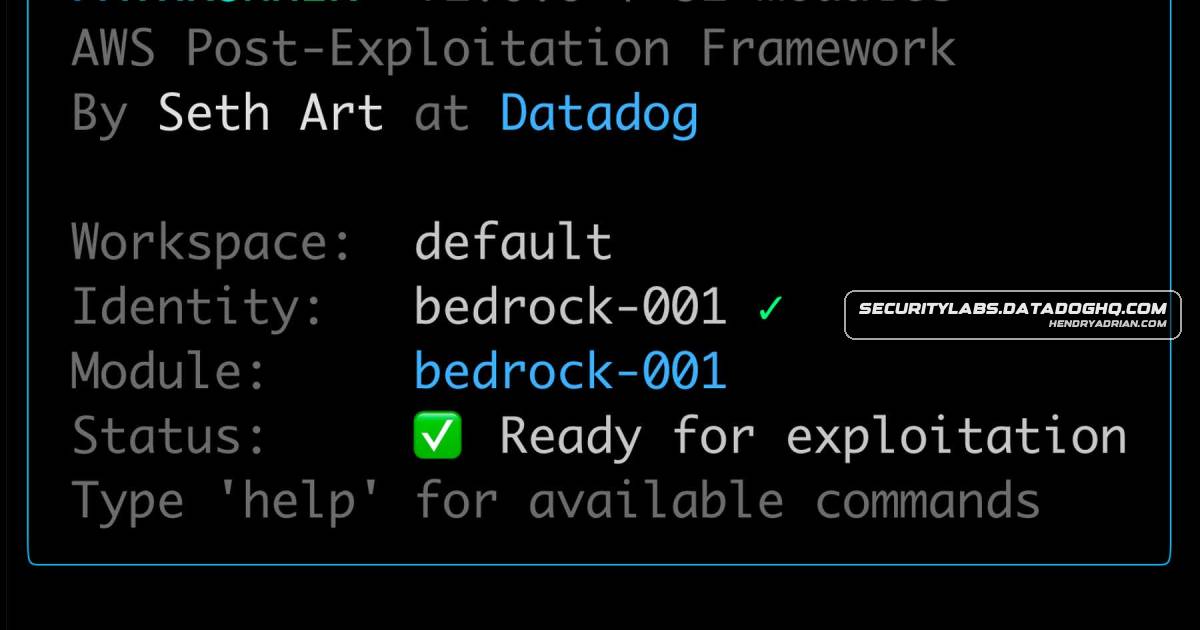
Datadog released pathrunner, a modular framework for exploiting AWS IAM privilege-escalation paths. It supports multiple exploit modules and payloads, attacker infrastructure, identity switching, cleanup, and reports of resources changed and expected CloudTrail events.
Key points
- Pathrunner automates exploitation of AWS IAM privilege-escalation paths cataloged by Datadog.
- It lets operators import and switch between AWS identities, select exploit modules, and capture credentials for target identities.
- The framework supports multiple payloads per module, which Datadog says can help defenders evaluate detections for different post-exploitation actions.
- Operators can configure a separate AWS account to host attacker infrastructure and collect credentials through a remote listener.
- Pathrunner can generate a workspace report listing resources created or modified, cleanup commands, and expected CloudTrail events with timestamps.
- Datadog says pathrunner had more than 80 exploit modules as of October 2026.
Article Details
- Event Type
- Release of pathrunner, a modular cloud-native offensive security framework for AWS IAM privilege-escalation testing.
- Impact
- The framework automates exploitation of AWS IAM privilege-escalation paths and can help defenders assess the impact of misconfigurations, test detections, and review generated CloudTrail events. It also supports deploying attacker infrastructure in an AWS account controlled by the operator. The article describes a security-testing tool, not a reported incident or victim impact.