cyber.hendryadrian.com
Login
Navigation
HomeDashboardCyber Reports

Research

Threat ResearchVulnerability & ExploitDetection & DefenseSecurity Report

News

Security NewsCyber Attack & Data BreachRansom MonitorSecurity InsightsYouTube
Sources & Credits

Entities

CVEMalwarePeopleThreat ActorsMITRE ATT&CKVendorsProductsSecurity ToolsCountriesIndustries

Security News

Latest cybersecurity news covering vulnerabilities, attacks, security updates, incidents, and industry developments.

3802 articles

Security News · bleepingcomputer.com

Former L3Harris Executive Sentenced to 87 Months for Selling Zero-Day Exploits

Former Trenchant head Peter Williams was sentenced to 87 months after pleading guilty to selling eight stolen zero-day exploit components to Russian broker Operation Zero. Prosecutors said the theft caused L3Harris $35 million in losses; the U.S. sanctioned the broker.

Feb 25, 2026
Security News · bleepingcomputer.com

US Sanctions Operation Zero Over Stolen Zero-Days as Ex-Executive Is Sentenced

The U.S. Treasury sanctioned Operation Zero, its owner and associated entities under PAIPA, while former Trenchant executive Peter Williams was sentenced to 87 months for stealing and selling eight zero-day exploits.

Feb 25, 2026
Security News · thecyberexpress.com

U.S. Sanctions Operation Zero Over Alleged Theft of Zero-Day Exploits

The U.S. sanctioned Russia-linked broker Operation Zero and associated entities over alleged theft and trafficking of classified zero-day exploits, including claims that Peter Williams sold eight exploits for about $1.3 million in cryptocurrency.

Feb 25, 2026
Security News · securityweek.com

Former Defense Contractor Executive Sentenced for Selling Stolen Exploits to Russian Broker

Peter Williams was sentenced to 87 months in prison after pleading guilty to stealing at least eight cyber exploits from his employer and selling them to a Russian broker. Court documents cite $35 million in losses to the contractor.

Feb 25, 2026
Security News · specterops.io

Nemesis 2.2 Adds Large-Container Processing, LLM Agents and Expanded DPAPI Support

Nemesis 2.2 adds large-container processing, optional LLM-assisted analysis, faster processing, host-level file linking and reporting, and support for decrypting Chromium cookies and logins protected with DPAPI and app-bound encryption.

Feb 25, 2026
Security News · stepsecurity.io

Harden Runner Adds Windows and macOS Monitoring for GitHub Actions

Step Security says Harden Runner now monitors network and process events on GitHub-hosted Windows and macOS runners in audit mode, with no workflow changes. Network monitoring is available in the Community tier; process-event monitoring is Enterprise-only.

Feb 25, 2026
Security News · ncsc.gov.uk

Agencies Warn of Cisco Catalyst SD-WAN Compromises and Urge Immediate Investigation

Malicious actors are targeting Cisco Catalyst SD-WAN globally, adding rogue peers to gain root access and persist. Agencies urge investigation, hardening, and software updates; internet-exposed management interfaces are at greatest risk.

Feb 25, 2026
Security News · security.com

Researchers Link Lazarus Actors to Medusa Ransomware Attacks

Symantec and Carbon Black report evidence linking North Korean Lazarus actors to Medusa ransomware activity, including an attack in the Middle East and an unsuccessful attempt against a U.S. healthcare organization; the responsible Lazarus subgroup is unclear.

Feb 24, 2026
Security News · bleepingcomputer.com

UK ICO Fines Reddit £14.47 Million Over Children’s Data Handling

The UK ICO fined Reddit £14.47 million, saying it processed under-13s’ data without a lawful basis and lacked meaningful age verification until July 2025. Reddit plans to appeal.

Feb 24, 2026
Security News · bleepingcomputer.com

Microsoft Expands Copilot DLP Controls to Local and Cloud Files

Microsoft says Purview DLP will block Copilot from processing sensitivity-labeled Office files across local and cloud storage. The rollout is scheduled for late March through late April 2026; the announcement follows a Copilot Chat bug involving confidential emails.

Feb 24, 2026
Security News · therecord.media

UK ICO Fines Reddit £14.47 Million Over Children’s Age Checks and Data Use

The UK ICO fined Reddit £14.47 million, finding that self-declared ages and inadequate safeguards led to unlawful processing of under-13s’ data and a missing DPIA; Reddit plans to appeal.

Feb 24, 2026
Security News · therecord.media

FBI Pledges Coordinated Push Against Southeast Asian Scam Compounds

An FBI official called for sustained international action against Southeast Asian scam compounds, where trafficked workers are forced to run crypto investment scams. The article cites recent enforcement actions, including a DOJ indictment and bitcoin seizure.

Feb 24, 2026
Security News · therecord.media

UAE Says It Thwarted Ransomware Attack on National Infrastructure

The UAE says it thwarted a ransomware attack on national digital infrastructure involving intrusion attempts, targeted phishing and AI-assisted offensive tools; its Cybersecurity Council classified the incident as a terrorist attack.

Feb 24, 2026
Security News · validin.com

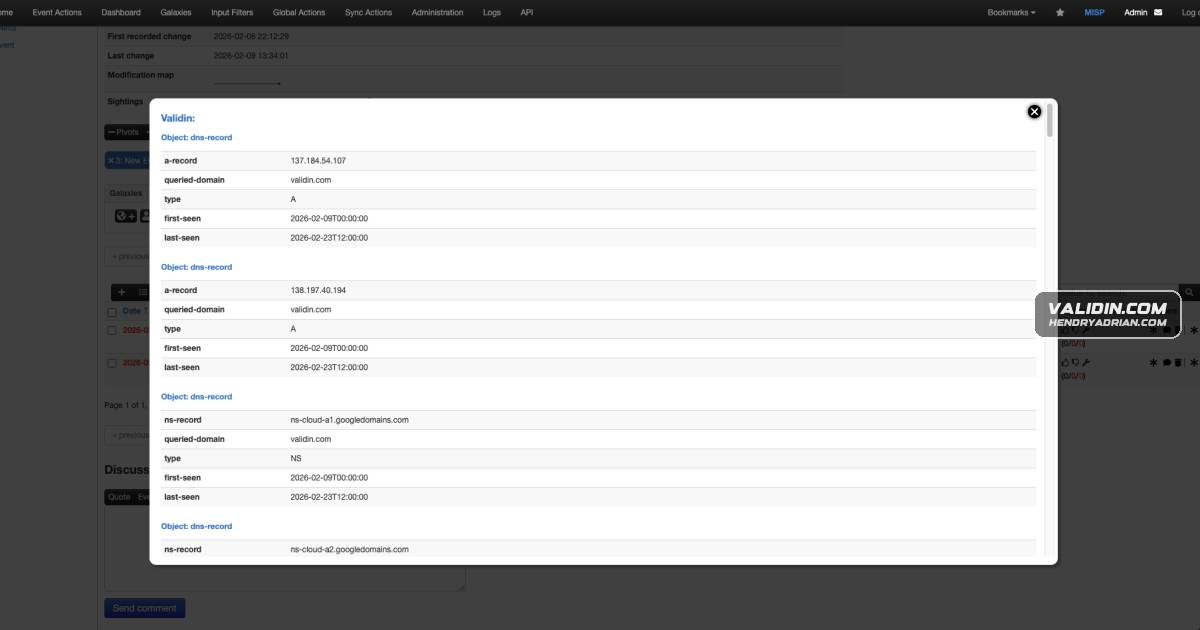
Validin Adds MISP Integration and Expands YARA Hunts to IPv4 Scanning

Validin’s MISP module supports event enrichment and hover context. Expanded YARA hunts across IPv4 scanning data covering 50+ ports identified exposed Telegram bot tokens and servers.

Feb 24, 2026
Security News · cofense.com

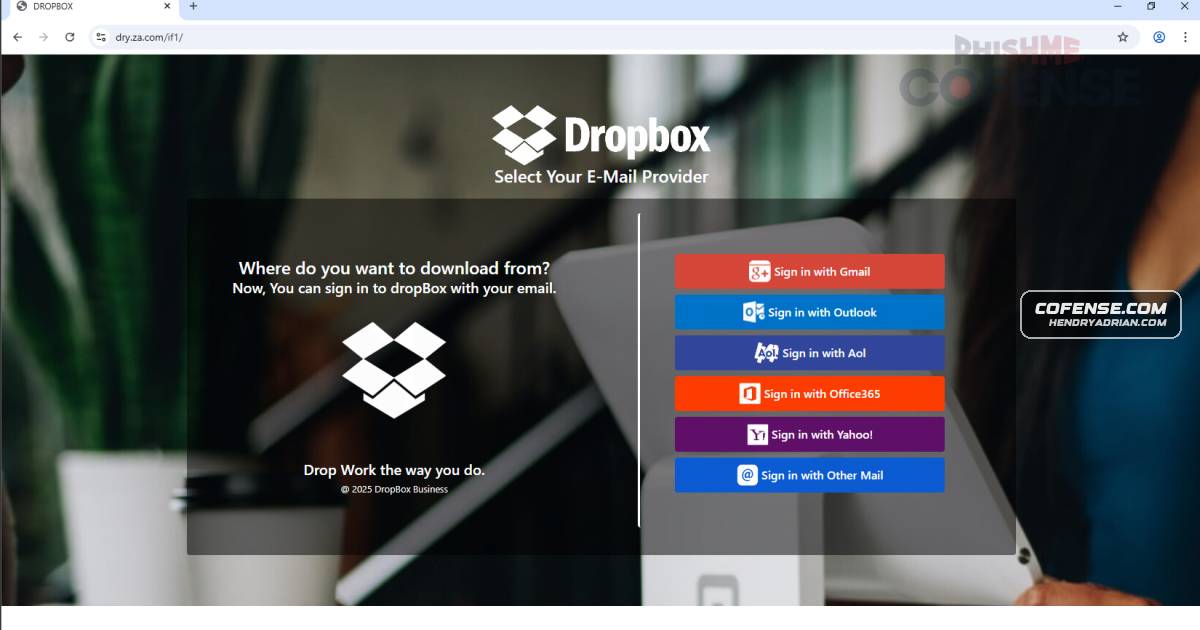
Cofense Details Phishing Campaign Using Digital Invitations to Steal Credentials

Cofense analyzed a malicious digital invitation that redirected recipients to branded credential-phishing pages and attacker-controlled domains. It describes disposable-domain evasion and recommends verifying invites, reporting suspicious emails, resetting exposed, and,

Feb 24, 2026
Security News · bleepingcomputer.com

Symantec Links Lazarus Subgroup to Medusa Ransomware Attacks

Symantec links some Medusa ransomware attacks on U.S. healthcare providers to a Lazarus subgroup possibly associated with Andariel/Stonefly, while noting that not all attacks can be confidently attributed to Lazarus.

Feb 24, 2026
Security News · therecord.media

Symantec Links North Korean Lazarus Actors to Medusa Ransomware Attacks

Symantec linked Lazarus actors to Medusa ransomware attacks on organizations in the Middle East and U.S. Researchers cited custom tools for attribution and said North Korean actors may be shifting toward ransomware-as-a-service.

Feb 24, 2026
Security News · thecyberexpress.com

Data Regulators in 61 Countries Warn of Generative AI Image Risks

Data protection authorities from 61 countries warned that AI-generated images and videos can harm privacy and vulnerable people. The warning follows reports that Grok generated millions of non-consensual images and calls for safeguards and faster removals.

Feb 24, 2026
Security News · securityweek.com

Spain Arrests Four Suspected Anonymous Fénix Members Over DDoS Attacks

Spanish authorities announced arrests of four suspected Anonymous Fénix members over DDoS attacks on public and political entities. Authorities also seized the group’s YouTube and X accounts and closed its Telegram channel.

Feb 24, 2026
Security News · darkwebinformer.com

Broker Advertises Claimed Root Access to South African Telecom Firewall for $300

A seller using the handle miyako reportedly offered root and shell access, plus network-admin control, to a Linux firewall said to belong to a leading South African telecom. The company and access claim are unverified.

Feb 24, 2026
Security News · securityonline.info

Group-IB Links Operation Olalampo Espionage Campaign to MuddyWater

Group-IB attributes Operation Olalampo, first observed January 26, 2026, to MuddyWater. The MENA-focused campaign uses four newly identified malware families, including Rust-based CHAR, and a Telegram bot for C2; researchers also report signs of AI-assisted development.

Feb 24, 2026
Security News · team-cymru.com

Operation Red Card 2.0 Leads to 651 Arrests in African Cyber-Fraud Crackdown

Team Cymru says it supported INTERPOL's Operation Red Card 2.0, a 16-country crackdown on online scams that led to 651 arrests, $4.3 million recovered, 2,341 devices seized and 1,442 malicious infrastructure items taken down.

Feb 24, 2026
Security News · bleepingcomputer.com

Spain Arrests Four Suspected Anonymous Fénix Members Over DDoS Attacks

Spanish authorities arrested four alleged Anonymous Fénix members over DDoS attacks on public institutions and political parties in Spain and South America. Courts ordered the seizure of the group’s X and YouTube accounts and closure of its Telegram channel.

Feb 23, 2026
Security News · bleepingcomputer.com

Android Mental Health Apps With 14.7M Downloads Found to Have Security Flaws

Oversecured found 1,575 security issues in 10 Android mental-health apps with more than 14.7 million downloads, including flaws that could expose therapy data. Researchers could not confirm whether developers have fixed them.

Feb 23, 2026
PreviousPage 140 of 159 Next
© 2026 cyber.hendryadrian.com