
Validin Adds MISP Integration and Expands YARA Hunts to IPv4 Scanning
Summary
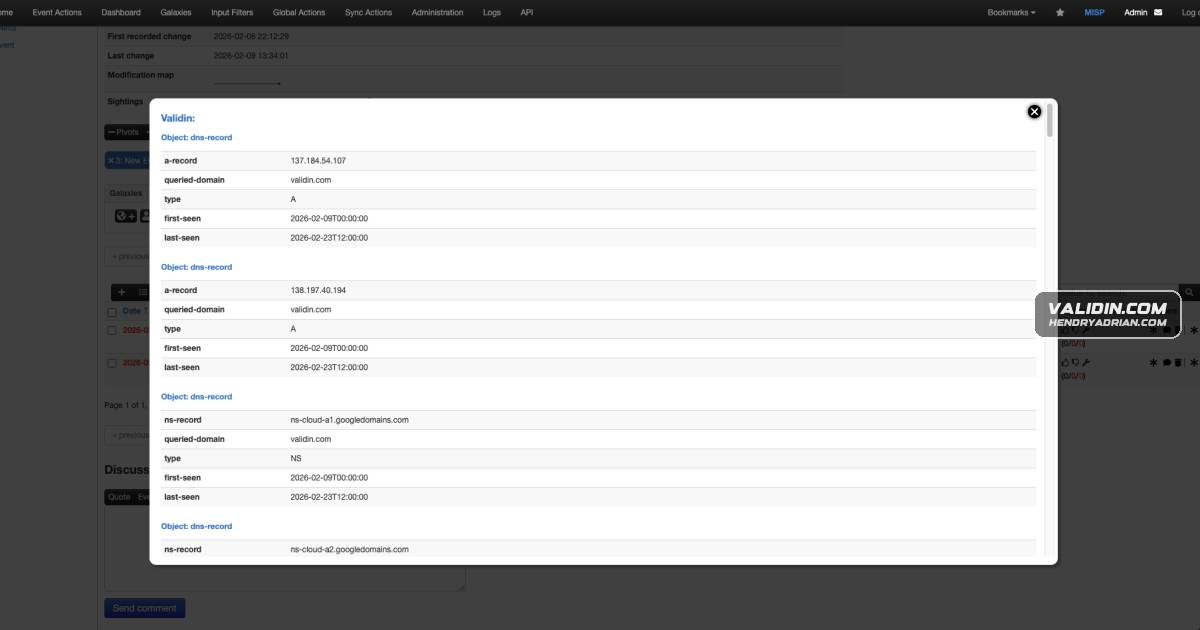
Validin’s MISP module supports event enrichment and hover context. Expanded YARA hunts across IPv4 scanning data covering 50+ ports identified exposed Telegram bot tokens and servers.
Key points
- The MISP expansion module supports domain, hostname, ip-src, and ip-dst attributes, with enrichment and hover modes.
- Enrichment draws on DNS, host-response, registration, certificate, and subdomain data; the article says the module was an open PR in misp-modules as of February 23.
- YARA hunts can now include active IPv4 host-response data, expanding scanning beyond virtual-host ports 80 and 443 to more than 50 security-relevant ports.
- Using a Telegram-token pattern, Validin found exposed Telegram bot servers on ports 8082 and 8083.
- Validin says exposed bot tokens can allow access to bot message history.
- A YARA hunt also identified joegotyou[.]cyou, which the article describes as appearing to be a location-phishing page; Validin says it could not identify related campaigns or infrastructure.
Article Details
- Event Type
- Validin announced a MISP expansion module and expanded YARA hunts to include active IPv4 host-response data.
- Impact
- The expanded scanning covered more than 50 security-relevant ports and helped identify exposed Telegram bot tokens and bot servers on ports 8082 and 8083. Validin also reported finding joegotyou[.]cyou, which it said appeared to be a location-phishing page that sent victims’ coordinates to an attacker.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| DOMAIN | joegotyou[.]cyou | Domain of a page Validin said appeared to be location phishing, sending victims’ coordinates to an attacker. |
Vendors
Products
MISPValidin is available as a MISP expansion module to enrich MISP events across Validin’s DNS, host responses, registration, certificates, and subdomain data sources, with both enrichment and hover modes.ValidinValidin is available as a MISP expansion module to enrich MISP events across Validin’s DNS, host responses, registration, certificates, and subdomain data sources, with both enrichment and hover modes.