cyber.hendryadrian.com
Login
Navigation
HomeDashboardCyber Reports

Research

Threat ResearchVulnerability & ExploitDetection & DefenseSecurity Report

News

Security NewsCyber Attack & Data BreachRansom MonitorSecurity InsightsYouTube
Sources & Credits

Entities

CVEMalwarePeopleThreat ActorsMITRE ATT&CKVendorsProductsSecurity ToolsCountriesIndustries

Security News

Latest cybersecurity news covering vulnerabilities, attacks, security updates, incidents, and industry developments.

3801 articles

Security News · thehackernews.com

Weekly Security Roundup Details Phorpiex Botnet, ActiveMQ RCE and AI-Related Threats

A weekly security roundup details Phorpiex’s hybrid P2P botnet, an ActiveMQ RCE chain, phishing and stealer campaigns, and AI-related prompt-injection risks, alongside vulnerabilities and exposed industrial systems.

Apr 9, 2026
Security News · therecord.media

Russia accuses former Radio Free Europe journalist of aiding cyberattacks

Russia’s FSB says it detained an unnamed former Radio Free Europe freelancer on treason charges, alleging he shared information through an SBU-linked Telegram channel used to aid cyberattacks. The allegations are not independently confirmed.

Apr 9, 2026
Security News · therecord.media

FCC Proposes Stricter Provider Identity Checks and Per-Call Fines to Curb Illegal Robocalls

The FCC is seeking comment on proposed stricter customer identity checks, longer record retention and per-call penalties for voice providers, aiming to curb illegal robocalls and help law enforcement.

Apr 9, 2026
Security News · bleepingcomputer.com

Hijacked Smart Slider 3 Pro Update Delivered Backdoors to WordPress and Joomla Sites

A malicious Smart Slider 3 Pro v3.5.1.35 update distributed April 7 may have affected WordPress and Joomla sites, installing backdoors and stealing credentials. The vendor recommends restoring a pre-April 7 backup or updating to v3.5.1.36 and cleaning affected sites.

Apr 9, 2026
Security News · therecord.media

Treasury to Share Cyber Threat Intelligence With Eligible Crypto Firms

Treasury will provide eligible U.S. digital-asset firms and industry groups the same actionable cyber threat intelligence shared with traditional financial institutions, at no cost; eligibility criteria remain unspecified.

Apr 9, 2026
Security News · thecyberexpress.com

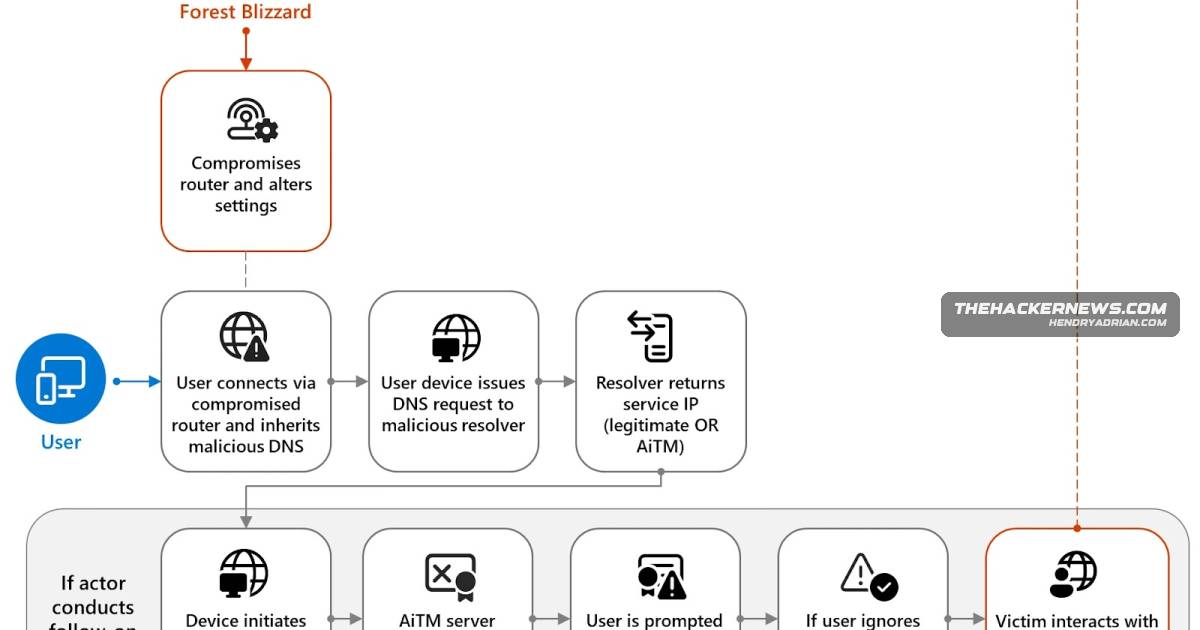
Forest Blizzard Used Compromised SOHO Routers for DNS Hijacking and AiTM Attacks

Forest Blizzard reportedly compromised SOHO routers to redirect DNS queries, affecting more than 200 organizations and 5,000 consumer devices. The campaign enabled monitoring and targeted AiTM attacks; Microsoft said its own systems were not compromised.

Apr 9, 2026
Security News · securityweek.com

Researchers Bypass Apple Intelligence Guardrails Using Prompt Injection

RSAC researchers report combining Neural Execs prompt injection with Unicode manipulation bypassed Apple Intelligence filters in 76% of 100 tests. RSAC says protections rolled out in iOS 26.4 and macOS 26.4; researchers have seen no malicious exploitation.

Apr 9, 2026
Security News · thecyberexpress.com

UNC6783 Targets BPO Providers to Reach Larger Organizations

Google reports that UNC6783 targets BPO providers using phishing, live-chat impersonation and fake updates, with tools that can capture clipboard data and install remote access malware. Mandiant recommends FIDO2 keys and MFA-registration audits.

Apr 9, 2026
Security News · securityweek.com

CloudSEK Finds Android App API Keys Can Expose Gemini Endpoints

CloudSEK says 32 API keys embedded in 22 Android apps can access Gemini resources. Attackers who extract them could access files and cached data or exhaust API quotas; actual misuse or data exposure is not reported.

Apr 9, 2026
Security News · wiz.io

Wiz Adds Security Visibility and Risk Analysis for Vercel Environments

Wiz introduced an integration that maps Vercel projects, domains, teams, members, and firewall configurations into its Security Graph to surface exposure, misconfigurations, and potential attack paths.

Apr 9, 2026
Security News · securityweek.com

Google Warns of UNC6783 Campaign Targeting BPOs for Data Extortion

GTIG warns that UNC6783 targets BPOs and corporate helpdesk staff with phishing, spoofed Okta and Zendesk pages, and a clipboard-stealing kit to bypass MFA. A possible link to Mr. Raccoon and his Adobe data-theft claim remains unconfirmed.

Apr 9, 2026
Security News · bleepingcomputer.com

Microsoft Suspends Open-Source Project Accounts, Blocking Windows Security Updates

Microsoft suspended accounts used by WireGuard, VeraCrypt, MemTest86, and Windscribe, blocking Windows releases and security patches. Microsoft said the suspensions followed incomplete mandatory verification; media coverage prompted outreach to help reinstate accounts.

Apr 9, 2026
Security News · therecord.media

TikTok Removes Six Covert Influence Networks Ahead of Hungary Election

TikTok said it removed six covert influence networks, hundreds of impersonating accounts and thousands of videos ahead of Hungary’s election. Reports described fabricated political narratives and a separate alleged operation targeting the Tisza Party’s IT systems.

Apr 9, 2026
Security News · securityweek.com

Iran-Linked Hackers Say Ceasefire Won’t End Cyberattacks

Handala said it would continue targeting Israel and may resume attacks on the U.S. U.S. agencies warned that Iran-supporting hackers had accessed internet-connected industrial controllers and urged organizations to update security precautions.

Apr 9, 2026
Security News · bleepingcomputer.com

Google: UNC6783 Uses BPO Access to Target High-Value Companies

Google says UNC6783 targets BPO providers with social engineering and phishing to access high-value companies, steal data and extort victims. Its findings include spoofed Okta pages, clipboard theft to bypass MFA and fake updates delivering remote access malware.

Apr 9, 2026
Security News · bleepingcomputer.com

Magento Skimmer Campaign Hides Credit Card Theft in 1×1-Pixel SVGs

Sansec reports a campaign targeting nearly 100 Magento stores with skimmers hidden in 1×1-pixel SVGs. The attackers reportedly use fake checkout forms to steal payment data; Adobe has not released a production fix for PolyShell.

Apr 9, 2026
Security News · bleepingcomputer.com

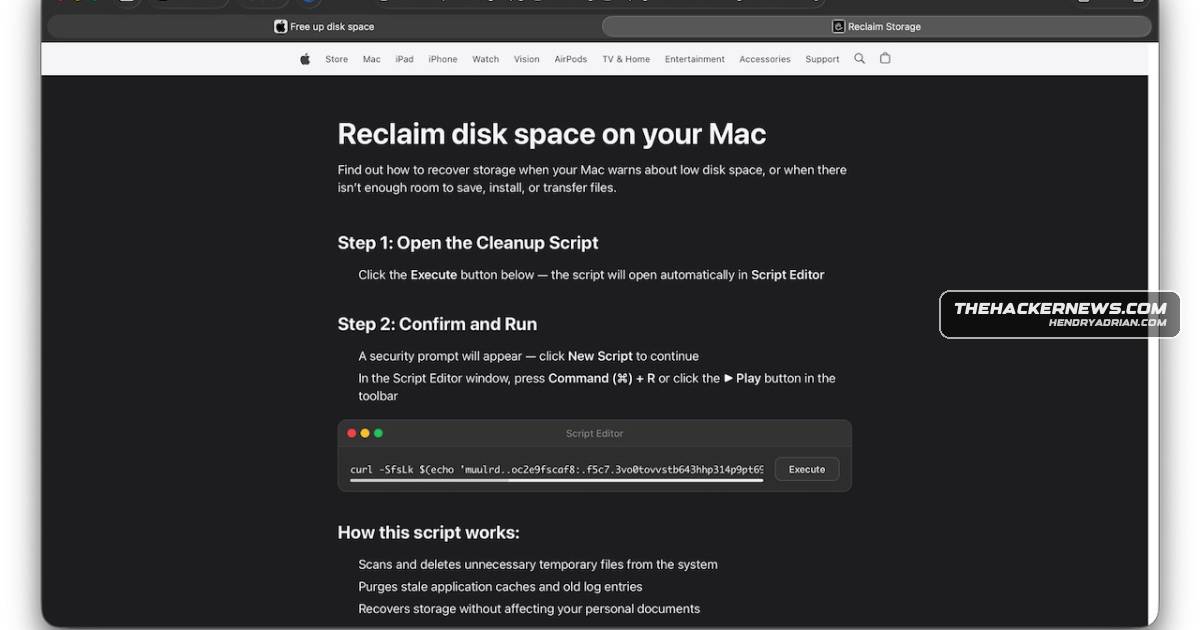
New macOS ClickFix Campaign Uses Script Editor to Deliver Atomic Stealer

Jamf researchers observed fake Apple-themed sites using applescript:// links to launch Script Editor with malicious code that downloads Atomic Stealer, which targets Keychain data, passwords, cookies, browser wallets and other system information.

Apr 8, 2026
Security News · securityonline.info

U.S. Agencies Warn of Iranian-Affiliated Attacks on Internet-Exposed Rockwell PLCs

A U.S. agency advisory reports Iranian-affiliated actors compromising internet-exposed Rockwell PLCs, manipulating HMI/SCADA displays and disrupting operations. It urges operators to remove PLCs from public internet exposure and secure remote access.

Apr 8, 2026
Security News · thecyberexpress.com

FBI Disrupts APT28-Linked Router Network Used for DNS Hijacking

The FBI says Operation Masquerade disrupted the U.S. portion of an APT28-linked network of compromised routers by collecting evidence, resetting DNS settings and blocking renewed access. Authorities recommend updating or replacing vulnerable routers and checking DNS and

Apr 8, 2026
Security News · attackiq.com

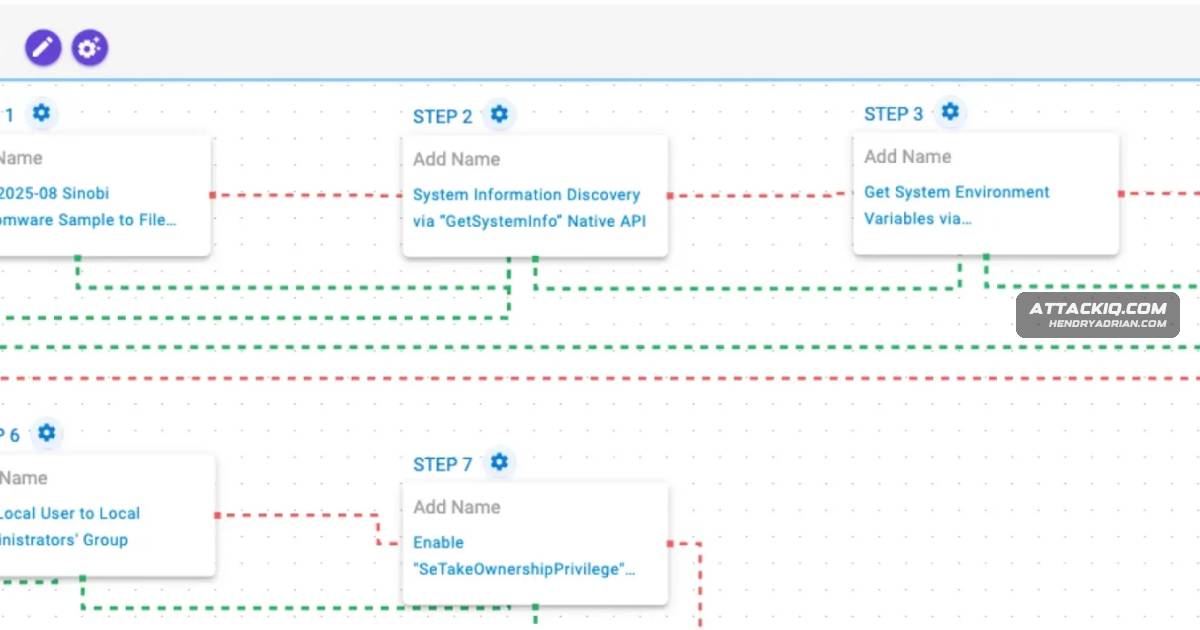
AttackIQ Releases Sinobi Ransomware Emulation for Security Control Validation

AttackIQ released an Adversarial Exposure Validation attack graph emulating Sinobi ransomware behaviors, including discovery, privilege escalation and AES-128/Curve25519 file encryption, to test security controls and response workflows.

Apr 8, 2026
Security News · securityonline.info

Proofpoint Reports TA416 Shift Toward European and Middle Eastern Diplomacy

Proofpoint reports that TA416 resumed targeting European government and diplomatic entities in mid-2025 and expanded into Middle Eastern government and diplomatic targets after the March 2026 Iran conflict, using evolving methods to deliver PlugX.

Apr 8, 2026
Security News · securityweek.com

U.S. Agencies Warn of Iran-Linked PLC Attacks Disrupting Critical Infrastructure

U.S. agencies warn that Iran-linked actors are targeting internet-exposed PLCs across critical infrastructure, with reported disruptions involving PLC project files and manipulated HMI/SCADA displays. They urge organizations to assess OT networks and apply advisory m

Apr 8, 2026
Security News · cisa.gov

U.S. Agencies Warn of Iranian-Affiliated Actors Exploiting PLCs Across Critical Infrastructure

U.S. agencies report Iranian-affiliated actors have targeted internet-facing PLCs since at least March 2026, extracting project files and manipulating HMI/SCADA displays. Some organizations experienced operational disruption and financial loss.

Apr 8, 2026
Security News · thehackernews.com

APT28 Used SOHO Router DNS Hijacking in Global FrostArmada Campaign

Lumen and Microsoft linked APT28/Storm-2754 to FrostArmada, which compromised SOHO routers to redirect DNS traffic and steal credentials via attacker-in-the-middle attacks. Infrastructure was disrupted after activity peaked at 18,000 IPs across 120 countries.

Apr 8, 2026
PreviousPage 120 of 159 Next
© 2026 cyber.hendryadrian.com