
APT28 Used SOHO Router DNS Hijacking in Global FrostArmada Campaign
Summary
Lumen and Microsoft linked APT28/Storm-2754 to FrostArmada, which compromised SOHO routers to redirect DNS traffic and steal credentials via attacker-in-the-middle attacks. Infrastructure was disrupted after activity peaked at 18,000 IPs across 120 countries.
Key points
- Lumen’s Black Lotus Labs named the campaign FrostArmada; Microsoft attributed the activity to APT28, also tracked as Storm-2754.
- The activity began by May 2025, with widespread router exploitation starting in August and more than 18,000 IPs across 120 countries communicating with APT28 infrastructure at its December peak.
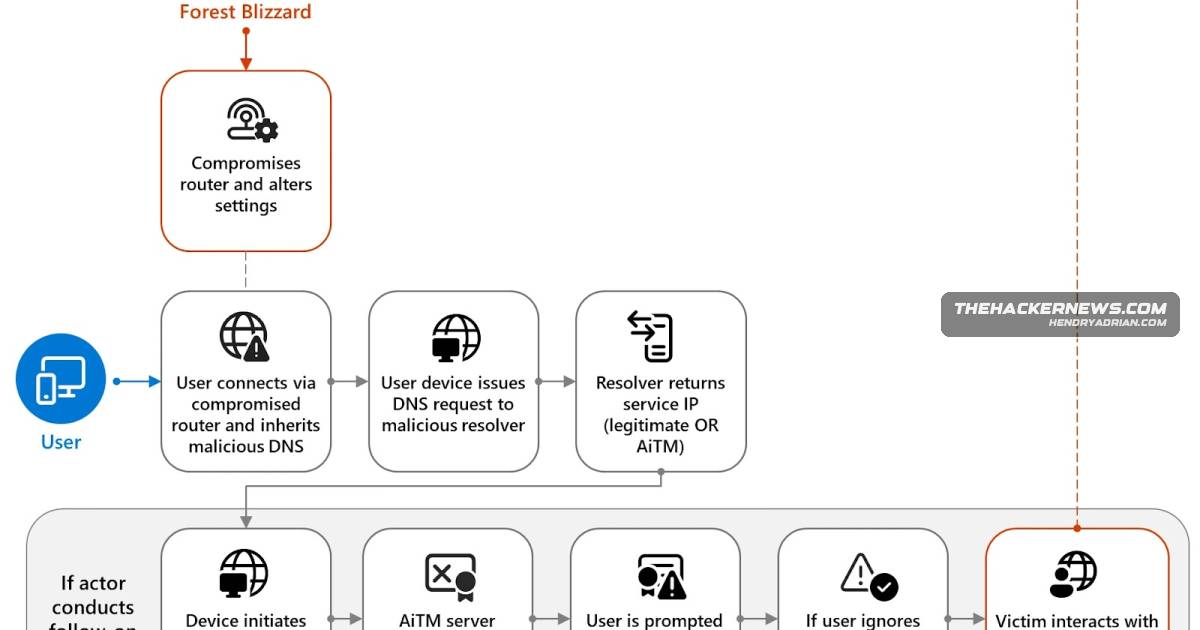
- The actor compromised MikroTik and TP-Link SOHO routers and changed their DNS settings to redirect local network traffic.
- Malicious DNS servers redirected requests to attacker-controlled attacker-in-the-middle nodes, where passwords, OAuth tokens, and other credentials were harvested.
- Microsoft said it identified more than 200 organizations and 5,000 consumer devices impacted; targets included government agencies and third-party email and cloud providers.
- APT28 is said to have likely exploited CVE-2023-50224 on TP-Link WR841N routers, an authentication bypass that could expose stored credentials.
- The infrastructure was disrupted in an operation involving the DOJ, FBI, and international partners. The U.K. NCSC assessed that the actor filtered a broad pool of users for intelligence-value targets.
Article Details
- Event Type
- State-linked cyber espionage campaign involving SOHO router compromise, DNS hijacking, and attacker-in-the-middle (AitM) activity.
- Impact
- Compromised MikroTik and TP-Link routers were reconfigured to redirect DNS traffic through actor-controlled infrastructure, enabling passive collection and theft of passwords, OAuth tokens, and other credentials. Microsoft reported that more than 200 organizations and 5,000 consumer devices were impacted. The campaign infrastructure was disrupted in a joint operation involving the DOJ, FBI, and international partners.
MITRE ATT&CK
CVE
Threat Actors
Vendors
Microsofttargeted government agencies and service providers and has been attributed to APT28/Storm-2754 by Microsoft before its infrastructure was disrupted by a joint DOJ/FBI international action.MikroTikAPT28 (aka Forest Blizzard) conducted a campaign codenamed FrostArmada that compromised insecure MikroTik and TPâLink SOHO routers to change DNS settings and hijack local network traffic for passiveTP-LinkAPT28 (aka Forest Blizzard) has been linked to a new campaign that has compromised insecure MikroTik and TP-Link routers and modified their settings to turn them into malicious infrastructure under their control as
Products
Outlook on the webSome of these domains are associated with Microsoft Outlook on the web.TP-Link WR841NAPT28 is said to have exploited TP-Link WR841N routers for its DNS poisoning operations by likely taking advantage of CVE-2023-50224 (CVSS score: 6.5), an authentication bypass vulnerability that could be used to
Countries
RussiaRussia-linked APT28 (aka Forest Blizzard) conducted a campaign codenamed FrostArmada that compromised insecure MikroTik and TPâLink SOHO routers to change DNS settings and hijack local network traffic for passiveUkraineThis cluster is also assessed to have engaged in interactive operations targeting a small number of MikroTik routers located in Ukraine.
Industries
Cloud service providersagencies, such as ministries of foreign affairs, law enforcement, and third-party email and cloud service providers across North African, Central American, Southeast Asian, and European countries.Governmentin December with communications from over 18,000 IPs across 120 countries, the operation targeted government agencies and service providers and has been attributed to APT28/Storm-2754 by Microsoft before its