
Weekly Security Roundup Details Phorpiex Botnet, ActiveMQ RCE and AI-Related Threats
Summary
A weekly security roundup details Phorpiex’s hybrid P2P botnet, an ActiveMQ RCE chain, phishing and stealer campaigns, and AI-related prompt-injection risks, alongside vulnerabilities and exposed industrial systems.
Key points
- Phorpiex’s Twizt variant combines HTTP command-and-control with TCP/UDP P2P communications and can deliver clippers, spam, and ransomware; the article reports about 125,000 infections daily on average.
- Apache ActiveMQ Classic flaw CVE-2026-34197 can enable remote code execution; when chained with CVE-2024-32114, it can be unauthenticated on versions 6.0.0–6.1.1. The article says fixes are available in versions 5.19.4 and 6.2.3.
- Google says financially motivated group UNC6783 targets organizations through BPO and help-desk social engineering, spoofed Okta logins, clipboard theft, and enrollment of attacker-controlled MFA devices.
- Sansec reported a Magecart campaign affecting 99 Magento stores, using hidden SVG elements to display a fake checkout and steal payment data; PolyShell was identified as the likely entry vector.
- Grafana patched GrafanaGhost, a reported indirect prompt-injection vulnerability that could silently expose sensitive data without user interaction.
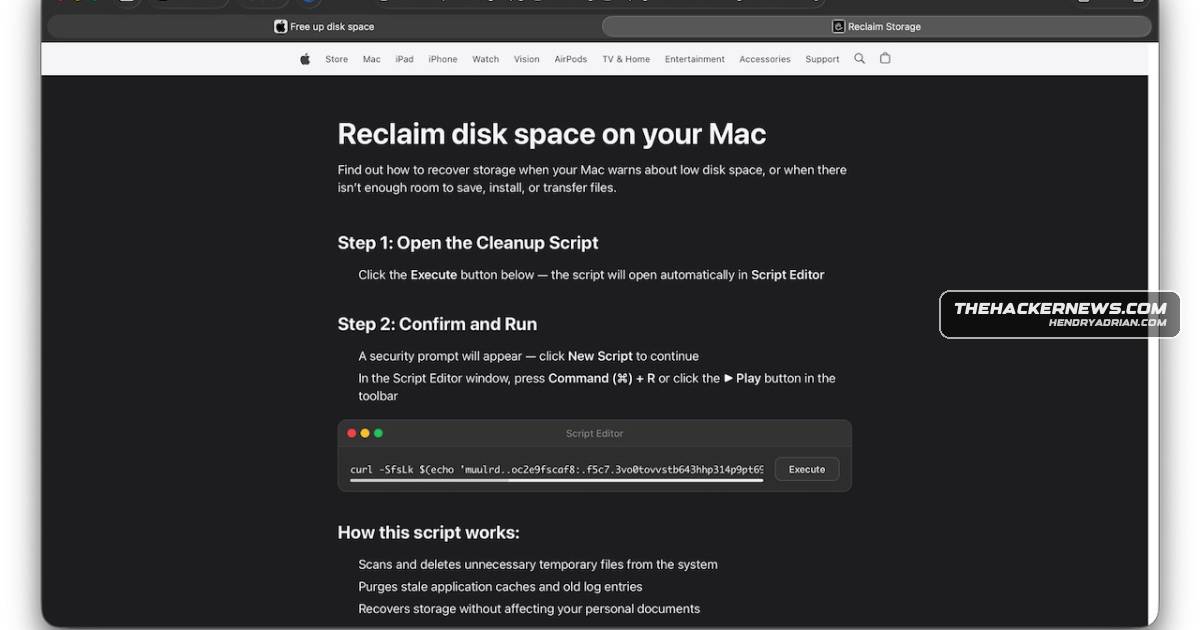
- ClickFix campaigns include Windows MSI installers delivering a Node.js-based stealer and a macOS attack abusing the applescript:// URL scheme to deliver Atomic Stealer.
- Linux kernel flaw CVE-2026-23226 in ksmbd can expose an SMB3 signing key or cause a kernel panic; exploitation requires valid SMB credentials and network access.
Article Details
- Event Type
- Weekly cybersecurity threat roundup covering malware activity, vulnerability exploitation, phishing, infrastructure exposure, and AI-related security risks.
- Impact
- Reported activity includes cryptocurrency theft, credential and payment-data theft, ransomware deployment, enterprise-data exfiltration, phishing, operational disruption, and exposure of private photos. The article also reports vulnerabilities that can enable remote code execution or leak cryptographic keys, and says some exposed infrastructure attacks caused operational disruption and financial loss.
MITRE ATT&CK
T1041 · Exfiltration Over C2 ChannelThe article describes malware exfiltrating data, including prompts and payment information, over attacker communications.T1059.001 · PowerShellA Proxifier-themed campaign uses PowerShell scripts to retrieve further payloads, including a cryptocurrency clipper.T1059.002 · AppleScriptA macOS ClickFix-style attack uses the applescript:// URL scheme to launch Script Editor and deliver an infostealer.T1091 · Replication Through Removable MediaThe Phorpiex variant is reported to propagate through removable and remote drives.T1204.002 · Malicious FileSeveral campaigns rely on victims launching malicious installers or executable files to deliver malware.T1566.002 · Spearphishing LinkReported phishing campaigns use invitation lures, spoofed Okta logins, and links to credential-harvesting pages.
CVE
CVE-2022-41678Apache Software Foundation · Apache ActiveMQAccording to Horizon3.ai, the security defect is a bypass for CVE-2022-41678, a bug that allows authenticated attackers to trigger arbitrary code execution and write web shells to disk.CVE-2024-32114apache · activemq; Apache Software Foundation · Apache ActiveMQA remote code execution (RCE) vulnerability that lurked in Apache ActiveMQ Classic for 13 years could be chained with an older flaw (CVE-2024-32114) to bypass authentication.CVE-2025-40039Linux · LinuxTracked as CVE-2026-23226 (CVSS score: 8.8), it falls under the same bug class as CVE-2025-40039, which was patched in October 2025.CVE-2026-23226Linux · LinuxTracked as CVE-2026-23226 (CVSS score: 8.8), it falls under the same bug class as CVE-2025-40039, which was patched in October 2025.CVE-2026-34197Apache Software Foundation · Apache ActiveMQ; Apache Software Foundation · Apache ActiveMQ All; +2 moreChained ActiveMQ vulnerabilities (including CVE-2026-34197) enable stealthy RCE and can be unauthenticated on some versions.
People
Austin LarsenGoogle Threat Intelligence Group principal threat analyst who described the UNC6783 campaign's targeting and phishing methods.Naveen SunkavallyHorizon3.ai researcher who described the ActiveMQ vulnerability, its credential requirements, and the unauthenticated exposure on some versions.Thijs XhaflaireSecurity researcher who commented on a macOS ClickFix campaign's use of the applescript:// URL scheme to bypass Terminal safeguards.
Threat Actors
Cyber Av3ngersThe article attributes similar attacks on PLCs in late 2023 to Cyber Av3ngers; it does not identify the group as responsible for the current reported exploitation.UNC6783Google is tracking this financially motivated threat cluster, which reportedly targets organizations by compromising BPO providers and help desk staff for data extortion.
Malware
Atomic StealerAccording to Jamf, a ClickFix-style macOS attack is abusing the “applescript://” URL scheme to launch Script Editor and deliver an Atomic Stealer infostealer payload, thereby bypassing Terminal entirely.GhostSocksand took advantage of the topical nature of the leak to distribute Vidar Stealer, PureLogs Stealer, and GhostSocks proxy malware through fake leaked Claude Code GitHub repositories.Globaldistribute high-volume sextortion email spam and facilitate ransomware deployment (e.g., LockBit Black, Global).LockBit Blackas well as distribute high-volume sextortion email spam and facilitate ransomware deployment (e.g., LockBit Black, Global).Lumma StealerA new 64-bit version of Lumma Stealer called Remus (historically called Tenzor) has emerged in the wild following Lumma’s takedown and the doxxing of its alleged core members.PhorpiexThis weekly roundup highlights an array of evolving threats — from a resilient Phorpiex/Twizt hybrid botnet and new stealer families to chained ActiveMQ flaws, platform abuse, and AI-adjacent exploit techniques.PureLogs Stealerwasted no time and took advantage of the topical nature of the leak to distribute Vidar Stealer, PureLogs Stealer, and GhostSocks proxy malware through fake leaked Claude Code GitHub repositories.RemusA new 64-bit version of Lumma Stealer called Remus (historically called Tenzor) has emerged in the wild following Lumma’s takedown and the doxxing of its alleged core members.TenzorA new 64-bit version of Lumma Stealer called Remus (historically called Tenzor) has emerged in the wild following Lumma’s takedown and the doxxing of its alleged core members.TrikA new variant of the botnet known as Phorpiex (aka Trik) has been observed, using a hybrid communication model that combines traditional C2 HTTP polling with a peer-to-peer (P2P) protocol over both TCP and UDP to ensureTwiztThis weekly roundup highlights an array of evolving threats — from a resilient Phorpiex/Twizt hybrid botnet and new stealer families to chained ActiveMQ flaws, platform abuse, and AI-adjacent exploit techniques.ValleyRATZIP file that ultimately leads to the installation of malware that’s consistent with ValleyRAT.Vidarsay, threat actors wasted no time and took advantage of the topical nature of the leak to distribute Vidar Stealer, PureLogs Stealer, and GhostSocks proxy malware through fake leaked Claude Code GitHub repositories.
Vendors
AdobeAdobe has yet to release a security update to address the PolyShell flaw in production versions of Magento.AnthropicThe report urges rapid patching, auditing of trusted platforms and AI integrations, stronger MFA/device controls, and vigilance against supply-chain and insider risksAppleThe attack leverages fake Apple-themed web pages that include instructions to “reclaim disk space on your Mac” by clicking on an “Execute” button that triggers the “applescript://” URL scheme.GrafanaGrafana has patched a security vulnerability that could have enabled attackers to trick its artificial intelligence (AI) capabilities into leaking sensitive data by means of an indirect prompt injection and withoutMetaA former Meta employee in the U.K. is under investigation over allegations that he illegally downloaded about 30,000 private photos from Facebook.Rockwell AutomationData from Censys has revealed that there are 5,219 internet-exposed hosts that self-identify as Rockwell Automation/Allen-Bradley devices.
Products
Apache ActiveMQ ClassicA remote code execution (RCE) vulnerability that lurked in Apache ActiveMQ Classic for 13 years could be chained with an older flaw (CVE-2024-32114) to bypass authentication.Claude Codeactually hijacks a Tunisian university’s private AI endpoint, bundles a stolen and rebranded Anthropic Claude Code system prompt, launders all responses to hide the true upstream source, and exfiltrates every userGitHubWhile the exposure lasted only about three hours, it triggered rapid mirroring of the source code across GitHub, prompting Anthropic to issue takedown notices (and later a partial retraction).GrafanaGrafana has patched a security vulnerability that could have enabled attackers to trick its artificial intelligence (AI) capabilities into leaking sensitive data by means of an indirect prompt injection and withoutJiraBecause these emails are dispatched from the platform’s own infrastructure (e.g., Jira’s Invite Customers feature), they are unlikely to be blocked by email security tools.Linux kernelA high-severity security flaw has been disclosed in the Linux kernel’s ksmbd SMB3 server.LSPosedLSPosed is a powerful framework for rooted Android devices that allows users to modify the behavior of the system and apps in real-time without actually making any modifications to APK files.macOSmacOS attack bypasses Terminal safeguardsMagentoA large-scale Magecart campaign is using invisible 1Ã1 pixel SVG elements to inject a fake checkout overlay on 99 Magento e-commerce stores, exfiltrating payment data to six attacker-controlled domains.Microsoft WindowsA ClickFix campaign targeting Windows users is leveraging malicious MSI installers to deliver a Node.js-based information stealer.Okta“The campaign relies on live chat social engineering to direct employees to spoofed Okta logins using [org].zendesk-support[##].com domains,” Austin Larsen, Google Threat Intelligence Group (GITG) principal threat
Countries
China“The Phorpiex botnet remains a highly adaptive and resilient threat.” There are about 125,000 infections daily on average, with the most affected countries being Iran, Uzbekistan, China, Kazakhstan, and Pakistan.IndiaSince the start of 2025, more than 2,000 Kaspersky users – most of them in India and Vietnam – have encountered the threat.Iran“The Phorpiex botnet remains a highly adaptive and resilient threat.” There are about 125,000 infections daily on average, with the most affected countries being Iran, Uzbekistan, China, Kazakhstan, and Pakistan.Kazakhstan“The Phorpiex botnet remains a highly adaptive and resilient threat.” There are about 125,000 infections daily on average, with the most affected countries being Iran, Uzbekistan, China, Kazakhstan, and Pakistan.Pakistan“The Phorpiex botnet remains a highly adaptive and resilient threat.” There are about 125,000 infections daily on average, with the most affected countries being Iran, Uzbekistan, China, Kazakhstan, and Pakistan.United States“Cyber-enabled fraud is responsible for almost 85% of all losses reported to IC3 [Internet Crime Complaint Center] in 2025,” the U.S.Uzbekistan“The Phorpiex botnet remains a highly adaptive and resilient threat.” There are about 125,000 infections daily on average, with the most affected countries being Iran, Uzbekistan, China, Kazakhstan, and Pakistan.VietnamSince the start of 2025, more than 2,000 Kaspersky users – most of them in India and Vietnam – have encountered the threat.
Industries
business process outsourcingand is targeting dozens of high-profile organizations across multiple sectors by compromising business process outsourcing (BPO) providers and help desk staff for later data extortion.Critical infrastructurecritical infrastructure sectors, causing operational disruption and financial loss in some cases.E-commerceA large-scale Magecart campaign is using invisible 1Ã1 pixel SVG elements to inject a fake checkout overlay on 99 Magento e-commerce stores, exfiltrating payment data to six attacker-controlled domains.GovernmentAkira, Qilin, INC./Lynx/Sinobi, BianLian, Play, Ransomhub, Lockbit, Dragonforce, Safepay, and Medusa emerged as the top ten variants to hit critical manufacturing, healthcare, public health, and government entities.HealthcareAkira, Qilin, INC./Lynx/Sinobi, BianLian, Play, Ransomhub, Lockbit, Dragonforce, Safepay, and Medusa emerged as the top ten variants to hit critical manufacturing, healthcare, public health, and government entities.ManufacturingAkira, Qilin, INC./Lynx/Sinobi, BianLian, Play, Ransomhub, Lockbit, Dragonforce, Safepay, and Medusa emerged as the top ten variants to hit critical manufacturing, healthcare, public health, and government entities.public healthAkira, Qilin, INC./Lynx/Sinobi, BianLian, Play, Ransomhub, Lockbit, Dragonforce, Safepay, and Medusa emerged as the top ten variants to hit critical manufacturing, healthcare, public health, and government entities.