
Attackers Abuse n8n Webhooks for Phishing, Malware Delivery and Device Fingerprinting
Summary
Cisco Talos says attackers have abused n8n cloud webhooks since October 2025 to host phishing pages, deliver modified Datto and ITarian RMM installers, and fingerprint email recipients. Webhook-linked email volume rose 686% in March 2026 versus January 2025.
Key points
- Cisco Talos reports that attackers have abused n8n cloud-hosted webhooks in phishing campaigns since October 2025.
- Webhook responses use HTML and JavaScript to make malicious downloads appear to come from n8n-hosted pages.
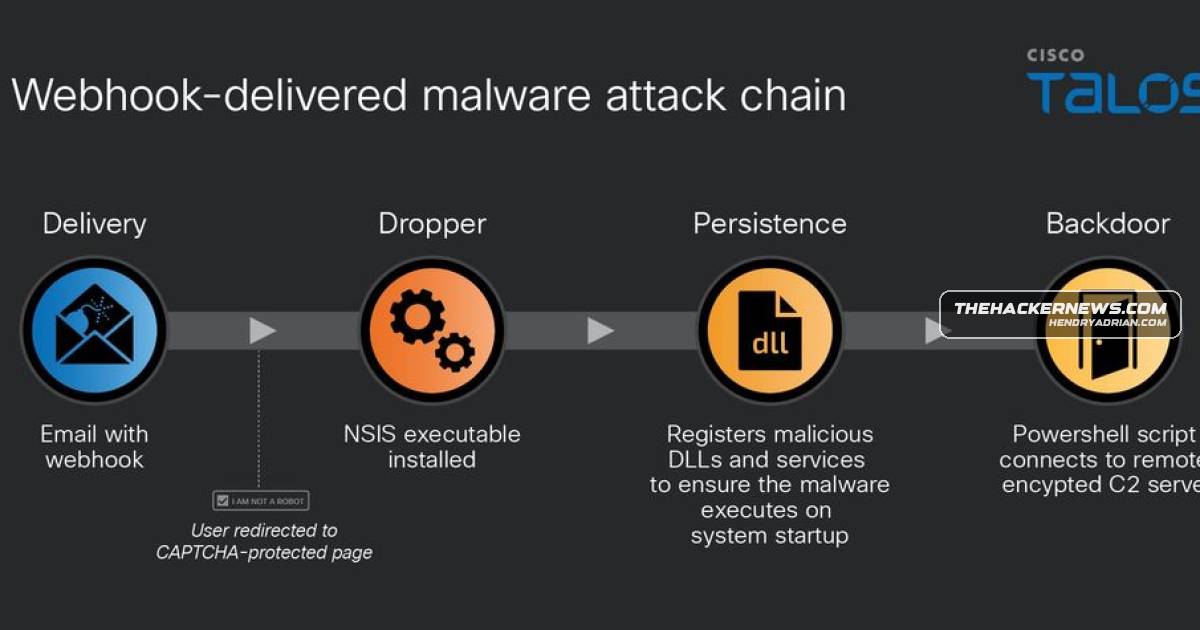
- A shared-document lure leads recipients to a CAPTCHA page that triggers a malicious payload download from an external host.
- The payloads include executables or MSI installers for modified Datto and ITarian RMM tools, used to establish persistence and connect to command-and-control servers.
- Other emails use invisible images hosted on webhook URLs to capture recipient information when the message is opened.
- Talos says email volume containing these webhook URLs was about 686% higher in March 2026 than in January 2025, and recommends hardening low-code platforms and monitoring webhook use.
Article Details
- Event Type
- Phishing campaigns abusing n8n cloud-hosted workflows and exposed webhooks for malware delivery and recipient fingerprinting.
- Impact
- Cisco Talos reported that attackers used n8n-hosted webhook pages and CAPTCHA prompts to deliver payloads that install modified Datto or ITarian Endpoint Management tools for persistent remote access and command-and-control connections. In a separate approach, invisible images on webhook URLs enabled attackers to identify recipients when emails were opened. Talos said email volume containing these URLs in March 2026 was about 686% higher than in January 2025.
MITRE ATT&CK
T1204.001 · Malicious LinkThe campaign relied on recipients clicking an embedded link to reach the CAPTCHA page and activate the payload download.T1219 · Remote Access ToolsThe delivered payloads used modified remote monitoring and management tools to establish persistent remote access and command-and-control connections.T1566.002 · Spearphishing LinkPhishing emails contained links to n8n-hosted webhook pages that led to malicious payload delivery.
People
Products
Dattothese campaigns use n8n-hosted pages and CAPTCHA triggers to fetch modified RMM installers (including Datto and ITarian) for persistent remote access, with webhook-related phishing volume spiking sharply.ITarian Endpoint Managementmodified versions of legitimate Remote Monitoring and Management (RMM) tools like Datto and ITarian Endpoint Management, and use them to establish persistence by establishing a connection to a command-and-controln8nThreat actors are abusing n8n’s managed cloud-hosted workflows and exposed webhook URLs on the *.app.n8n.cloud domain to run phishing campaigns that deliver malicious payloads and fingerprint devices.