
Sinobi Claims Scales and Associates Inc as a Victim
A ransomware.live monitoring record attributes a leak-site claim involving Scales and Associates Inc to Sinobi. The claim is unconfirmed.
Monitors ransomware victims, threat groups, leak-site activity, and newly disclosed ransomware incidents.
2834 articles
A ransomware.live monitoring record attributes a leak-site claim involving Scales and Associates Inc to Sinobi. The claim is unconfirmed.
Ransomware.live reports that MedusaLocker listed Brazilian supermarket chain Bandeirante Supermercados in a ransomware claim on May 5, 2026. The post says the claim is unconfirmed.
A ransomware.live record attributes an unverified claim to MedusaLocker that it extracted approximately 16,000 email addresses from Elken Sdn Bhd.

Ransomware.live lists Punch & Associates Investment Management as an Akira claim; the group reportedly threatens to upload 10 GB, including sensitive client and employee information. The claims are unverified.
Akira claims it breached Maximum Mold and threatens to leak employee information, customer files, contracts, NDAs, and project documents. The claims are unconfirmed; ransomware.live says it monitors the post.
A ransomware claim attributed to Qilin names Spanish consumer-services organization Ahorramas. The post links to the group’s claim but says the information is unconfirmed and provides no further incident details.
ShinyHunters claim responsibility for a breach involving Instructure’s Canvas LMS and threaten to leak a list of affected schools unless a settlement is reached by May 7, 2026. The post says the claim is unconfirmed.
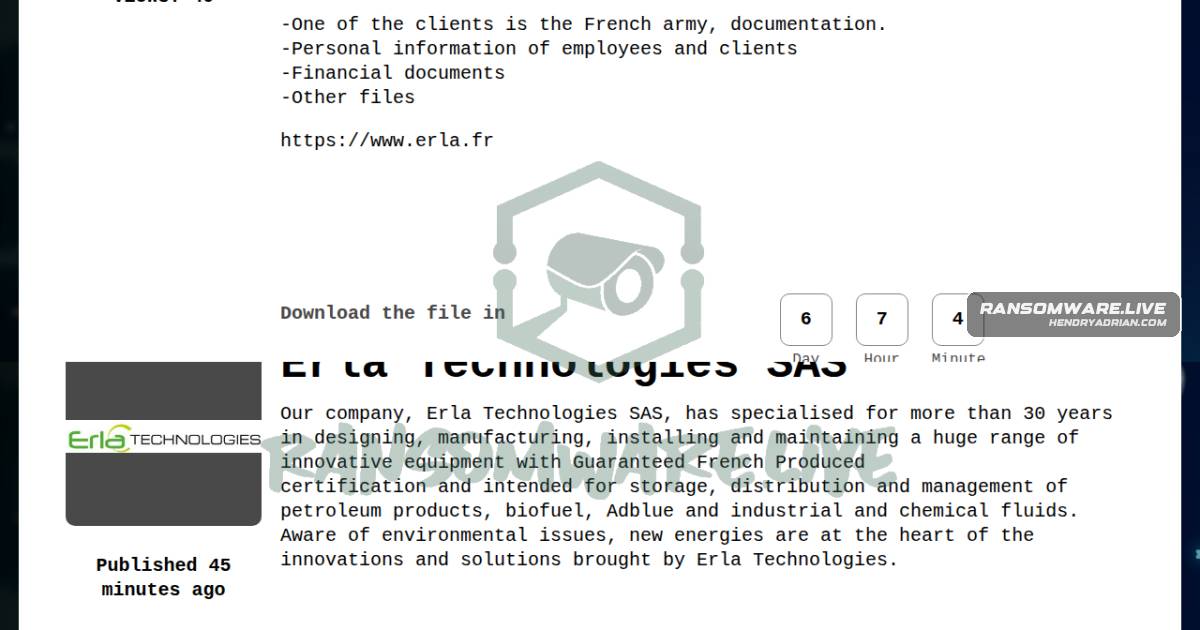
The spacebears ransomware group claims Erla Technologies SAS was affected and that employee and client personal information, financial documents, and other files were exposed. The claim is unverified.
ShinyHunters claim they targeted Colombia’s Adelante Soluciones Financieras (Addi.com), alleging over 16 million records and 518GB+ of compressed data. The claim is unverified; ransomware[.]live says it cannot confirm the information.
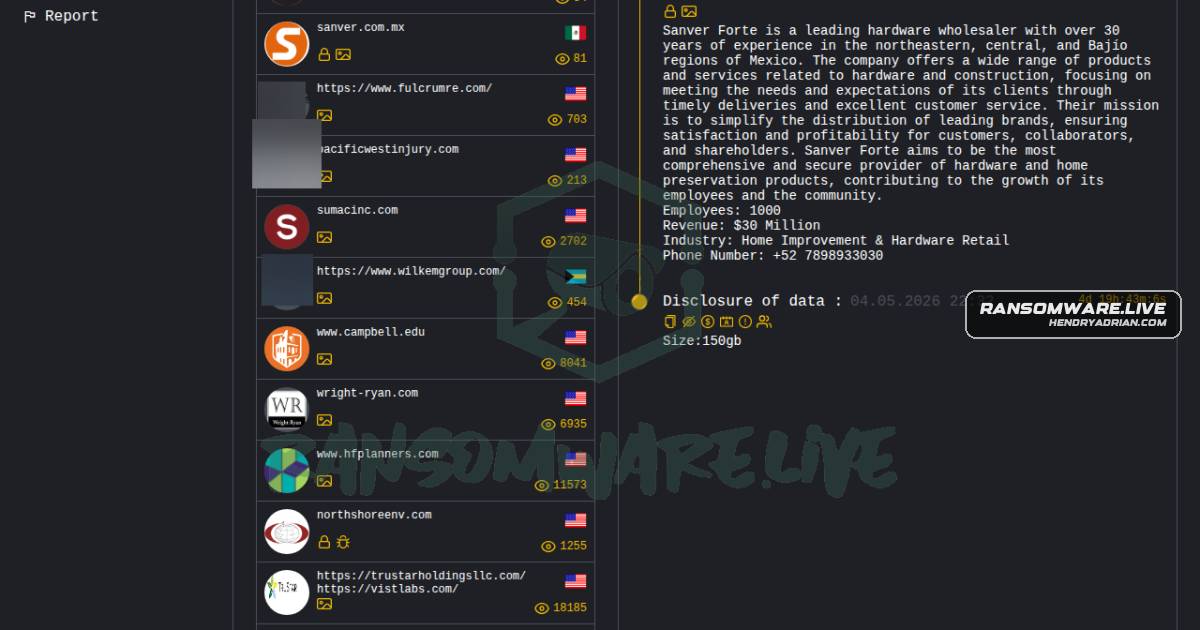
A monitoring post says incransom claims to have compromised Mexican hardware wholesaler Sanver Forte and threatens data release. The claim is unconfirmed.
Ransomware actor krybit claims Foodsmart Dominicana, S.R.L., in the Dominican Republic, as a victim. The claim concerns foodsmart[.]com[.]do and is unconfirmed; ransomware.live says it is monitoring the claim.
Ransomware.live lists hokuyo2006[.]co[.]jp, a Japanese manufacturing company, in a Safepay ransomware claim. The record cites the group's leak-site post; the claim is unconfirmed.
A ransomware.live-monitored post attributes a claim involving Thompson Builders Corporation and 3,633 GB of data to securotrop. The claim is awaiting clarification and the publisher says it cannot confirm its accuracy.
Pear claims it compromised Morning Star Tours and is demanding a ransom to prevent the release of information. The claim is unverified and is attributed to Pear and ransomware.live monitoring.
The ransomware group qilin claims it compromised Seagate Capital Construction in the US, deployed ransomware, and threatened data exfiltration. The monitoring post says the claims are unconfirmed.
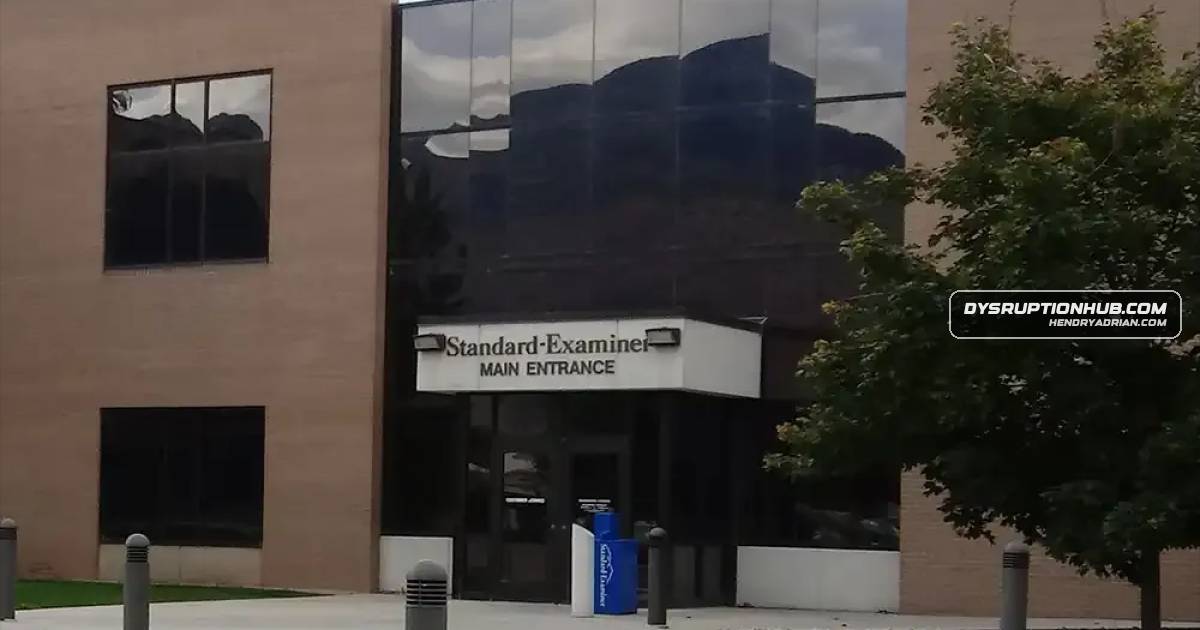
The Standard-Examiner reported April print delays, then Qilin listed the newspaper on its leak site in May. The paper has not confirmed ransomware, data theft or a connection between the claim and the disruption.
A ransomware.live monitoring post attributes to PrinzEugen an unconfirmed claim that a campaign targeting Standard Bank Group and Liberty began February 27, 2026, and exfiltrated 1.2 TB of data.
A ransomware claim attributed to m3rx names German technology company it-freitag[.]de. The post is unverified and reports no stolen data.
A ransomware.live-monitored claim attributes the alleged theft of 180 GB of data, reportedly 698,000 files, from Engineered Machine Tool (emtco[.]com) to m3rx. The article says the claim is unconfirmed.
A ransomware.live monitoring record attributes to Stormous an unverified claim involving FANASA[.]COM and lists financial, tax, customer, vendor, and internal corporate records as allegedly exposed.
A monitored record attributes an unverified ransomware claim about or-technology[.]com to Stormous. It lists financial, planning, project-report, and SQL-related information; the accuracy is unconfirmed.
A ransomware claim attributed to Qilin names Armstrong George Cohen Will Ophthalmology in the US. The post suggests data exposure and service disruption, but the information is unconfirmed.
A ransomware.live monitoring record attributes an unconfirmed breach claim against Photonic to actor mnt6; the article says it cannot independently confirm the claim.
A ransomware claim attributed to cmdorganization names JG Stewart Construction of Canada and alleges unauthorized access and operational disruption. The post says the claim is unconfirmed.