
MedusaLocker Claims It Extracted About 16,000 Email Addresses from Elken Sdn Bhd
Summary
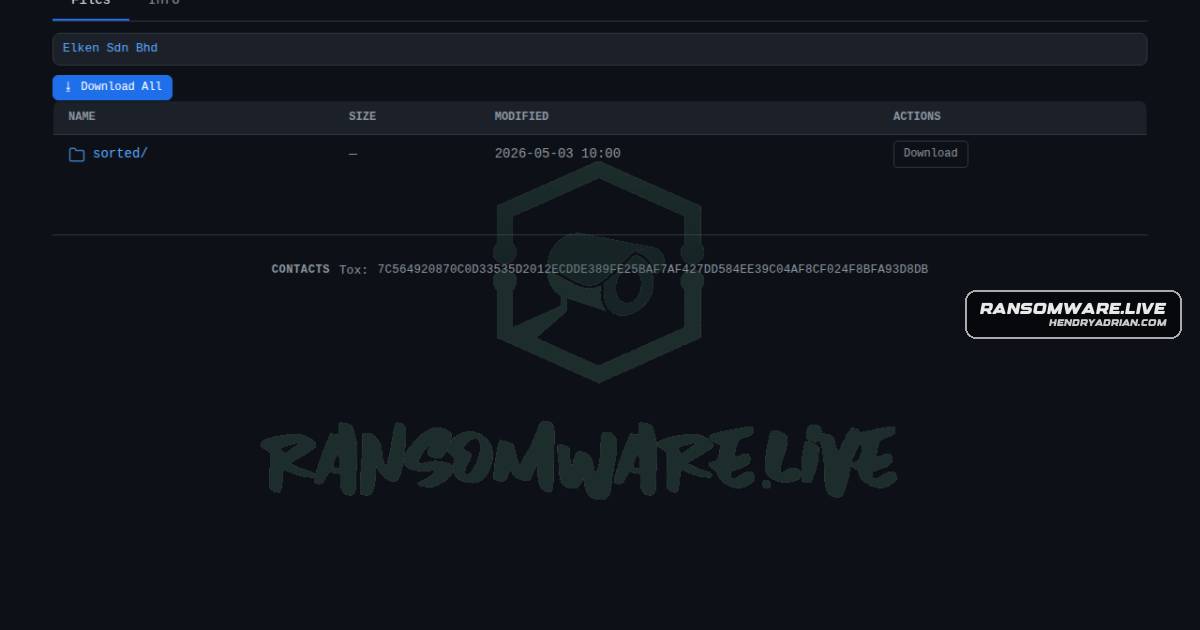
A ransomware.live record attributes an unverified claim to MedusaLocker that it extracted approximately 16,000 email addresses from Elken Sdn Bhd.
Key points
- The named victim is Elken Sdn Bhd.
- The claim is attributed to the MedusaLocker ransomware actor and linked to its leak-site listing.
- The group claims approximately 16,000 email addresses were extracted; the report says it cannot confirm the claim.
Article Details
- Victim
- Elken Sdn Bhd
- Claim Date
- 2026-05-05
- Encryption Status
- Unknown
- Exfiltration Status
- Claimed by the ransomware group; unverified
- Exfiltrated Data
- Email addresses
- Exfiltrated Size
- Approximately 16,000 email addresses
- Ransom Demand
- Unknown
- Leak Status
- Listed on the ransomware group's site; publication or authenticity of the data is unverified