
Incransom Claims Sanver Forte as a Victim in Mexico
Summary
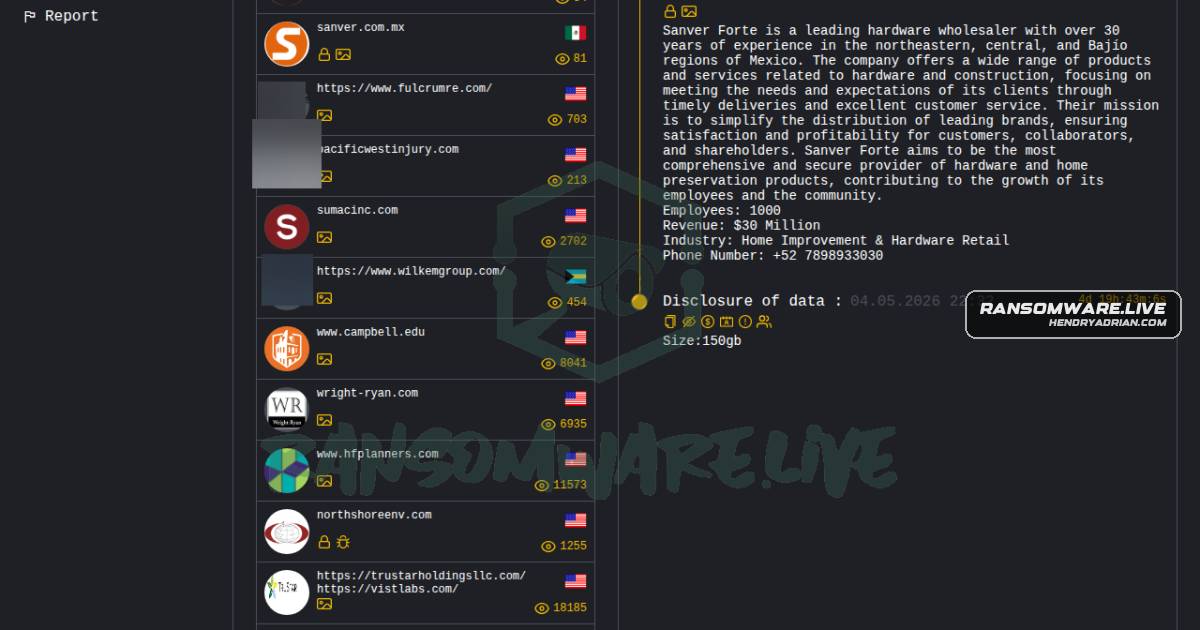
A monitoring post says incransom claims to have compromised Mexican hardware wholesaler Sanver Forte and threatens data release. The claim is unconfirmed.
Key points
- The record names Sanver Forte as the victim and incransom as the actor.
- The post attributes the claim to the actor's disclosure page and says ransomware.live monitored it.
- The group reportedly threatens to release data and disrupt customers and operations unless paid.
- The claim potentially involves sensitive financial and operational data; the post provides no independent confirmation.
Article Details
- Victim
- Sanver Forte
- Victim Domain
- sanver.com.mx
- Claim Date
- 2026-05-04
- Encryption Status
- Unknown; encryption is not reported.
- Exfiltration Status
- Unconfirmed; the report says sensitive data may have been exfiltrated.
- Exfiltrated Data
- Potentially sensitive financial and operational data, according to the report.
- Ransom Demand
- Payment is reportedly demanded, but no amount is disclosed.
- Leak Status
- Release was reportedly threatened; no publication of data is reported.