
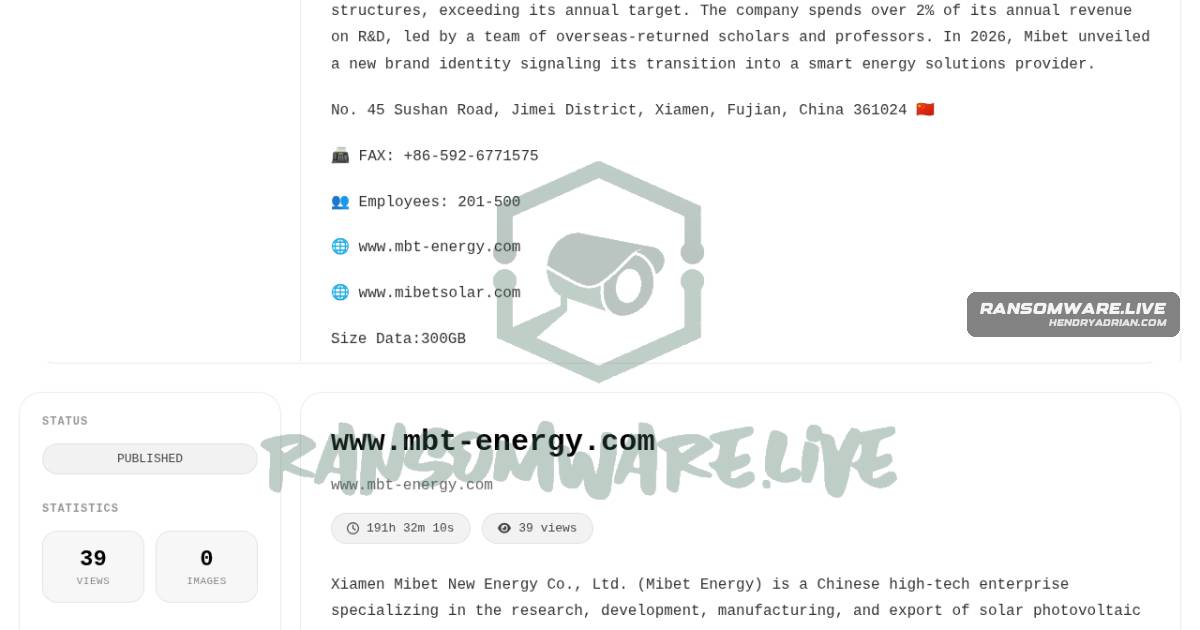
Krybit Claim Names Mibet Energy’s German Website
A ransomware.live record says krybit claims www[.]mbt-energy[.]com, associated with Mibet Energy in Germany, as a victim. It describes operational disruption, but the claim is unconfirmed.
Monitors ransomware victims, threat groups, leak-site activity, and newly disclosed ransomware incidents.
2821 articles
A ransomware.live record says krybit claims www[.]mbt-energy[.]com, associated with Mibet Energy in Germany, as a victim. It describes operational disruption, but the claim is unconfirmed.

Lapsus$ claims it has data from GitHub Internal and says it may leak the data for free if no buyer is found. The claim, monitored by ransomware[.]live, is unverified.
Lapsus$ claims it obtained mappings of INGKA GROUP’s global e-commerce architecture and internal platforms, including supply chain, cloud, and MLOps systems. The claim is unconfirmed and was monitored by ransomware.live.
Triple X claims it stole about 1.5TB from a U.S. law firm, including 24,900 passport files and sensitive financial, tax and identity records. The monitoring post says the group’s claims are unconfirmed.
Triple X claims it exfiltrated about 2 TB of customer records, contracts, passports and ID cards from Bni[.]co[.]id and says more data will be released. The claim is unconfirmed; ransomware[.]live attributes the listing to the group.
Ransomware.live attributes an unverified claim to Black X that it holds core technical data from South Korea’s Daechang Solution and plans to sell it to one buyer. No independent confirmation is provided.
Ransomware.live lists the Australian Medical Council as a target claimed by threeam and alleges disruption to accreditation and assessment activities. The post says the claim is unconfirmed.
The threeam ransomware group reportedly listed Belgian IT provider ConsulTIC (consultic[.]be) as a victim on June 12, 2026. The monitoring post says the claim is unconfirmed; no incident impact is independently established.

Ransomware.live lists WS Group Brasil (ws[.]com[.]br) as a threeam claim dated June 12, 2026; the post alleges service disruption, which it says is unconfirmed.
Ransomware.live reports that threeam claimed an attack on Argentina’s Molinos Cabodi Hnos. S.A., alleging disruption to production and services; the post says the claim is unconfirmed.
Ransomware.live attributes an unverified claim to threeam alleging disruption at Germany-based BSynchro Holding, whose insurtech products include CORA. The record lists bsynchro[.]com; no independent confirmation is provided.

A ransomware.live record attributes a ransomware claim against Malaysia’s MyIPO to payload, citing the actor’s leak-site post. The claim is unconfirmed.
A ransomware.live record attributes an unverified claim targeting insamani[.]com[.]ar and INSA INDELMA S.A. to ThreeAM. The record gives June 12, 2026 dates, while its introduction says March 2024.
Ransomware.live lists Palmero, an Argentine capital goods manufacturer, as a threeam target, citing the group’s claim dated June 12, 2026. The site says it could not confirm the claim.
ransomware.live lists the Town of Jastrebarsko (jastrebarsko[.]hr) as a ThreeAM ransomware claim published June 12, 2026. The article says the claim is unconfirmed.

Ransomware.live lists Jet Machined Products as a victim claimed by the threeam group. The claim is unverified; the article provides no confirmed incident details.
Stormous claimed it breached mlit[.]com[.]my and stole operational and financial records. The claim is unverified; the post says it is based on public claims monitored by ransomware[.]live.
ShadowByt3$ claims it stole 859MB of Nintendo[.]com data, including employee and payment-related records, and demands $2 million to prevent publication by June 15, 2026. The claim is unconfirmed.
Ransomware.live lists Cambridge Mobile Telematics as a coinbasecartel ransomware target and claims the incident disrupted its driving-analytics and DriveWell platform. The post says the claims are unconfirmed.
Ransomware.live reports that actor coinbasecartel claimed Demand.io as a victim, demanded payment, and threatened disruption to data or operations. The claim is unconfirmed.

A ransomware claim monitored by ransomware.live attributes an alleged compromise of Al Ishrak Contracting to dragonforce. The article says the claim is unconfirmed.

Ransomware.live lists Cheoy Lee Shipyards as a DragonForce target, with the claim dated June 12, 2026. The post alleges operational disruption and threats to data and systems; these claims are unconfirmed.
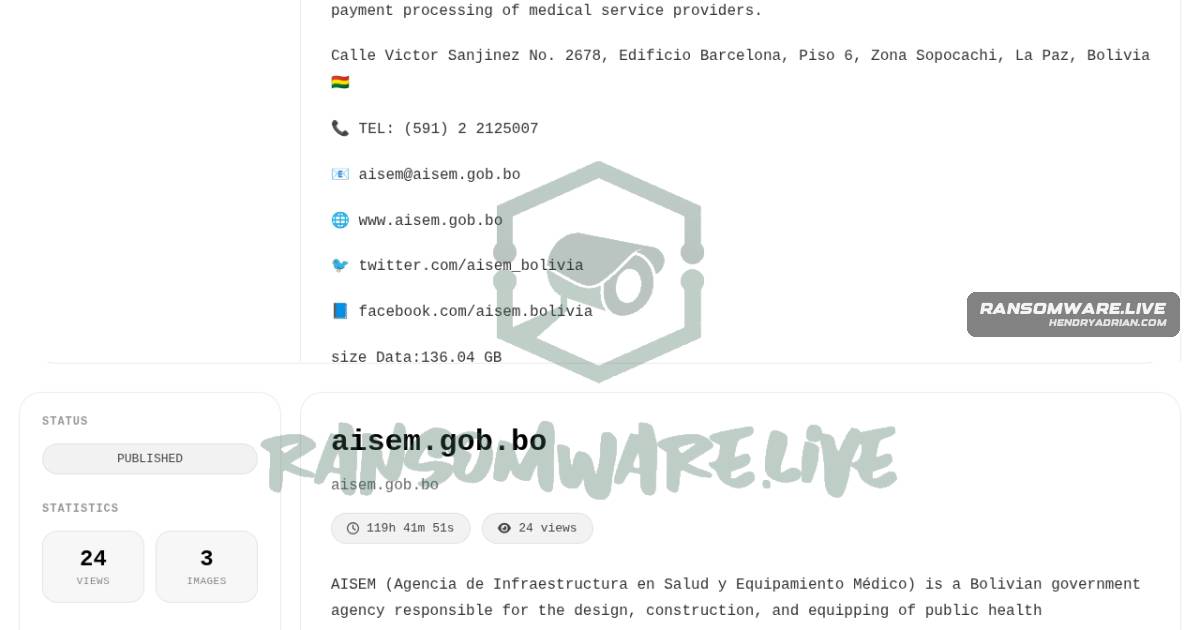
A ransomware[.]live monitoring post reports Krybit’s ransomware claim against Bolivia’s AISEM, the agency responsible for health infrastructure and medical equipment. The post alleges service and system disruption; the claim is unconfirmed.
ShinyHunters claim they will leak data allegedly taken from Zayo and Allstream unless contacted by June 16, 2026. The claim is monitored by ransomware.live and is unconfirmed.