
Krybit Claims Ransomware Activity Against Bolivia’s AISEM
Summary
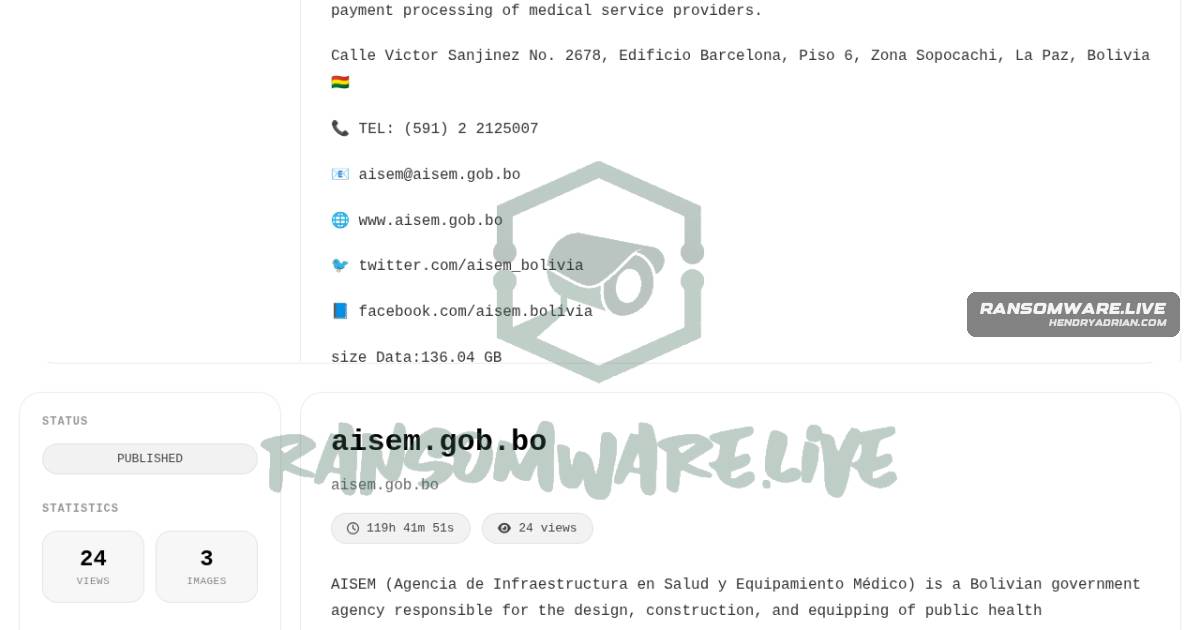
A ransomware[.]live monitoring post reports Krybit’s ransomware claim against Bolivia’s AISEM, the agency responsible for health infrastructure and medical equipment. The post alleges service and system disruption; the claim is unconfirmed.
Key points
- The monitoring record identifies AISEM, a Bolivian government agency, as the claimed victim.
- Krybit is named as the actor; the post attributes the claim to the group’s source.
- The post alleges disruption to AISEM’s services and systems, but provides no independent confirmation.
- The claim was discovered and published on June 12, 2026.
Article Details
- Victim
- AISEM
- Victim Domain
- aisem.gob.bo
- Claim Date
- 2026-06-12
- Encryption Status
- Not disclosed
- Exfiltration Status
- Not disclosed
- Ransom Demand
- Not disclosed
- Leak Status
- A ransomware-group claim was posted; publication or leakage of data was not reported.