
Nova Claims Kedah State Government Portal Compromise
Ransomware.live reports that nova claims to have compromised the Kedah State Government's public-services portal and offers a data tree and samples as evidence. The claim is unconfirmed.
Monitors ransomware victims, threat groups, leak-site activity, and newly disclosed ransomware incidents.
2821 articles
Ransomware.live reports that nova claims to have compromised the Kedah State Government's public-services portal and offers a data tree and samples as evidence. The claim is unconfirmed.
Qilin claims it encrypted data affecting Q Link Wireless operations in the United States. The claim is unconfirmed; the post cites the group’s leak site and says it is monitored by ransomware.live.
Ransomware.live lists Misericórdia de Santo Tirso, a Portuguese healthcare organization, as a Qilin ransomware target. The post attributes claims of unauthorized access and file encryption to Qilin and says the information is unconfirmed.
Ransomware.live lists an unconfirmed SafePay claim targeting tokyocivil[.]co[.]jp in Japan, with a June 15, 2026 publication date.
SafePay’s leak site lists hughstirling[.]co[.]uk as a ransomware victim; ransomware.live monitored the claim. The report identifies the firm as based in Goslar, Germany, and says the claim is unconfirmed.
Incransom claimed Smith and Associates, a Maine accounting firm, as a victim. The ransomware.live-monitored record was discovered June 15, 2026; the claim is unconfirmed.

Ransomware.live reports an unverified ShinyHunters claim that Glendale Community College data was stolen: 62+ GB across 304,000+ files, including 150,000+ student records. The group demanded contact by June 18, 2026.
ShinyHunters claims to have taken more than 23GB of data from moody[.]edu, including communications, enrollment, donor, payroll and student-housing records, and set a June 18, 2026 deadline. The claim is unconfirmed.
Ransomware[.]live reports an unverified ShinyHunters claim that Illinois Central College data was compromised, including payroll, banking and student records. The group allegedly demanded contact by June 18, 2026, or threatened leakage and disruption.
Ransomware.live lists Can Healthcare Group in Turkey as a Qilin ransomware target. The post says operations were impacted after unauthorized access, but notes the information is based on the group’s unconfirmed claim.
A ransomware.live monitoring record attributes a ransomware claim against Mexico’s Grupo Indi to Qilin. The group’s claim is unverified; the record reports system disruption but provides no independent confirmation.
A ransomware.live monitoring post attributes a claim targeting Mahajak Development in Thailand to thegentlemen. The group’s claims of disruption are unverified; the post says it cannot confirm them.
A ransomware claim attributed to thegentlemen names South Texas Spinal Clinic and alleges operational impact. The claim is unconfirmed; the post says it is monitored by ransomware[.]live.
A ransomware.live-monitored post attributes a ransomware claim involving Colombian distributor Enciso Ltda to thegentlemen. The reported operational disruption is unconfirmed; the article says it cannot verify the group’s claims.
Nova claims Sky Devices’ technology systems were compromised and says it will provide a data tree and samples if contacted. The monitoring post says the claim is unconfirmed.
Ransomware.live records an unverified nova claim involving Bangladesh-based Divine IT. The actor allegedly shared samples of stolen data with the company’s support team to prompt engagement.
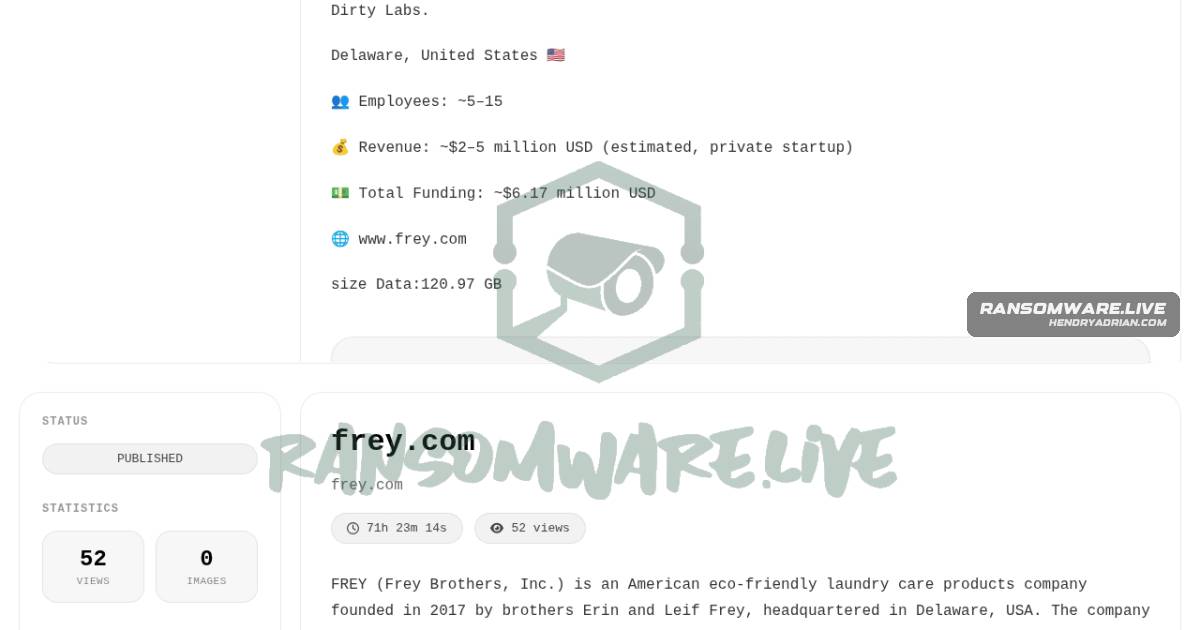
A ransomware.live post attributes a ransomware claim involving FREY (Frey Brothers, Inc.) to krybit. It reports encrypted files and affected system availability, but says the claims are unconfirmed.

DragonForce allegedly claimed it deployed ransomware against London production studio INK and indicated operational disruption in the UK. The claim is unconfirmed; the article's June 2024 reference conflicts with June 2026 monitoring timestamps.
A ransomware.live post attributes to nightspire an unconfirmed claim that Blue Nile Medical Center’s systems were compromised and encrypted and more than 3,000 patient EHR records exposed.
Nova allegedly claims to have stolen data from Balai Besar POM di Bandung, an Indonesian food and drug regulator. The monitoring post says the actor offered a data tree and samples; the claim is unconfirmed.
Nightspire is alleged to have targeted WaxWorks Inc., with claims of encrypted files, operational disruption and a payment demand. The post says the claims are unconfirmed and is monitored by ransomware.live.
A ransomware.live monitoring post attributes claims of unauthorized access and data encryption at Silsbee Police Department to Nightspire. The claims are unconfirmed; no official statement is provided.
A ransomware.live monitoring post attributes to ShinyHunters a claim of stealing over 297 GB of Council of Europe data and threatens publication unless the organization makes contact by June 16, 2026. The claims are unconfirmed.
Ransomware.live lists Charisma Media as an alleged Securotrop ransomware target, with a claimed impact size of 808 GB. The listing is marked “Awaiting,” and the post says the claim is unconfirmed.