
Krybit Claims Ransomware Attack on Malaysian MAJUHOME
Summary
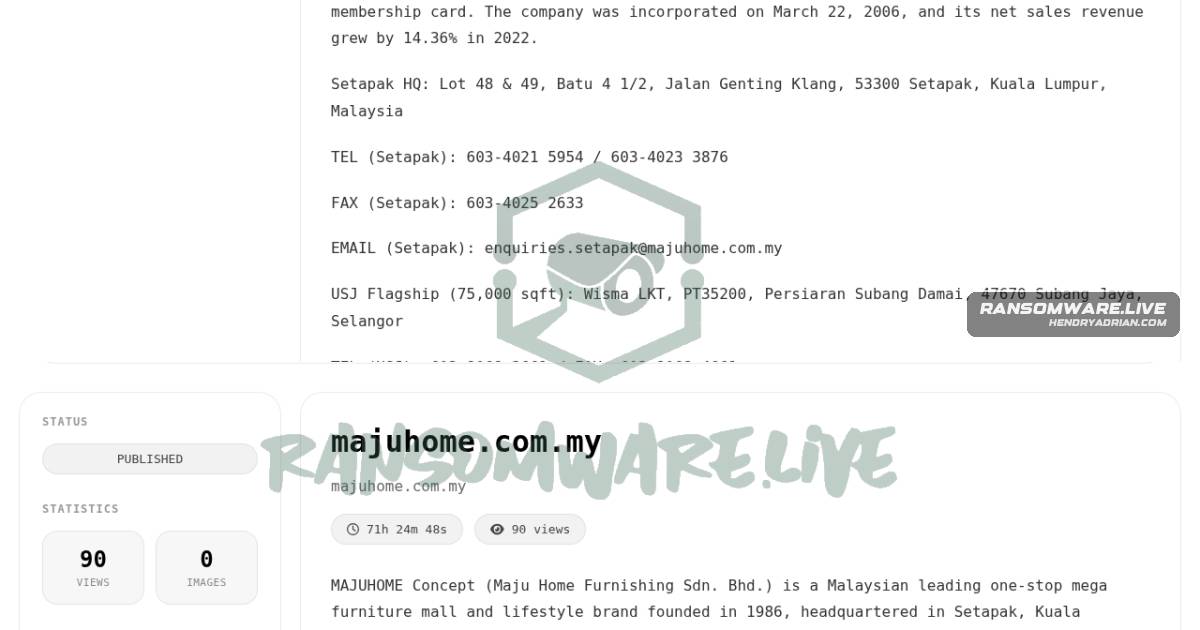
Ransomware.live recorded an unverified krybit claim targeting MAJUHOME Concept in Malaysia. The post says operations were disrupted and data exposure was a risk, but provides no independent confirmation.
Key points
- The record names MAJUHOME Concept (Maju Home Furnishing Sdn. Bhd.) as the victim and krybit as the ransomware actor.
- The claim is attributed to krybit’s onion blog and monitored by ransomware.live.
- The post describes operational disruption and data exposure risk, but explicitly says the group’s claims could not be confirmed.
- No independent evidence of compromise, data exposure, or disruption is provided.
Article Details
- Victim
- MAJUHOME Concept (Maju Home Furnishing Sdn. Bhd.)
- Victim Domain
- majuhome.com.my
- Claim Date
- 2026-07-03
- Encryption Status
- Unknown; the source does not report whether systems were encrypted.
- Exfiltration Status
- Unknown; the source reports data exposure risks but does not confirm exfiltration.
- Ransom Demand
- Not disclosed
- Leak Status
- Unknown; the source reports a public ransomware-group claim but does not state whether data were published.