
Qilin Claims Db Tarimsal Enerji as a Ransomware Victim
ransomware.live lists Db Tarimsal Enerji as a Qilin ransomware victim in Turkey, citing a public group claim. The claim is unconfirmed.
Monitors ransomware victims, threat groups, leak-site activity, and newly disclosed ransomware incidents.
2804 articles
ransomware.live lists Db Tarimsal Enerji as a Qilin ransomware victim in Turkey, citing a public group claim. The claim is unconfirmed.

A ransomware.live monitoring post lists Collge Mont Notre-Dame de Sherbrooke as a cmdorganization claim dated July 30, 2026. It says the school’s network and services were disrupted but notes the claims are unconfirmed.
A ransomware.live monitoring post attributes a ransomware claim against U.S.-based TenSparrows to Qilin. The post alleges disruption and encrypted data, but says the claims are unconfirmed.
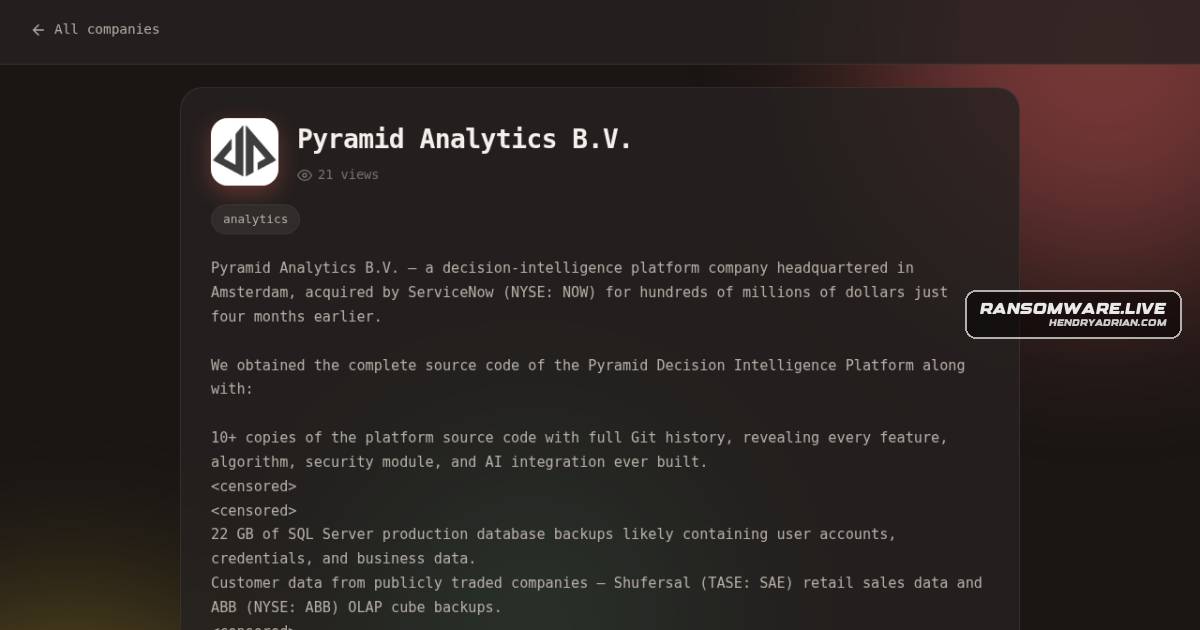
Ransomware.live reports an unverified Aurora claim that Pyramid Analytics B.V. data includes the platform’s source code, full Git histories, and 22 GB of production SQL Server backups, allegedly containing credentials and customer information.
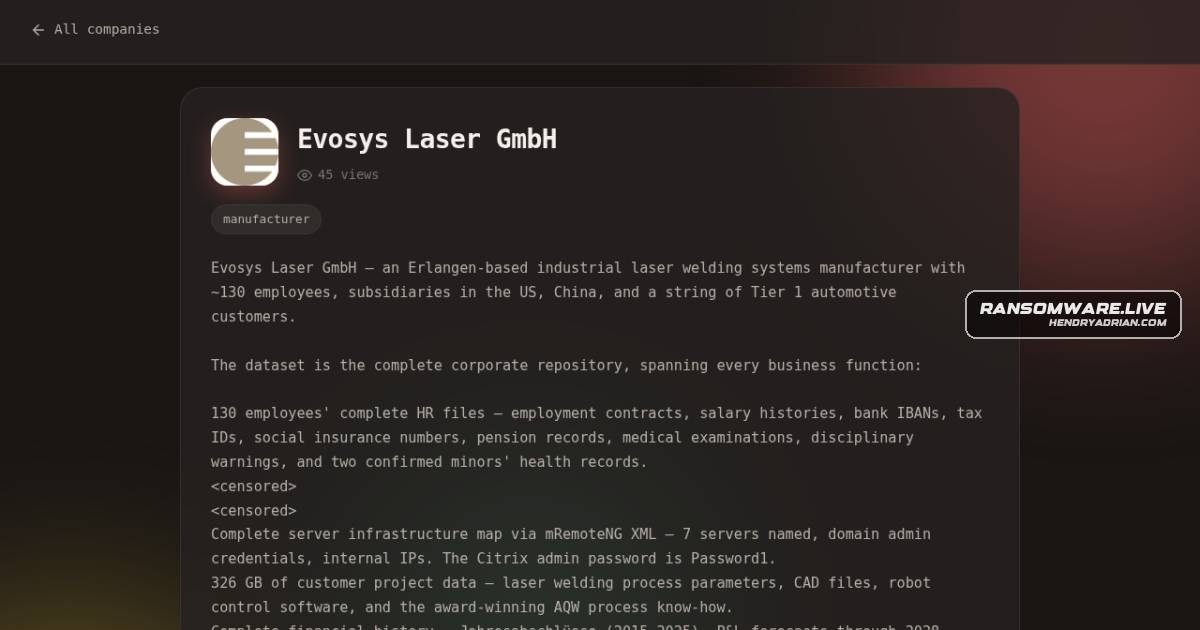
Aurora claims it compromised Evosys Laser GmbH and exposed corporate data, including HR records, infrastructure credentials, customer projects and industrial-control files. The claim is unverified; ransomware[.]live cites the group’s public post.
Aurora claims it stole employee files, rental contracts and customer claims data from Van Eijck International Car Rescue, as well as a Google Workspace backup. The monitoring post says the claims are unconfirmed.

A ransomware.live monitoring record attributes a claim of a Prelys Courtage client data breach in France to Anubis. The post says the claim is unconfirmed.
Black X claims it targeted Malaysian manufacturer Tong Kong E & E Sdn Bhd and involved sensitive customer and banking records. The post attributes the information to the group; the claims are unconfirmed.
Ransomware.live lists Sanaa Hospital in Yemen as a Black X ransomware claim, alleging encryption, payment demands and disruption to healthcare systems. The post says it cannot confirm the claims.
Ransomware.live reports that Incransom claims to have exfiltrated 12 TB of data from Harwal Group in the UAE. The post cites the group’s disclosure page and says the claim is unconfirmed.
Akira allegedly claimed Northwood Country Club in Meridian, Mississippi, was affected by ransomware and threatened to upload corporate data, including employee information, financials, contracts, and agreements. The claim is unconfirmed.
Insomnia claimed an attack on Panama-based distributor Sky Solutions, which serves more than 4,000 points of sale. The monitoring post says the claim has not been independently confirmed.
ransomware[.]live records an unverified aurora claim against Bretford Manufacturing, alleging exposure of workforce, banking, network, HR and engineering records. The post says the claims have not been independently confirmed.
Ransomware.live lists StellarRAD Systems as a SpaceBears claim, alleging theft of SQL data, DWG plans, employee and client personal information, financial documents, and APP files. The article says the claim is unconfirmed.
Ransomware.live reports a gunra ransomware claim involving Malaysia’s Weilhotel, dated July 29, 2026. The post says the claim is unconfirmed and provides no official statement from the hotel.
Incransom claims it exposed Della Casa Group AG data, including personal and client information, finance records, and project details. The monitored claim lists 86,332 files; the post says it could not confirm the information.
Ransomware.live records an unverified ransomware claim by coinbasecartel against UK-based ticketing technology provider Accesso. The article cites the actor’s listing but does not independently confirm the claim.
A ransomware.live monitoring post attributes a claim that Deadlock targeted AHENK lab, a medical laboratory in Turkey. The post says the claim is unconfirmed; it provides no evidence of compromise or impact.
A ransomware.live monitoring post attributes to thegentlemen a claim targeting Buck Knives, alleging compromise and disruption to its U.S. operations. The post says the claim could not be verified.
Blacknevas claims it breached Speed Group and exfiltrated more than 1 TB of data, including technical documents, customer databases and production data. No official statement has been issued; the claim is unconfirmed.
ransomware.live records a Qilin claim naming Hoc, a victim in the UK. The post alleges encryption and service disruption, but the article says the claim has not been confirmed.
Ransomware.live lists an unverified Akira claim that 81GB of Franz Krause artworksgroup data will be uploaded, including employee, client, financial and confidential files.
Ransomware.live lists B-K Tool & Design as a victim claimed by cmdorganization. The post says the claim is unconfirmed; the record was discovered and published on July 28, 2026.
A ransomware.live post attributes a Craneware incident claim to Chaos. Craneware’s public statements and filings describe exposed data as non-sensitive or already-public regulatory information; the post says the claim is unconfirmed.