

CRPxO Claims 0.8 GB Data Leak at KUVEYT TURK
Ransomware.live reports that CRPxO claimed KUVEYT TURK in Turkey as a victim and said 0.8 GB of data was leaked. The post says the claim is unconfirmed.
Monitors ransomware victims, threat groups, leak-site activity, and newly disclosed ransomware incidents.
2804 articles
Ransomware.live reports that CRPxO claimed KUVEYT TURK in Turkey as a victim and said 0.8 GB of data was leaked. The post says the claim is unconfirmed.
Ransomware.live lists Additive Manufacturing LLC as a victim claimed by thegentlemen, with a July 31, 2026 discovery and publication date. The post says the claim is unconfirmed and provides no independent evidence or company statement.
Ransomware.live lists Laempe Reich as a victim claimed by the Insomnia ransomware group; the post alleges operational disruption in the US but says the claims are unconfirmed.
The ransomware group insomnia claims Merritt Woodwork in the US as a victim and alleges operational disruption. The claim is attributed to the group’s site and monitored by ransomware[.]live; the article says it cannot confirm the information.
Ransomware.live attributes a ransomware claim against Kenaitze Indian Tribe to thegentlemen. The post alleges disruption to tribal health, education and elder care services; the author says the claim is unconfirmed.
Ransomware.live reports an unconfirmed ransomware claim by thegentlemen against Chilean miner Las Cenizas, with the claim linked to operations in Cabildo, Taltal, and Franke.
Ransomware.live lists Betz Industries as a Booba Project victim, alleging the group stole about 7 GB of data. The post says the claim is unconfirmed.
Interlock claims Gardiner Family Chiropractic patient records, medical histories, and internal financial information were compromised and exposed. The post cites a leak-site source and ransomware.live monitoring; the claim is unconfirmed.

DragonForce claims it targeted UK accountancy firm Lamont Pridmore and took or encrypted confidential internal and client financial documents. The post says the released archive expands to about 250 GB; the claims are unconfirmed.
Ransomware.live lists BLUEVISTALLC[.]COM as a Clop claim dated July 31, 2026. The post says the claim is unconfirmed; it alleges encryption or threatened data exposure.

Ransomware.live lists MBM Law as a DragonForce ransomware-claim victim. The post cites the group’s leak-site source, but says the claim has not been independently confirmed.

DragonForce claimed it targeted U.S. industrial construction services provider RUS Industrial and disrupted operations. The monitoring post says the claim is unconfirmed.
Ransomware[.]live lists Stewart Belland & Associates Inc. as a victim associated with cmdorganization, with a July 31, 2026 discovery and publication date. The listing is based on the group’s public claim and is unconfirmed.
ransomware.live[.] monitors a claim by “pear” against Sonitor Technologies; the article says the group’s claims are unconfirmed.
A ransomware.live monitoring record attributes a claim against MAG USA Inc to securotrop. The listing reports an estimated 1,871 GB of encrypted data, but says the group’s claims are unconfirmed.
A ransomware.live monitoring post attributes a ransomware claim against Hawaii Family Dental to Qilin. The post says files or systems may have been encrypted or disrupted, but notes the group’s claims are unconfirmed.
AguAseo, a Panamanian waste collection and cleaning organization, is listed in a Gammax ransomware claim alleging operational disruption. The listing is based on the group’s public claim and has not been independently confirmed.
A ransomware.live monitoring post attributes a ransomware claim naming RE/MAX 1st Choice to Gammax and says the group threatened to compromise or disclose data. The claim is unconfirmed.
Ransomware.live lists Audio Precision, Inc. as a Qilin ransomware victim, citing the group’s leak-site post. The claim alleges targeting in the U.S.; the publisher says it could not verify the information.
Ransomware.live lists L3Harris as a victim of ransomware activity claimed by the kyber actor, citing an actor leak-site post. The claim, including reported U.S. disruption, is unconfirmed.
Ransomware.live lists C.A. Walker Construction as a Genesis ransomware victim, citing a Genesis leak-site claim dated July 30, 2026. The post says the allegation is unconfirmed.
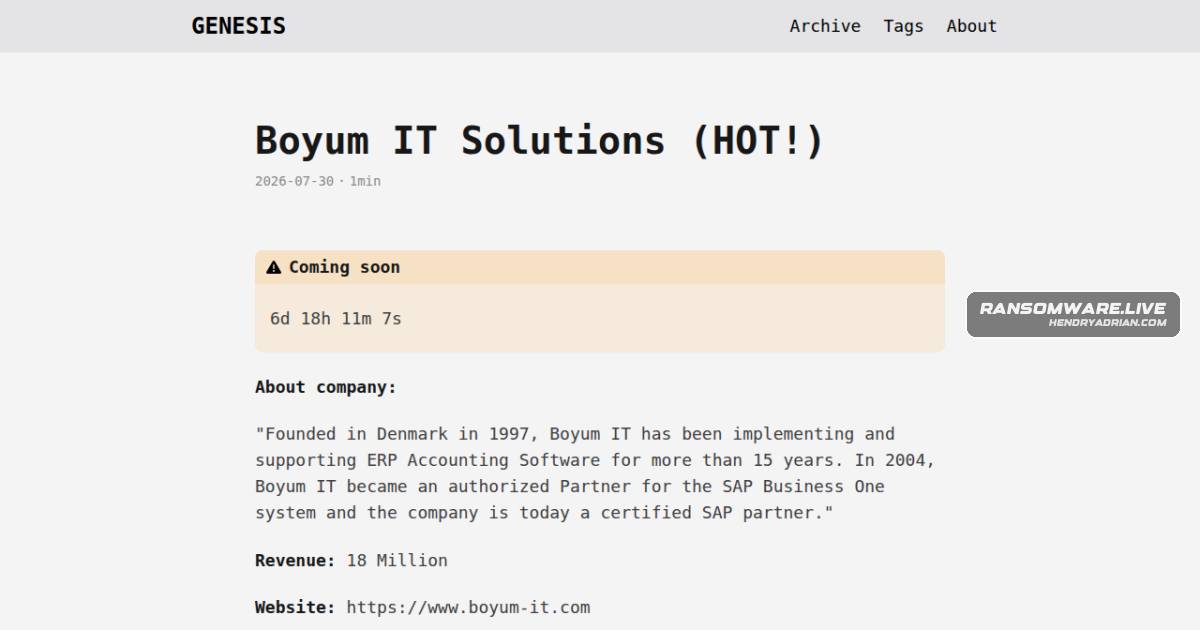
Ransomware.live reports that Genesis claims Boyum IT Solutions, an IT services provider in Denmark, as a victim. The post says business systems and data were compromised, but notes the group’s claim is unconfirmed.
cmdorganization claims an intrusion affected Contact Group, an Australian building services provider. The claim is unconfirmed and was monitored by ransomware[.]live.
Incransom claims it stole 3.2 TB of data from Australia’s Partnered Health Group in June 2026, including patient and staff records. The post cites the group’s leak-site disclosure; the claims are unconfirmed.