
Aurora Claims to Have Compromised Evosys Laser GmbH
Summary
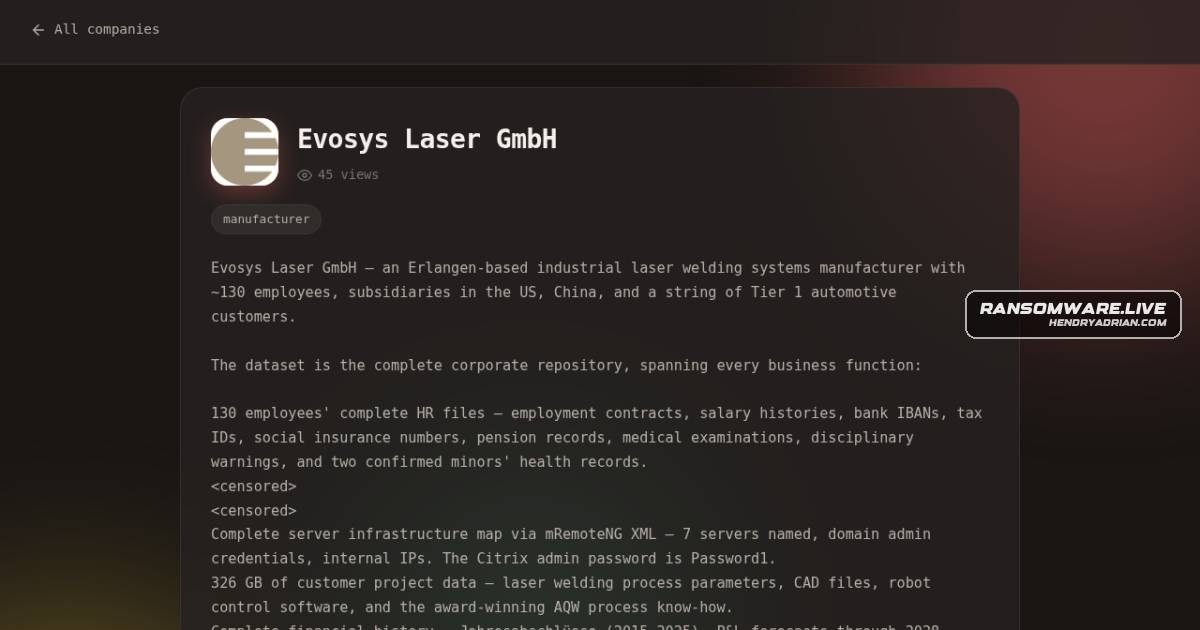
Aurora claims it compromised Evosys Laser GmbH and exposed corporate data, including HR records, infrastructure credentials, customer projects and industrial-control files. The claim is unverified; ransomware[.]live cites the group’s public post.
Key points
- Aurora’s leak-site post claims Evosys Laser GmbH’s corporate repository was compromised; the claim is unverified.
- The post alleges exposure of HR records, including sensitive personal and medical information.
- It claims server infrastructure data included domain administrator credentials and a Citrix administrator password.
- The group claims access to 326 GB of customer project data, including CAD files and robot-control software.
- The post also claims exposure of industrial-control files, PLC programs, private keys and customer VPN configurations.
Article Details
- Victim
- Evosys Laser GmbH
- Claim Date
- 2026-07-30
- Encryption Status
- Unknown
- Exfiltration Status
- Claimed by aurora; not independently confirmed
- Exfiltrated Data
- The claim describes a complete corporate repository, including HR records, customer project data, financial records, server infrastructure information, and industrial control data. The source says it cannot confirm the claim's accuracy.
- Exfiltrated Size
- 326 GB of customer project data claimed; not independently verified
- Leak Status
- A claim was published on aurora's blog; the source does not confirm that data was publicly leaked or verify the claim's authenticity.
Threat Actors
Products
CitrixComplete server infrastructure map via mRemoteNG XML, including seven named servers, domain admin credentials, internal IPs, and the Citrix admin password.mRemoteNGinvolving the compromise of its complete corporate repository, including HR, server infrastructure (mRemoteNG XML with domain admin credentials), and customer project data.NGINXIndustrial control data, including robot SRS source code, PLC programs, nginx private keys for laser system web interfaces, and VPN configurations for customer site remote access.