
Incransom Claims Lantis Enterprises as a Ransomware Victim
Ransomware.live reports that incransom listed Lantis Enterprises (lantisnet[.]com) in a ransomware claim. The post says US systems and operations were affected; the claim is unconfirmed.
Monitors ransomware victims, threat groups, leak-site activity, and newly disclosed ransomware incidents.
2802 articles
Ransomware.live reports that incransom listed Lantis Enterprises (lantisnet[.]com) in a ransomware claim. The post says US systems and operations were affected; the claim is unconfirmed.
Ransomware.live lists Preferred Financial Group as a Play ransomware victim; the post attributes claims of unauthorized access and business disruption to the group but says they are unconfirmed.
Ransomware.live lists First Tek, a technology company in Taiwan, as a Play ransomware target, citing the group’s leak-site claim. The publisher says it could not confirm the claim.
Ransomware.live records an Incransom claim against TRULITE GLASS & ALUMINUM SOLUTIONS, alleging access and theft of more than 8 TB of data and threatening publication. The post says the claims are unconfirmed.
The krybit ransomware group claims it targeted Brazil's CESMAC University Center. The monitoring post lists the claim as discovered and published on Aug. 4, 2026, and says it could not verify the information.
Qilin claims it targeted German manufacturer RUPP Spritzguss. The monitoring post attributes the claim to Qilin’s leak site and says disruption and data encryption occurred; the information is unconfirmed.
A ransomware.live record says Qilin claimed Galvin Brothers, an Irish manufacturing company, as a victim. The post attributes the claim to Qilin’s leak site and says the incident details are unconfirmed.

Ransomware.live lists University SprinklerSystems as a victim in an Akira claim alleging access to and exfiltration of employee, client, and internal files; the post says it could not verify the claim.
Ransomware.live lists WD Masonry & Concrete as a Qilin ransomware claim, citing the group's leak-site post. The monitoring post says the claim is unconfirmed.
Ransomware.live lists Worldtube, a South Korean automotive-parts manufacturer, as a Gunra ransomware target based on the group's public claim; the alleged incident and reported operational impact are unconfirmed.
A ransomware claim attributed to Orova names Taiwan-based DBM Reflex. The report cites a leak-site source and ransomware.live monitoring, but says the claim is unconfirmed.
A ransomware.live monitoring post attributes a ransomware incident claim involving Agricultural Chemical Solutions to Orova. The post says operations were disrupted, but notes the claim is unconfirmed.
Ransomware.live lists SBI Manufacturing, a Sioux Falls metal fabrication and machine welding company, as a victim claimed by Orova. The post says operations were disrupted and files encrypted, but these claims are unconfirmed.
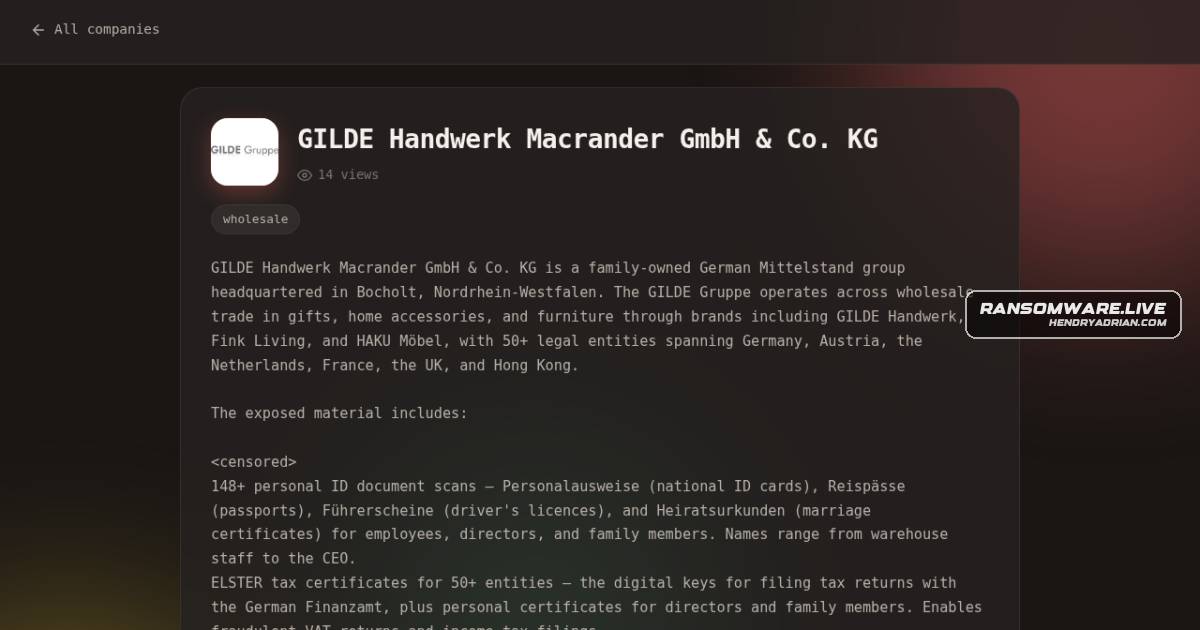
The Aurora ransomware group claims it holds sensitive records from GILDE Handwerk Macrander GmbH & Co. KG, including identity documents, payroll, tax and financial records. The claim is unverified and attributed to the group by ransomware.live.
Incransom claims it targeted Philippine retailer and property developer Liberty Commercial Center (LCC), identified as lccgroup[.]com. The ransomware.live post cites the group's disclosure and says the claim is unconfirmed.
Ransomware[.]live lists pushidrosal[.]id as a victim claimed by the incransom group, citing its disclosure page. The report says it cannot confirm the claim.
Ransomware.live monitored an Aurora ransomware claim naming US Installation Group, Inc. The group’s claim is unconfirmed, and the article provides no independent evidence of compromise or disruption.
A ransomware.live monitoring record attributes to incransom a claim of obtaining data from Argentina’s Oleoductos del Valle, including HR, financial, tax, and personal records. The claim is unconfirmed.
Incransom listed Clinton Health Access (clintonhealthaccess[.]org) as a ransomware victim and made unverified allegations involving the Clinton Foundation and cryptocurrency transactions. The monitor says it cannot confirm the claims.
Ransomware.live lists hanan-hov[.]co[.]il as a SafePay claim and alleges disruption to logistics operations in Israel. The post says the group's claims are unconfirmed.
Ransomware.live records an unverified SafePay claim targeting Simonrack, a Spanish metal-shelving manufacturer. The claim was posted on SafePay's leak site on August 3, 2026; the article says it cannot confirm the information.
A ransomware.live record attributes a claim targeting Italy-based new-point[.]it to Safepay and reports operational disruption. The post says the information comes from the group’s public claims and is unconfirmed.
Ransomware.live recorded a SafePay claim naming naskdoorinc[.]com, a Pennsylvania manufacturer, on Aug. 3, 2026. The post alleges operational disruption; the site says it could not verify the claim.
SafePay claims it targeted pradotuylaw[.]com, described as a U.S. law firm. The claim was reported by ransomware.live; the article says it could not confirm the information.