
Play Ransomware Claim Names First Tek in Taiwan
Summary
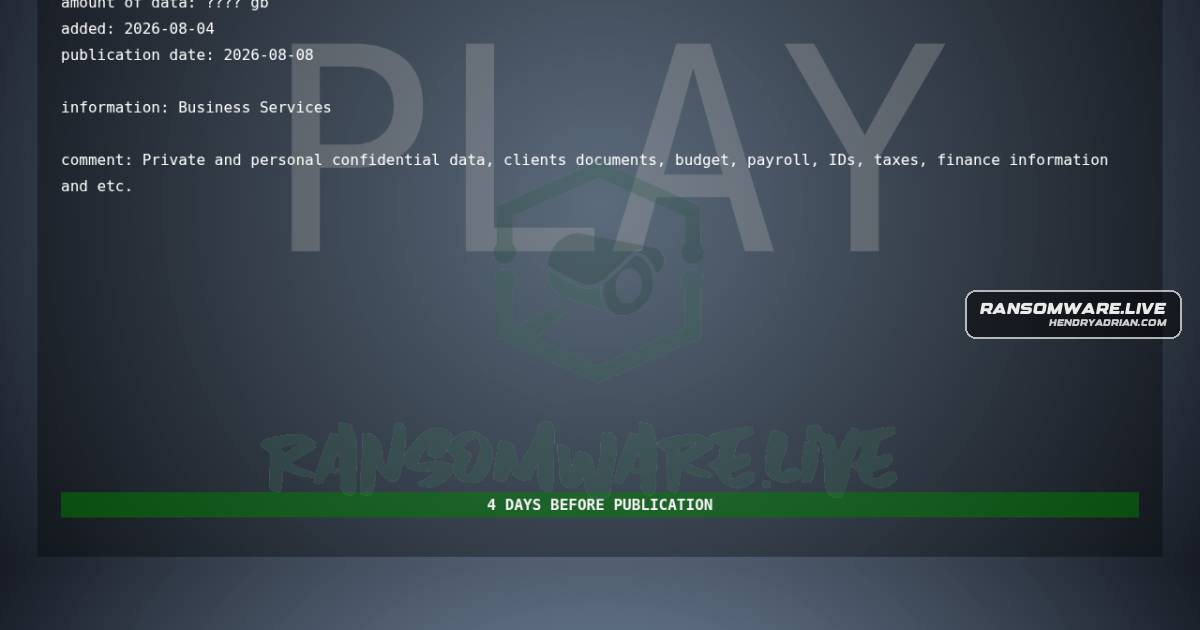
Ransomware.live lists First Tek, a technology company in Taiwan, as a Play ransomware target, citing the group’s leak-site claim. The publisher says it could not confirm the claim.
Key points
- The record names First Tek as the victim and Play as the ransomware actor.
- The claim is attributed to a Play leak-site post and monitored by ransomware.live.
- The publisher says it could not confirm the claim and invites an official statement from First Tek.
- The record alleges unauthorized access, file encryption, disruption and ransom demands; it provides no independent evidence for these claims.
Article Details
- Victim
- First Tek
- Victim Domain
- Unknown
- Claim Date
- 2026-08-04
- Encryption Status
- Encryption was reported in the public group claim; unverified.
- Encrypted Size
- Unknown
- Exfiltration Status
- Unknown
- Exfiltrated Data
- Unknown
- Exfiltrated Size
- Unknown
- Ransom Demand
- An attempted ransom demand was reported, but no amount was disclosed; unverified.
- Leak Status
- Unknown
Threat Actors
Countries
TaiwanFirst Tek in Taiwan was targeted by the play ransomware threat actor, associated with the United States, leading to unauthorized access and encryption of victim files.United StatesFirst Tek in Taiwan was targeted by the play ransomware threat actor, associated with the United States, leading to unauthorized access and encryption of victim files.