
Qilin Claims Attack on Romanian University
A Qilin leak-site claim says Universitatea De Vest Vasile Goldi Din Arad in Romania was targeted. The monitoring post says it cannot confirm the claim; no incident details are provided.
Monitors ransomware victims, threat groups, leak-site activity, and newly disclosed ransomware incidents.
2803 articles
A Qilin leak-site claim says Universitatea De Vest Vasile Goldi Din Arad in Romania was targeted. The monitoring post says it cannot confirm the claim; no incident details are provided.
A ransomware.live monitoring record attributes a ransomware claim involving Pioneer Coldstore & Cladding (pcclimitedindia[.]com) to lockbit5. The claim is unconfirmed.

Akira claims it will upload 16GB of Belasco Electric data, potentially including employee personal information and business records. The claim is unconfirmed; the article says it is monitored by ransomware.live.
A ransomware.live monitoring record says Akira claims it will publish 30 GB of Albers Mechanical Contractors data, including employee information, financial records, contracts, NDAs, and customer information. The claim is unconfirmed.
Qilin's leak site listed Service Electric as a ransomware victim. The monitoring post says systems were reportedly encrypted or inaccessible, but the claim has not been confirmed.
Ransomware[.]live reports that RansomHouse claimed an attack on Thailand-based PCL Holding. The post says operations were impacted, but provides no independent confirmation; the author says the claim could not be verified.
LockBit 5 allegedly listed SMS-SME as a ransomware target, according to a ransomware.live monitoring record citing the group's post. The claim is unconfirmed, and no incident impact is detailed.
LockBit 5 claims Sirsa, an Italian plastics processor, was affected by ransomware. The claim is listed by ransomware.live, and the source says it could not confirm the information.

DragonForce claims TUI China was affected and says passports, visas, internal documentation, and legal and financial records are involved. The monitoring post says the claim is unconfirmed.
ShinyHunters claimed Alcon Inc. was compromised, affecting over 25 million Salesforce records containing some PII, and set an August 4, 2026 deadline before a possible data leak. The claim is unconfirmed.
A ransomware.live monitoring post attributes an unconfirmed ransomware claim targeting US manufacturer Wire Products to Qilin. The post says it is based on the group’s public claim and cannot confirm its accuracy.
Qilin claims it compromised Freedom Claims Management and threatens to leak data unless demands are met. The monitoring post attributes the claim to Qilin; the incident is unconfirmed.
Ransomware.live records an unconfirmed krybit claim naming South African company Buzz Trading 104 (Pty) Ltd, trading as Master Products; the post says the attack affected operations and data access.
Incransom claims it deployed ransomware against the Evangelical Council for Financial Accountability (ECFA), according to ransomware[.]live. The article says the claim has not been independently confirmed.
Ransomware.live lists ProHealth Medical Group Pte Ltd (prohealth[.]sg) as a krybit claim dated Aug. 2, 2026. The post alleges operational disruption, but says the claim is unconfirmed.
A ransomware.live monitoring post attributes a claim against Asset Flooring Group Australia to Qilin, alleging system-access disruption and encrypted files. The post says the claims are unconfirmed.
A ransomware.live monitoring post attributes a claim targeting INTERTRUST AUSTRALIA PTY LTD in Australia to Qilin. The post says the claim’s accuracy is unconfirmed.
Ransomware.live lists Moses & Singer LLP as a victim of a SilentRansomGroup claim, discovered and published Aug. 2, 2026. The post says the claim is unconfirmed and provides no incident details.
Ransomware.live lists Country Motos S.A. de C.V. (Country Motors/Country Honda), a Mexican motorcycle dealership, as a claimed Krybit ransomware victim. The claim, attributed to a Krybit post dated Aug. 2, 2026, is unconfirmed.
A ransomware.live record attributes a claim involving Mairie de Drancy to Qilin. The post says services were disrupted and files encrypted, but notes the information is based on the group's public claim and is unconfirmed.
Ransomware.live lists a public ransomware claim by krybit concerning the Municipality of Rinxent’s official website in France. The article says the claim is unconfirmed; compromise details are not verified.
Ransomware.live reports a Krybit claim targeting ASHA Microfinance Bank Limited (ASA Nigeria). The post says operations were affected, but the claim is unconfirmed.
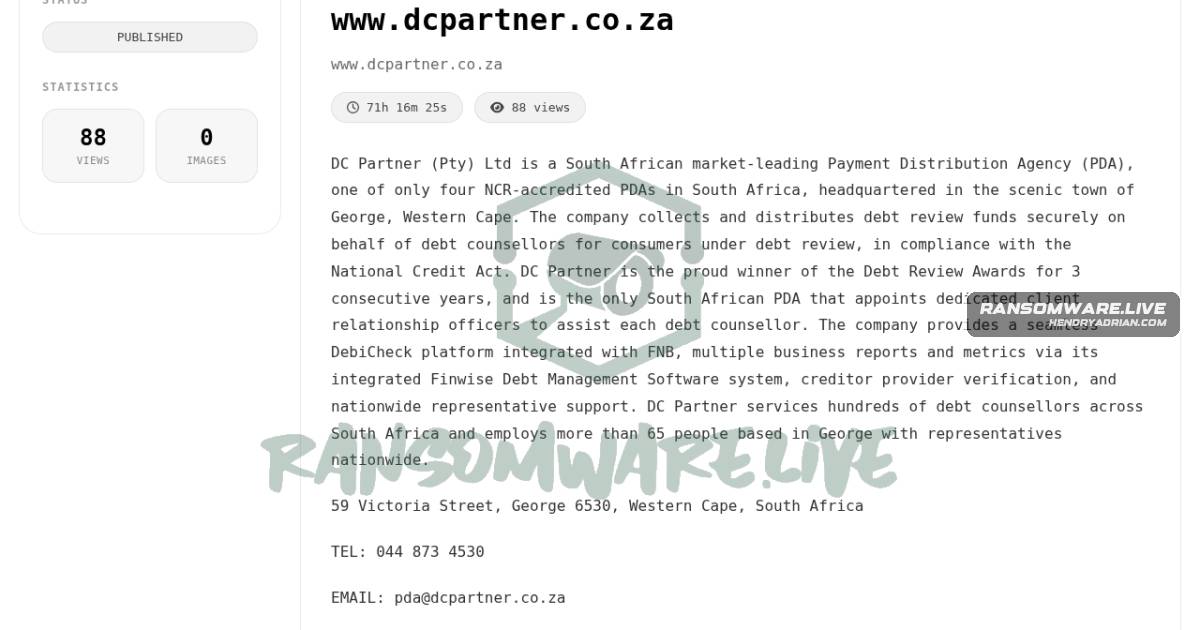
Ransomware.live lists DC Partner (Pty) Ltd, a South African payment distribution agency, as a krybit ransomware victim. The post alleges operational disruption; the publisher says the claim is unconfirmed.
Ransomware.live records a CRPxO claim that Encore Enterprises, Inc. was targeted and 700 GB of data leaked; the post says the claim is unconfirmed.