
Ransomware actor iah6477 claims ProAmpac as a victim
A ransomware-monitoring post attributes a claim against U.S. manufacturer ProAmpac to actor iah6477 and reports 745.3 GiB of data. The post says the claim is unconfirmed.
Monitors ransomware victims, threat groups, leak-site activity, and newly disclosed ransomware incidents.
2781 articles
A ransomware-monitoring post attributes a claim against U.S. manufacturer ProAmpac to actor iah6477 and reports 745.3 GiB of data. The post says the claim is unconfirmed.
A ransomware claim attributed to pear names NEXT LEVEL MEDICAL, LLC, a Texas urgent-care provider. The post says the claim is unconfirmed; its reported operational impact has not been independently established.
ransomware[.]live lists an unconfirmed Krybit claim targeting Ferretornillos, S.A. in Guatemala. The post claims disruption and encrypted data; no confirmation from the company is provided.
Ransomware.live lists Malaysia’s KenEp Resources as a Qilin ransomware victim, citing the group’s leak-site claim. The report alleges disruption to access to critical files and systems; the claim is unconfirmed.
Ransomware.live lists Sanatorio Modelo de Caseros in Argentina as a Qilin ransomware claim dated Aug. 26, 2026. The post alleges encryption and disruption but says the information is unconfirmed.
Ransomware.live reports that actor krybit claimed to target India-based healthcare platform Karkinos Healthcare and disrupt services. The post says the claim is unconfirmed.
ransomware.live reports an unconfirmed ransomware claim by krybit against Le Conseil Gabonais des Chargeurs (cgcgabon[.]com), citing the group’s leak site. The record is dated August 26, 2026.
Krybit claims it targeted Finodaya Capital Private Limited, alleging operational disruption and possible data exfiltration. The claim was monitored by ransomware[.]live and is unconfirmed.
Ransomware.live reported a Qilin claim naming UK manufacturer Metal Conversions, published on August 26, 2026. The group’s claim is unconfirmed; the article says it could not verify the information.

Akira claims it will exfiltrate 119 GB of PA-ID data and publish it. The ransomware.live post says the alleged data includes employee IDs, client information, financial records and NDAs; the claim is unconfirmed.
Akira allegedly threatened to upload 14GB of data from Oral and Maxillofacial Surgery in Brockton, including employee, client, financial and patient information. The claim is unconfirmed.
A ransomware.live monitoring record attributes to Qilin a claim that it targeted Romanian manufacturer SC PaderTeG Cabluri Electrice and encrypted files, reportedly disrupting operations. The post says the claims are unconfirmed.
Chaos claims it breached Central Ohio Primary Care (copcp[.]com) and may publish information after alleged failed outreach. ransomware.live says it cannot confirm the claim.
The Chaos ransomware group claims it will publish information about MS Walker after the organization did not engage. The claim is unconfirmed; the monitoring post says it cannot verify the group’s allegations.
Chaos claims it targeted Park de Rochie (parkderochie[.]com) and says it will publish more details. The claim is attributed to the group’s post and monitored by ransomware.live; the article says it cannot confirm the claims.
A ransomware.live entry attributes to SafePay an unconfirmed claim of access to systems associated with Air Liquide in South Korea. The record identifies industry[.]airliquide[.]kr as the victim.
Ransomware.live recorded a Qilin claim naming Brazosport College. The post says the claim is unconfirmed; it provides no independent verification of compromise, encryption, or data theft.
A ransomware.live monitoring post attributes an unverified ransomware claim against Taiwanese CPA practice Bai-chi CPA Firm to Orova. The post alleges data and operational impact but says the claims could not be confirmed.
A monitoring post attributes to Orova a ransomware claim involving Arich Enterprise’s pharmaceutical marketing operations and customer network. The post says the information is unconfirmed.
Orova reportedly claimed a ransomware attack on Central Florida Civil LLC, a Florida underground utilities and site development company. The claim was listed on a leak site and monitored by ransomware.live; it is unconfirmed.
Ransomware.live reports an unconfirmed direwolf claim targeting Italian law firm Studio Legale ESE. The group reportedly claimed encryption, operational disruption, and a ransom demand; the article says these claims are unverified.
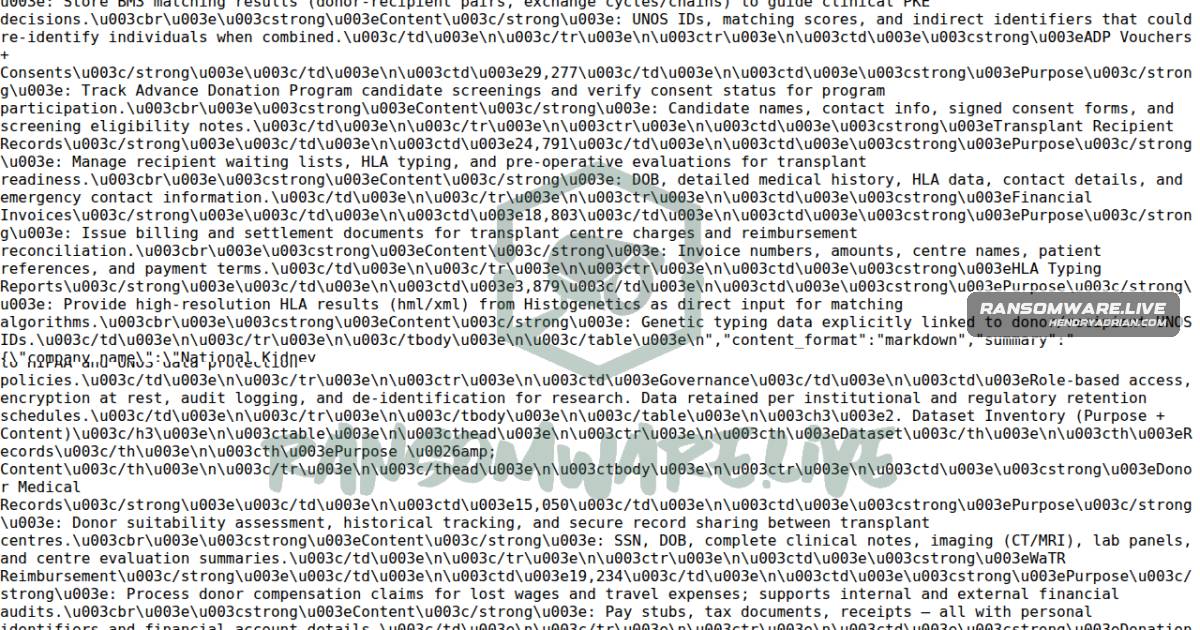
Direwolf claimed a ransomware incident involving National Kidney Registry, which coordinates kidney paired donations. The claim is unconfirmed; the article provides no independent evidence of compromise or service disruption.
Ransomware.live lists ShadowByt3$’s unconfirmed claim that it accessed Knottingham Trent University’s portal, stole personal and academic data, and threatened to leak it unless demands were met.
ShadowByt3$ claims it accessed A-Plus Software Limited via SQL injection and downloaded backend and website data. The ransomware.live post says the claim is unconfirmed.