
ShadowByt3$ Claims Theft of 375.66 MB From Sinar Mas Agribusiness
Ransomware.live records an unconfirmed ShadowByt3$ claim that it stole 375.66 MB of data from Sinar Mas Agribusiness and Food (Golden Agri-Resources).
Monitors ransomware victims, threat groups, leak-site activity, and newly disclosed ransomware incidents.
2786 articles
Ransomware.live records an unconfirmed ShadowByt3$ claim that it stole 375.66 MB of data from Sinar Mas Agribusiness and Food (Golden Agri-Resources).

A ransomware.live monitoring post attributes a claim that 1,844 files from Malaysia’s PCA Group Sdn. Bhd. were exposed to majinahanashi. The claim is unconfirmed.
Dark Project claims it stole 120,000 files totaling 115 GB from Pump Engineering Company, including customer, insurance, financial and project records. The post says the claim is unconfirmed.
A ransomware.live monitoring record attributes a ransomware claim against engineering software provider Cosmon to the beast group. The article says the claim is unconfirmed.
A ransomware.live monitoring record attributes an unverified encryption and data-theft claim to Akira, alleging 392GB was taken from Boustead International Heaters in Germany, including employee and business records.

Ransomware.live lists Wozair in the UAE as a DragonForce ransomware claim, citing the group's blog. The post says Wozair's HVAC operations were impacted, but the claim is unconfirmed.

A ransomware.live listing attributes to Dragonforce an unverified claim that data from Brookview Financial, including sensitive customer information, was exfiltrated. The post says the information relates to many thousands of customers.
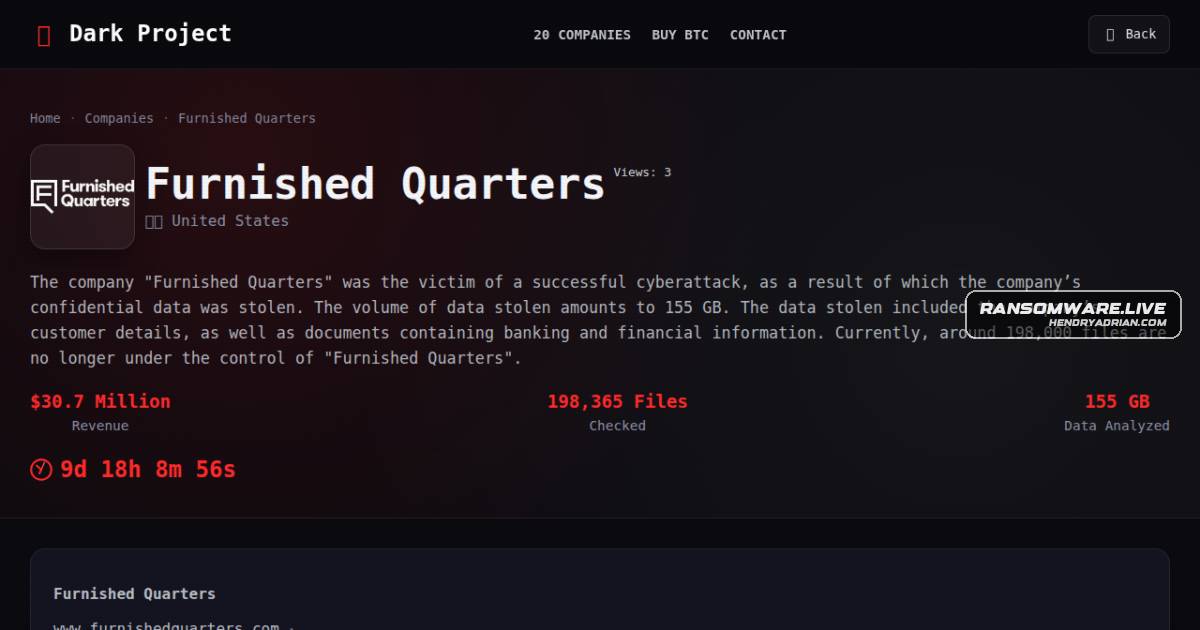
Dark Project claims it stole 155 GB of data from Furnished Quarters, including customer details and banking and financial documents. The post says about 198,000 files are affected; the claim is unconfirmed.
Dark Project claims it compromised Design-Aire Engineering’s service systems and stole about 377GB of data, including employee personal information and client architectural plans. The monitoring post says the claims are unconfirmed.
Ransomware.live lists Jones, Little & Co., CPAs, LLP as a Dark Project victim. The group claims it stole at least 100 GB of data and encrypted systems; the publisher says the claims are unconfirmed.
Ransomware[.]live lists South Africa’s Furniture Bargaining Council (FBC) as impacted by Deadlock. The post attributes the claim to the ransomware group and says it is unconfirmed.
Deadlock claims it stole 27 GB of files from Shaheen Law Group, including client, financial, identity, medical and transaction records. The monitoring post says the claim is unconfirmed.
Qilin claims it compromised Consultores de Seguros and encrypted data, potentially disrupting operations. The claim was listed on August 24, 2026, and is unverified.
A monitoring post attributes to Dark Project a claim that it stole about 27,000 files from The Liberty Group and encrypted company systems, disrupting operations. The claims are unconfirmed.
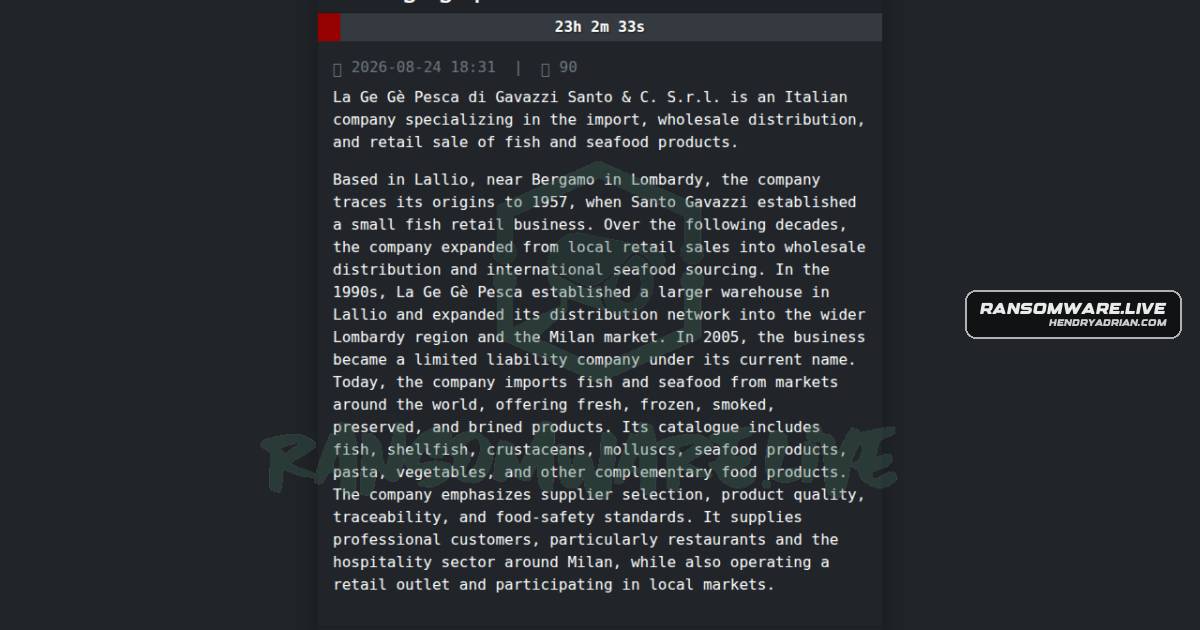
A ransomware.live record attributes a claim against lagegepesca.it to SafePay and links to the group’s leak-site post. The record says systems were encrypted and services disrupted, but notes the group’s claims are unconfirmed.
Ransomware.live reports an incransom claim against FFKR Architects, an architecture firm with offices in Utah, Arizona, and Idaho. The post says the attack affected US operations but notes the claim is unconfirmed.

DragonForce reportedly claimed Criba’s data included financial and client documents and information from Argentina, Uruguay, and other countries. The claim is unconfirmed.

DragonForce claims it exposed data from Brazil’s Frato, including financial, shareholder, employee and client information. The monitoring post says the claim is unconfirmed.
Ransomware.live lists A&E + SMA Design as a Qilin ransomware target, citing a Qilin leak-site URL. The record is based on the group’s claim and has not been independently confirmed.
ransomware[.]live lists Senvibe as a Panzer ransomware claim, discovered Aug. 24, 2026. The post says the claim is based on the group’s public statements and is unconfirmed.
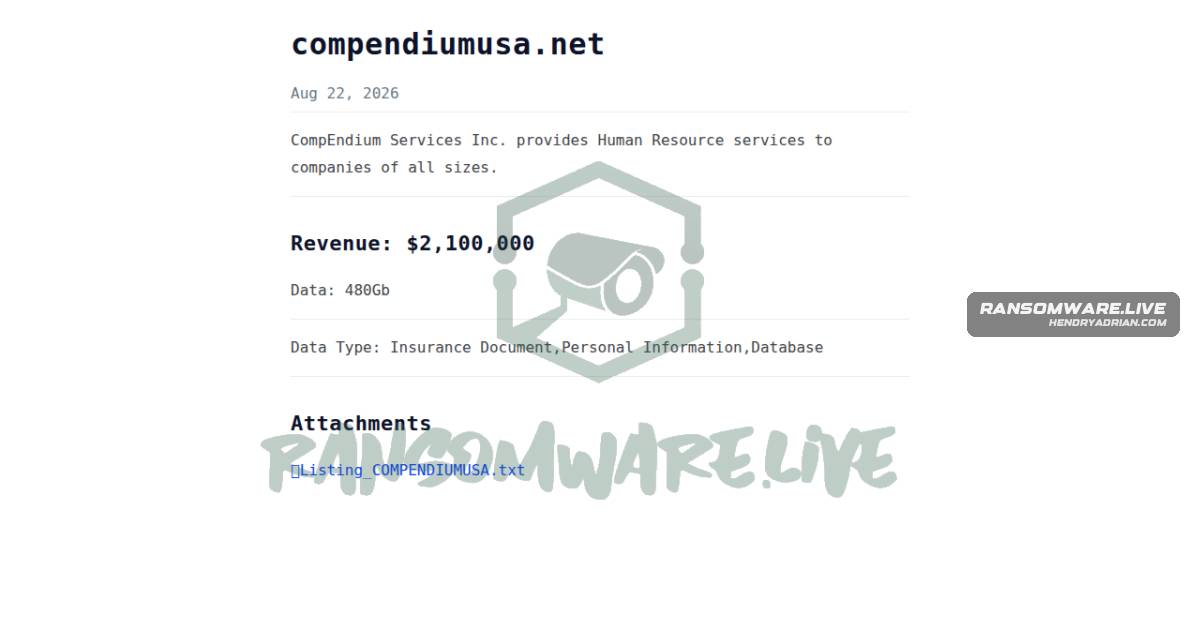
L Group claims it deployed ransomware against compendiumusa[.]net and threatened disruption to the organization’s data and systems. ransomware[.]live says the claim is unconfirmed.
Qilin claimed it attacked Aurore Development S.p.A. in Italy and encrypted files. The ransomware.live post says the claim is unconfirmed.
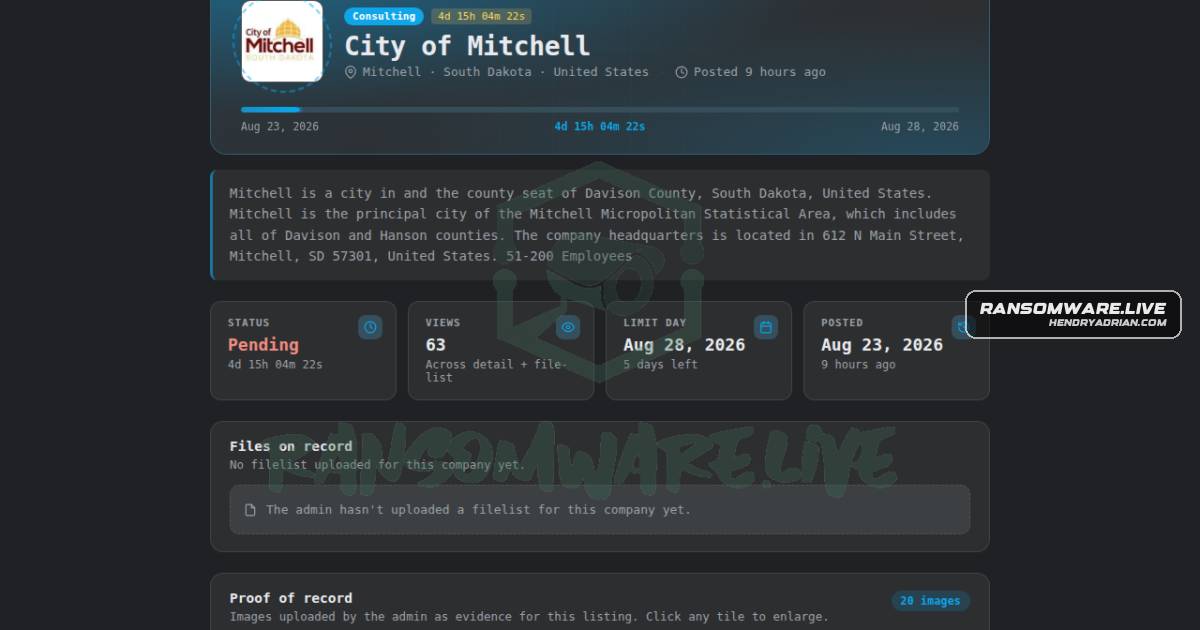
A ransomware.live monitoring record attributes a claim against the City of Mitchell to Storm. The post alleges data encryption and service disruption, but says the claims are unconfirmed.
Ransomware.live reports that Storm listed Sharp Motor Group, an automotive dealership group in Tweed Heads, Australia. The claim is unconfirmed; the article provides no independently verified incident details.