

Majinahanashi claims planned leak of 6,341 MONTCAU files
Ransomware[.]live monitoring records a Majinahanashi claim that MONTCAU faces a scheduled leak involving 6,341 files; the post says the claim is unconfirmed.
Monitors ransomware victims, threat groups, leak-site activity, and newly disclosed ransomware incidents.
2781 articles
Ransomware[.]live monitoring records a Majinahanashi claim that MONTCAU faces a scheduled leak involving 6,341 files; the post says the claim is unconfirmed.
A monitoring post lists South Pacific Hotel Limited in Hong Kong as a ransomware victim claimed by Orova. The post says the claim is unverified and provides no independently confirmed details of compromise or impact.
Ransomware.live records ShadowByt3$’s unverified claim that BayView Real Estate was breached and data stolen. The post describes a 216.6 MB archive and provides mirror links, but says it cannot confirm the claims.
Ransomware group iah6477 claimed trc-companies was affected and reported 4.2 TiB of data. The monitoring post says the claim is unconfirmed.
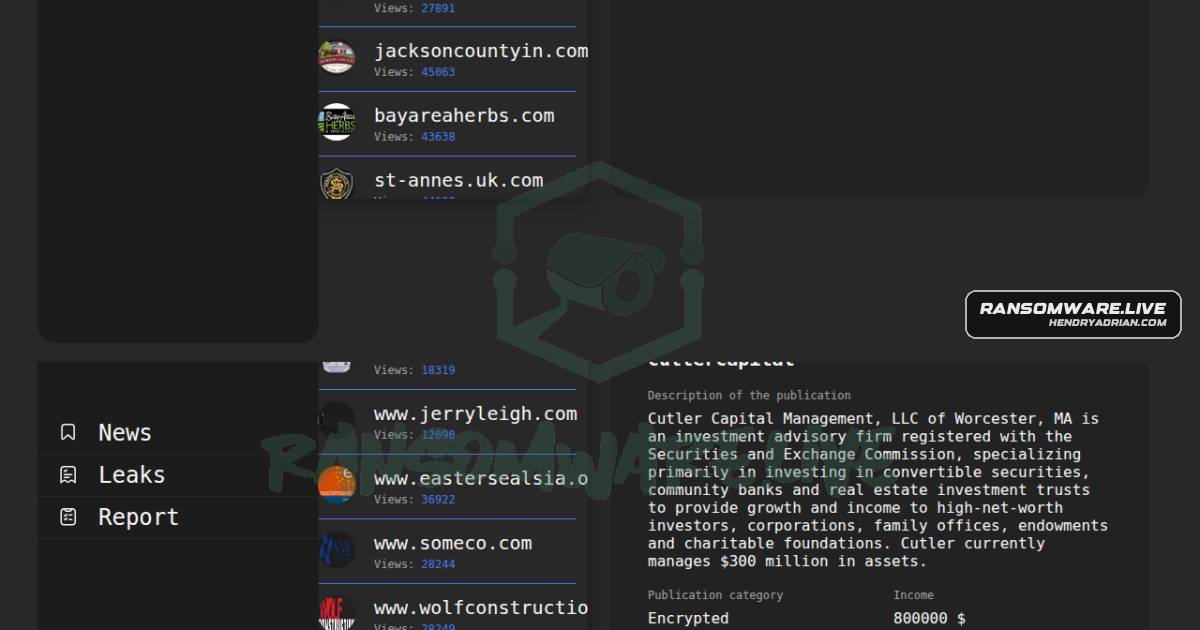
Ransomware.live lists Cutler Capital Management, LLC as targeted by the Lynx ransomware actor, citing the actor’s leak-site post. The claim is unverified; the article does not confirm compromised data or other incident impact.
A ransomware.live monitoring post attributes an unconfirmed ransomware-activity claim against Hangzhou Qihan Biotech to the group “global”; it says data and operations were affected, but provides no independent confirmation.
A ransomware.live-monitored post attributes to the group “global” an unconfirmed claim that it compromised Uruguay-based Vigilia, disrupting care, ambulance, insurance and medical-coordination services.
Rhysida claims it encrypted and exfiltrated 9,056,196 files from Valley Health Team, including patient and financial data. The claim is attributed to the group’s leak-site listing and is unconfirmed.
Qilin claimed Tramigo, a Finnish transportation company, as a victim and reportedly claimed encryption and operational disruption. The post attributes the information to the group's leak site and says the claims are unconfirmed.
Ransomware.live lists Australian technology company DigiGround as a Qilin target; the group reportedly claims encryption and a ransom demand. The post says the claims are unconfirmed.
Ransomware.live lists Otto Sieve GmbH, a German building services company, in a Storm ransomware claim. The post says the claim is unconfirmed; no independent evidence of disruption or data impact is provided.
A ransomware.live monitoring post attributes a ransomware claim naming Whitehouse in the UK to Qilin. The post says the claim is unconfirmed.
Ransomware.live lists Infinnium as a Qilin ransomware victim, citing the group's public claim. The post says the claim is unconfirmed; no statement from Infinnium is included.

A ransomware.live monitoring post attributes an unverified ransomware claim involving Caduceus Medical Group to Anubis. The post says the information cannot be confirmed.
Ransomware.live reports that LockBit5 claims to have targeted the Tennessee Medical Association. The claim is unconfirmed, and the record provides no incident impact or technical details.

ShadowByt3$ claims it sent Bayview Real Estate extortion emails and stole 216.6 MB of data, threatening a leak unless contacted by Aug. 29, 2026. The claims are unverified.
Ransomware.live reports that the Storm group claimed to have targeted German language academy Sprachakademie Rhein-Ruhr in Duisburg. The claim is unverified.
Ransomware.live lists Singleton Reynolds (singleton[.]com) as a Chaos ransomware claim published Aug. 27, 2026. The post says the claim is unconfirmed and its accuracy could not be verified.
Ransomware[.]live lists ETNA Software as a claimed Eclipse ransomware victim, citing the group's leak-site post. The claim says trading services were disrupted, but the article says it is unconfirmed.
Ransomware.live lists Agrimac as a Storm ransomware victim, citing a Storm-linked onion page. The post says the claim is unconfirmed and provides no details of impact or stolen data.
A ransomware.live monitoring record attributes a ransomware claim against Globalport Terminals in the Philippines to Qilin. The group’s claims of encryption and operational disruption are unconfirmed.
incransom claims it has 536 GB of data from Rohloff Group, including employee personal and financial records. The monitoring post says full publication is forthcoming and notes the claim is unconfirmed.
Ransomware.live records a Qilin ransomware claim against Providence Investments, a US financial-services firm, dated Aug. 27, 2026. The post says systems were disrupted and data may be affected, but the claims are unconfirmed.
MedusaLocker reportedly claimed it targeted Jgsee in Thailand and extracted four email addresses. The report attributes the information to the group’s public claim and says it could not confirm its accuracy.