
Play Ransomware Claim Names Roxiticus Golf Club
Ransomware.live lists Roxiticus Golf Club in the US as a target of the Play ransomware group. The claim is attributed to the group and remains unverified.
Monitors ransomware victims, threat groups, leak-site activity, and newly disclosed ransomware incidents.
2843 articles
Ransomware.live lists Roxiticus Golf Club in the US as a target of the Play ransomware group. The claim is attributed to the group and remains unverified.
Ransomware[.]live records an unverified Play claim involving All Real Estate Title Solutions. The post says the actor intends to encrypt systems and exfiltrate data; it provides no independent confirmation.
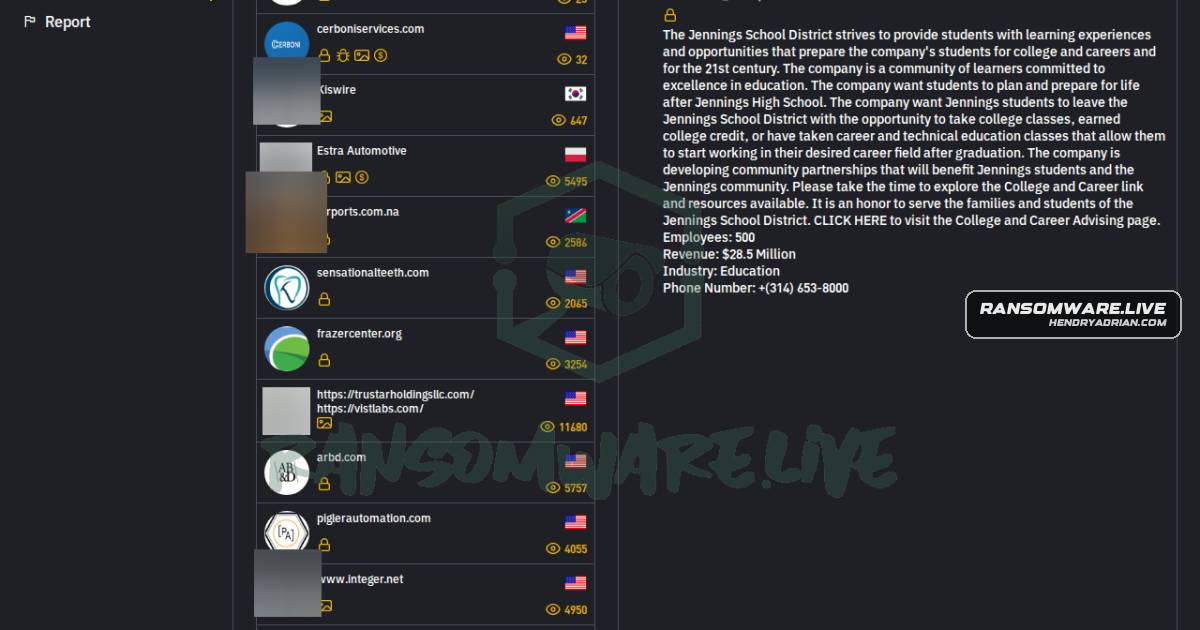
A ransomware.live monitoring post attributes an unverified ransomware claim against Jennings School District to incransom. It says the district and authorities are investigating; no ransom amount or extent of data exfiltration is disclosed.
A ransomware.live monitoring post attributes claims of data encryption and a ransom demand involving PWNA Plains to incransom. The post says the claims are unconfirmed.
Incransom claims it exfiltrated data from cerboniservices[.]com and threatens public release unless a ransom is paid. The claim is unconfirmed.

ShinyHunters claims it obtained 27GB of Berkadia Salesforce records containing PII and internal data; the monitoring post says the claim is unconfirmed.
A ransomware claim attributed to Qilin lists Retail Centenario as a victim. The claim was reported by ransomware.live on March 24, 2026, but the post says it could not confirm the information; no further incident details are provided.
Aroostook Mental Health Services is listed in a Qilin ransomware claim recorded on March 24, 2026. The post says the claim is unverified and provides no details on impact, encryption, or ransom payments.
Akira claims it plans to publish 138 GB of Mooers Immigration data, including sensitive client documents. The claim is unverified; the article provides no independent confirmation that the data was accessed or obtained.
Akira claims it exfiltrated about 17 GB of data from Concord Components, Wefapress, Environment Masters, Fairmont Hot Springs Resort, and Road America, including sensitive employee and business records. The claims are unconfirmed.
Worldleaks claims it compromised Marion Military Institute and threatens to publish information after a countdown of just over one day. The claim is unconfirmed, and the group has not specified what data was allegedly taken.
Lapsus$ claims it stole roughly 3GB of AstraZeneca data, including credentials, code and employee information, and listed the company on its leak site. AstraZeneca has not confirmed the claim; a possible link to the Trivy attack is disputed.
Akira claims it will release 72 GB of French Engineering data unless extortion demands are met. The ransomware.live-monitored post says the data includes employee records and confidential documents; the claim is unconfirmed.

DragonForce claims it attacked M3 Group, alleging file encryption and threatening to release data. The monitoring post says the claim is unconfirmed.
Gunra claims BKK Sky and Trio-Tech International as victims. The group alleges about 560 GB of Trio-Tech data was exfiltrated, including employee files, credentials, internal audits, HR data and customer information.
Ransomware.live lists an unverified thegentlemen claim targeting Japan-based Omikenshi, alleging a payment demand for decryption and to prevent public release of sensitive information.
A ransomware claim attributed to crypto24 names Buenos Aires law firm Estudio O’Farrell. The report alleges operational disruption and a threat involving sensitive client data; the claim has not been confirmed.
The ransomware group thegentlemen claims it targeted Peru-based Grupo Tawa and threatens to leak or block access to data unless paid. The monitored claim is unverified; the article says its accuracy could not be confirmed.
TheGentlemen claims it breached Delta Ducon Engenharia in Brazil, encrypted networks and exfiltrated confidential data, and may release or sell the information unless a ransom is paid. The claim is unconfirmed.
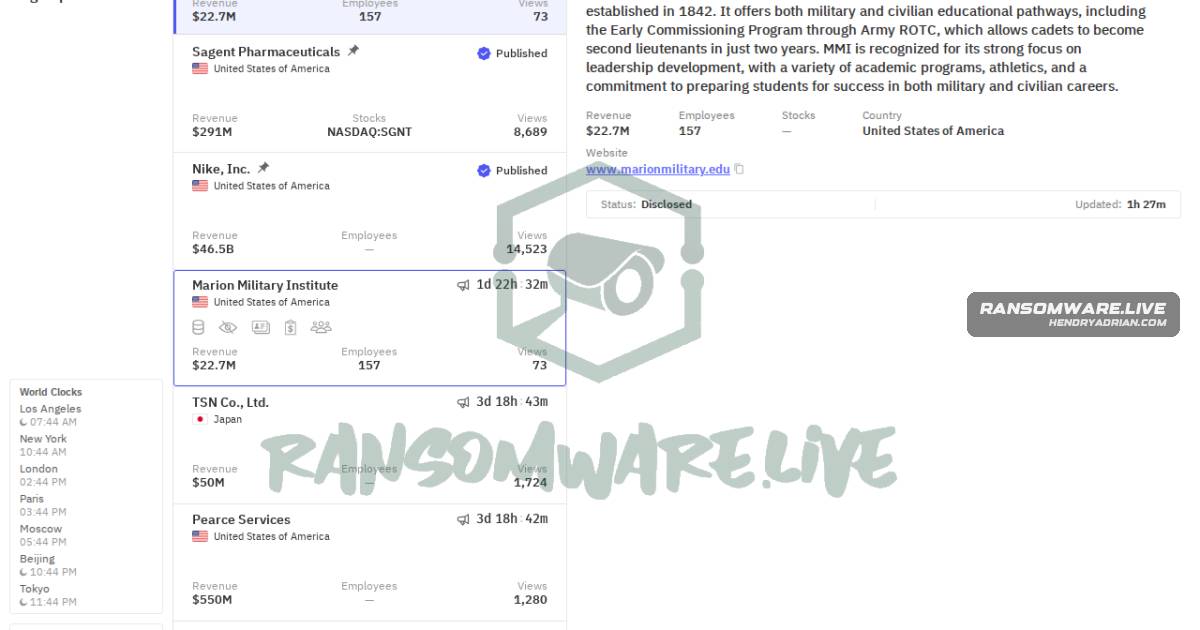
WorldLeaks claims it encrypted critical systems and exfiltrated sensitive data at Marion Military Institute, threatening a ransom demand and possible public release. The claim is unconfirmed.
A ransomware.live monitoring post attributes an unconfirmed ransomware and extortion claim against Mantra Softech Pvt. to Osiris. The post says systems were compromised and operations disrupted, but provides no independent confirmation.
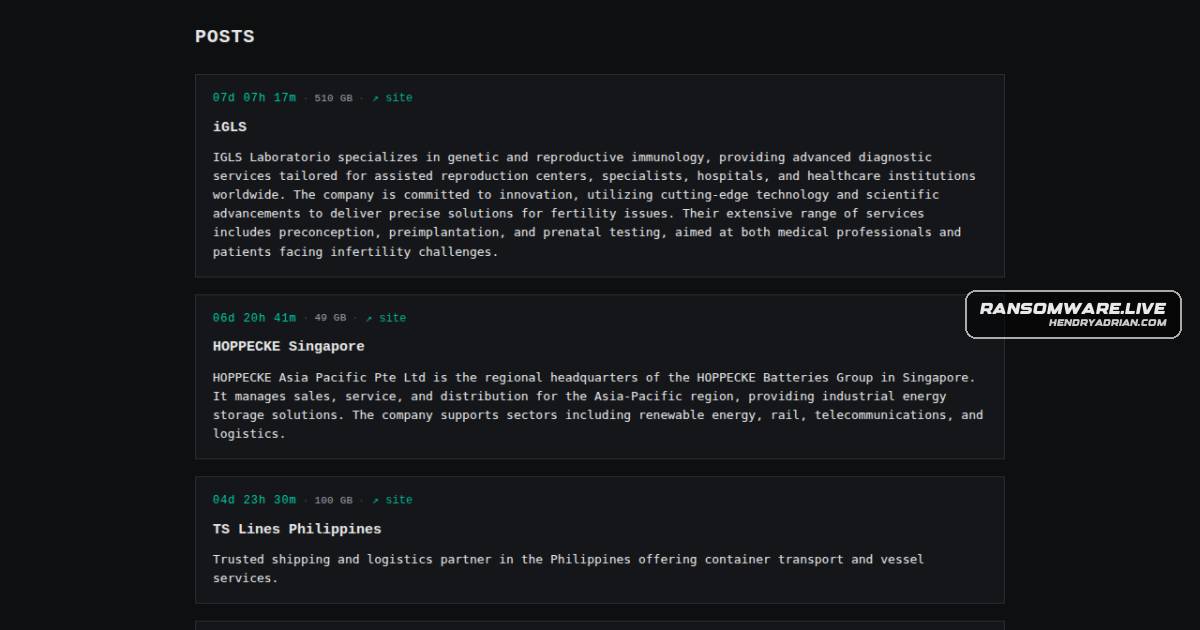
A ransomware.live-monitored post attributes an unconfirmed ransomware claim against iGLS Laboratorio in Spain to Payload. The post alleges disruption to the lab’s diagnostic services; the article says the claim has not been confirmed.
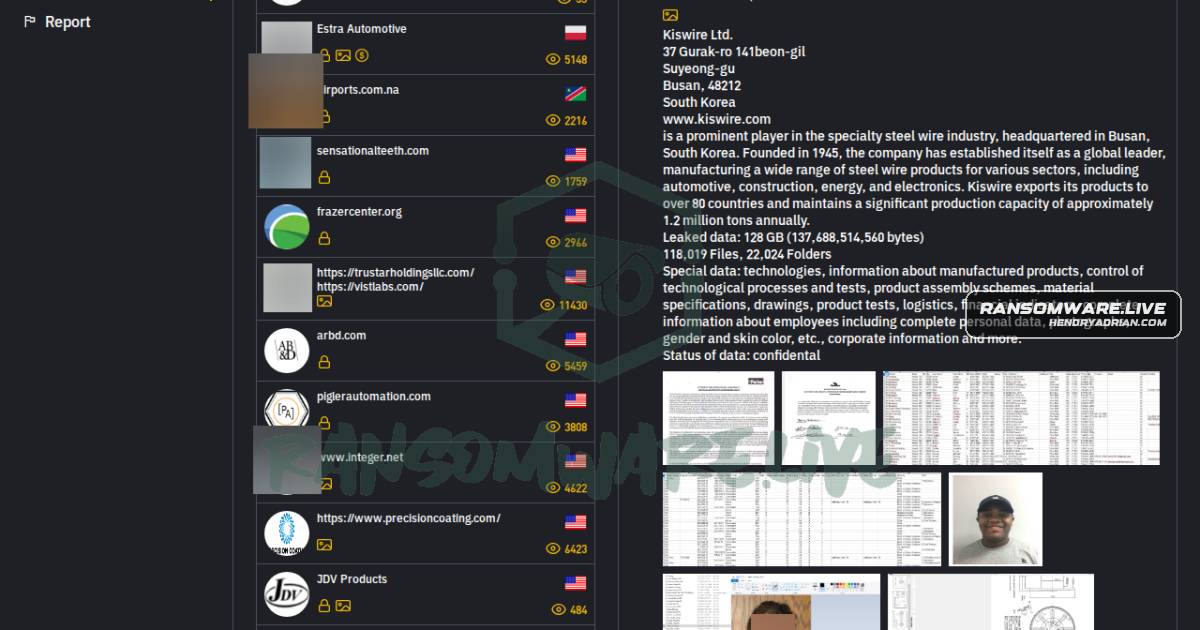
Incransom claims it exfiltrated 128 GB from South Korean manufacturer Kiswire, including corporate information and employee records. The monitoring post says the claim is unconfirmed.
Akira claims it will upload 17 GB of Rioja Motor data, allegedly including employee IDs and medical information, client documents, financial records, and project correspondence. The claim is unconfirmed.