
Play Ransomware Claim Names Roxiticus Golf Club
Summary
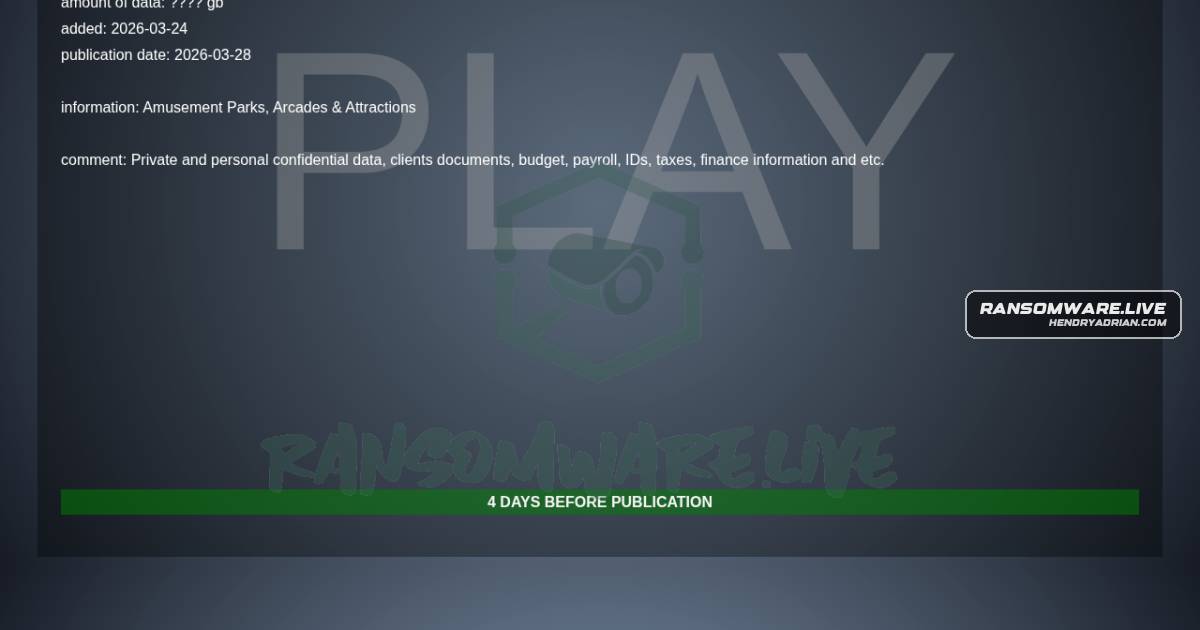
Ransomware.live lists Roxiticus Golf Club in the US as a target of the Play ransomware group. The claim is attributed to the group and remains unverified.
Key points
- The record names Roxiticus Golf Club as the victim and Play as the ransomware actor.
- The post attributes the claim to the ransomware group; it says the information could not be confirmed.
- The record lists the club's sector as hospitality and tourism and its country as the US.
- The claim was listed as published and discovered on March 24, 2026.
Article Details
- Victim
- Roxiticus Golf Club (reported target; incident unconfirmed)
- Encryption Status
- Not disclosed
- Exfiltration Status
- Not disclosed
- Ransom Demand
- Not disclosed
- Leak Status
- Not disclosed