
WorldLeaks Claims Marion Military Institute Ransomware Attack
Summary
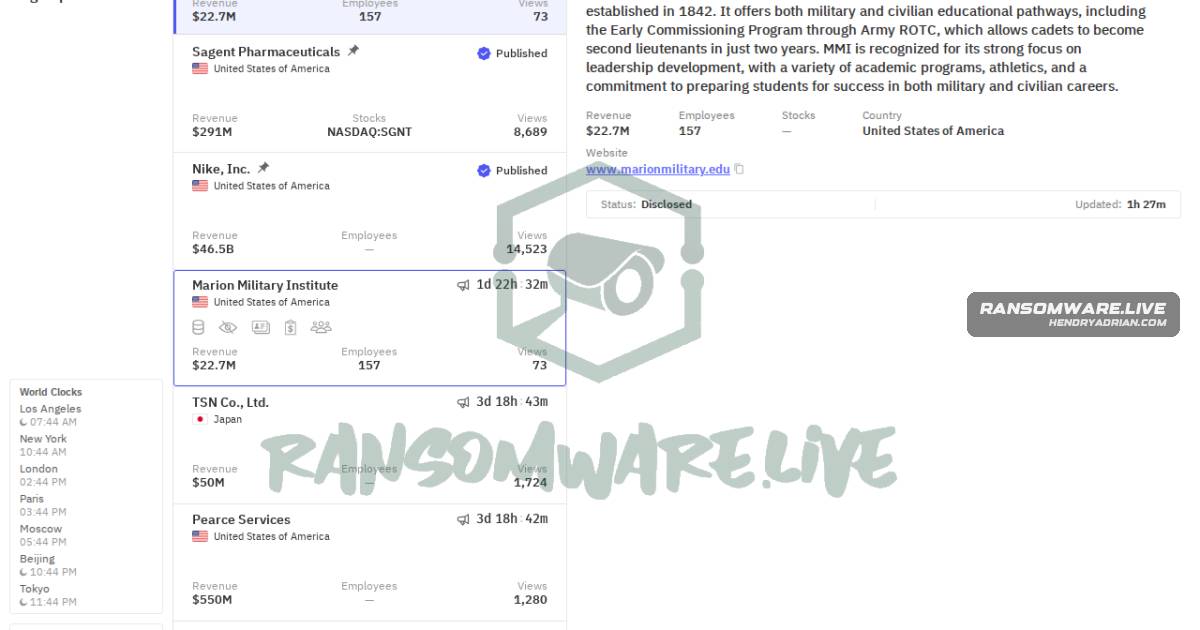
WorldLeaks claims it encrypted critical systems and exfiltrated sensitive data at Marion Military Institute, threatening a ransom demand and possible public release. The claim is unconfirmed.
Key points
- WorldLeaks claims Marion Military Institute in Marion, Alabama, was targeted.
- The group claims it encrypted critical systems and exfiltrated sensitive data; these claims are unconfirmed.
- WorldLeaks threatens a ransom demand and possible public release of the data if the institute does not comply.
- The record attributes the claim to the group’s leak site and says it was monitored by ransomware[.]live.
Article Details
- Victim
- Marion Military Institute
- Claim Date
- 2026-03-23
- Encryption Status
- WorldLeaks claims it encrypted critical systems; the claim is unconfirmed.
- Exfiltration Status
- WorldLeaks claims it exfiltrated data; the claim is unconfirmed.
- Exfiltrated Data
- Sensitive data, according to the group; specific data is not disclosed and the claim is unconfirmed.
- Ransom Demand
- The group reportedly threatens a ransom demand if the victim does not comply; no amount or confirmed demand is disclosed.
- Leak Status
- WorldLeaks threatens potential public release if the victim does not comply; no release is reported.