cyber.hendryadrian.com
Login
Navigation
HomeDashboardCyber Reports

Research

Threat ResearchVulnerability & ExploitDetection & DefenseSecurity Report

News

Security NewsCyber Attack & Data BreachRansom MonitorSecurity InsightsYouTube
Sources & Credits

Entities

CVEMalwarePeopleThreat ActorsMITRE ATT&CKVendorsProductsSecurity ToolsCountriesIndustries

Security Insights

Curated cybersecurity insights, opinions, emerging technologies, AI security topics, and notable industry discussions.

1296 articles

Security Insights · huntress.com

Seven Security Awareness Training Pitfalls to Avoid

The article outlines seven security awareness training pitfalls, including infrequent or forgettable lessons, punitive phishing simulations, compliance-only programs, outdated threat content, and burdensome administration.
Mar 21, 2024
Security Insights · threatfabric.com

Behavioral Biometrics Could Strengthen Authentication as Biometric Spoofing Advances

ThreatFabric discusses Android banking trojans that reportedly downgrade biometric checks to PINs and explains how behavioral biometrics could provide passive authentication, while noting risks such as false positives.

Mar 21, 2024
Security Insights · darkowl.com

SCATTERED SPIDER Uses Social Engineering and SIM Swaps to Target Organizations

A DarkOwl overview describes SCATTERED SPIDER’s reported phishing, helpdesk impersonation, SIM swapping and credential theft, along with its tools, malware and high-profile targets. It recommends training helpdesk staff on vishing, smishing and OTP attacks.

Mar 19, 2024
Security Insights · huntress.com

How macOS TCC Tracks App Permissions—and How MDM Overrides Can Grant Excessive Access

An explainer of macOS TCC covers how tccd and its database track app permissions, and warns that MDMOverrides.plist can grant broad access, such as full disk access for bash, without a clear reflection in the UI.

Mar 11, 2024
Security Insights · darkowl.com

How Darknet Data Can Expand OSINT Investigations

A DarkOwl webinar explains how analysts can combine darknet and surface-web sources for OSINT, with examples involving threat actors, leaked data, cryptocurrency, and conflict-related activity.

Mar 6, 2024
Security Insights · wiz.io

What DORA Requires of Financial Firms’ Cloud Security

An overview of DORA’s ICT-risk requirements for financial organizations, including cloud risk assessments, security provisions in provider contracts, ongoing monitoring, and potential CNAPP support.

Feb 26, 2024
Security Insights · team-cymru.com

How CTEM Helps Organizations Continuously Manage Threat Exposure

The article explains CTEM as a business-focused approach to managing exposure through scoping, discovery, prioritization, validation and mobilization, with practical steps for each stage.

Feb 22, 2024
Security Insights · wiz.io

How Chia Mining Can Enable Cloud Storage Cryptojacking

The article explains why Chia’s proof-of-storage model may appeal to cryptojackers and how large cloud storage usage can evade some common monitoring. It outlines cost, logging and detection considerations for defenders.

Feb 21, 2024
Security Insights · huntress.com

Healthcare Cybersecurity Risks and Practical Steps for Smaller Organizations

The article outlines healthcare cyber risks, forthcoming HHS cybersecurity standards and support, and steps smaller organizations can take, including endpoint protection, email security, and staff awareness training.

Feb 15, 2024
Security Insights · blog.talosintelligence.com

How Attackers Use QR Codes in Phishing Emails to Steal Credentials and Deliver Malware

Attackers use QR codes in phishing emails to direct victims to credential-stealing pages or malware on personal mobile devices, where enterprise protections may be weaker. Talos recommends mobile security, QR-code URL inspection, user education, and MFA.

Feb 14, 2024
Security Insights · huntress.com

How Attackers Abuse Remote Management Tools for Access and Persistence

A Huntress webinar recap explains how attackers misuse RMM tools for remote access and persistence, discusses challenges in detecting abuse, and demonstrates silently installing AnyDesk from a Sliver beacon.

Feb 6, 2024
Security Insights · hunt.io

Overview Highlights State-Linked Cyber Threat Groups, Targets and Tools

A high-level overview profiles eight state-linked threat groups, outlining their suspected origins, motivations, target sectors, and reported malware and tactics, including espionage, phishing, credential theft, and surveillance.

Feb 6, 2024
Security Insights · hunt.io

Hunt.io Walkthrough Finds a Phishing Site Hosting XWorm RAT

A hunting walkthrough examines an open directory containing a cryptocurrency phishing site and XWorm RAT, showing how its files attempt to steal credentials and recovery phrases and how scripts download and execute additional files.

Feb 1, 2024
Security Insights · darkowl.com

Webinar Reviews Iran’s Cyber Operations, Malware and Front Companies

A webinar transcript surveys Iran’s cyber program, including state-linked groups, malware, ransomware, front companies and cryptocurrency. The speaker discusses the difficulty of attributing operations specifically to the MOIS or IRGC.

Jan 30, 2024
Security Insights · darkowl.com

DarkOwl Forecasts Ransomware, Credential Theft and Other Threats to Persist in 2024

DarkOwl analysts review 2023 cyber threats and forecast continued ransomware, credential theft, dark web activity, messaging-app use and malicious adoption of AI in 2024.

Jan 18, 2024
Security Insights · wiz.io

Wiz Recaps Its 2023 Cloud Security Stories and Key Lessons

Wiz revisits selected 2023 stories on cloud vulnerabilities, supply-chain attacks, ransomware, Microsoft’s stolen signing key and AI data poisoning, highlighting lessons about credential security, data hygiene and training-data integrity.

Jan 16, 2024
Security Insights · huntress.com

How Apple's TCC Framework Controls App Access to Sensitive macOS Data

An overview of macOS TCC explains how it records app permissions for sensitive data, where its databases reside, and why managing permissions across business devices can add complexity.

Jan 16, 2024
Security Insights · wiz.io

Ten AI Security Reads Cover LLM Risks, Safeguards, and Security Uses

A curated list of 10 articles explores AI security, including LLM vulnerabilities, safeguards, insecure machine-learning code, policy, AI-assisted fuzzing, and malicious uses of chatbots.

Jan 5, 2024
Security Insights · wiz.io

Four Questions to Guide Security Teams Evaluating AI-SPM Tools

The article outlines four questions for assessing AI security: visibility into AI components, identifying risks, prioritizing them, and detecting pipeline misuse. It also promotes Wiz’s AI-SPM capabilities.

Jan 2, 2024
Security Insights · darkowl.com

DarkOwl Outlines Darknet Fraud Trends, From Account Takeovers to Healthcare Fraud

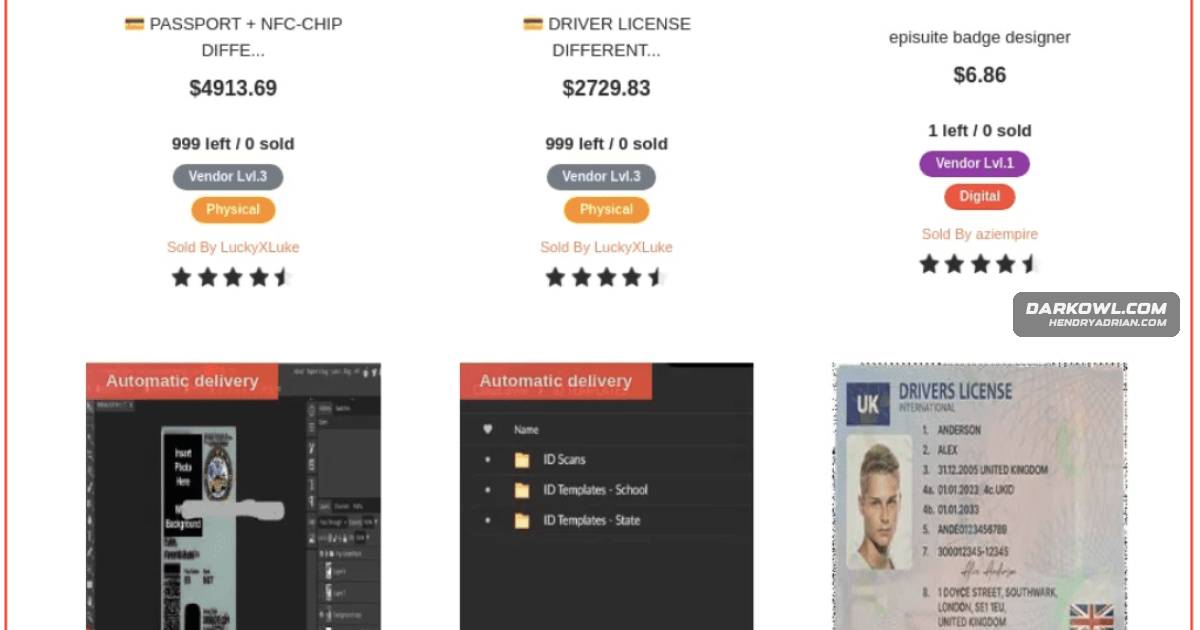
DarkOwl describes darknet fraud involving refund services, stolen accounts, gift cards, personal and financial data, counterfeit documents, and healthcare information, and recommends password managers and avoiding password reuse.

Dec 19, 2023
Security Insights · team-cymru.com

Using NIST CSF 2.0 to Strengthen Supply Chain Risk Management

The vendor blog explains how organizations can apply NIST CSF 2.0 to supply-chain security, including continuous asset discovery, risk scoring that combines vulnerability severity with business context, partner benchmarking, and real-time threat intelligence.

Dec 15, 2023
Security Insights · huntress.com

How Small Businesses Can Make Cyber Threat Intelligence More Useful

The article explains how small and midsize businesses can focus cyber threat intelligence on their decisions, balance the cost of formal requirements development, and assess external providers for relevant, actionable insights.

Dec 12, 2023
Security Insights · huntress.com

Why Indicators Still Matter for Small-Business Cyber Defense

The article explains that indicators are limited without context, but high-confidence indicators can still provide SMBs and MSPs with a practical, low-cost layer of defense alongside other security controls.

Dec 7, 2023
Security Insights · darkowl.com

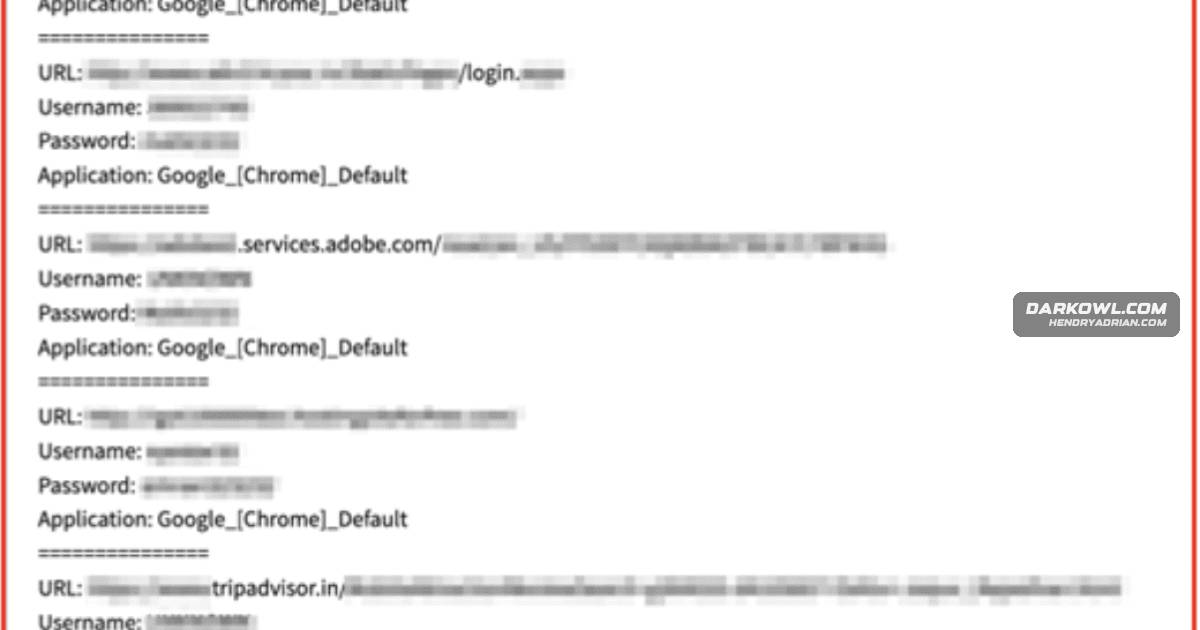
What Stealer Logs Contain and How Cybercriminals Use Them

Stealer logs collect recent data from infected devices, including credentials, cookies, browser autofill, and device details. Criminals can use the information for account takeover, identity theft, and fraud.

Dec 6, 2023
PreviousPage 48 of 54 Next
© 2026 cyber.hendryadrian.com