
What Stealer Logs Contain and How Cybercriminals Use Them
Summary
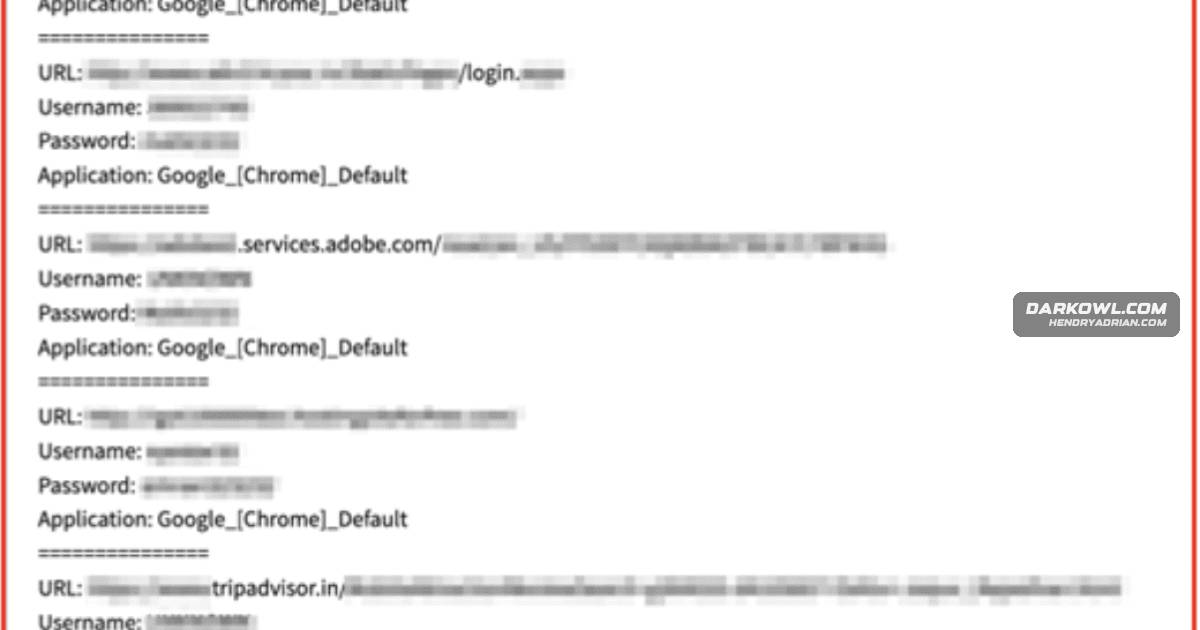
Stealer logs collect recent data from infected devices, including credentials, cookies, browser autofill, and device details. Criminals can use the information for account takeover, identity theft, and fraud.
Key points
- Infostealers are commonly spread through phishing, malicious attachments, fake websites, and fraudulent software or apps.
- Stolen logs may include passwords, cookies, browsing data, autofill details, financial information, and device identifiers.
- Criminals can use stolen session cookies to access accounts without the victim’s username and password.
- The article says stealer logs may contain more current credentials than older data from leaks or breaches.
- Logs may also reveal installed software, browsers, and device information that can support profiling or social engineering.
- The article describes stealer logs as data observed on darknet markets and discusses their potential for identity theft, financial crime, and account takeover.
Article Details
- Topic
- Stealer logs and the sensitive data infostealer malware collects, exfiltrates, and enables criminals to misuse