cyber.hendryadrian.com
Login
Navigation
HomeDashboardCyber Reports

Research

Threat ResearchVulnerability & ExploitDetection & DefenseSecurity Report

News

Security NewsCyber Attack & Data BreachRansom MonitorSecurity InsightsYouTube
Sources & Credits

Entities

CVEMalwarePeopleThreat ActorsMITRE ATT&CKVendorsProductsSecurity ToolsCountriesIndustries

Security Insights

Curated cybersecurity insights, opinions, emerging technologies, AI security topics, and notable industry discussions.

1296 articles

Security Insights · darktrace.com

How to Reduce Data Exposure Risks in Amazon Bedrock Deployments

Broad IAM roles and limited visibility can expose sensitive data through Bedrock agents. Darktrace describes how its cloud security product maps configurations and access, flags misconfigurations, and monitors for unusual behavior.
Nov 19, 2025
Security Insights · darkowl.com

How to Avoid Black Friday Shopping, Phishing and Delivery Scams

The article outlines fake retail sites, phishing offers, delivery-text scams and fraudulent charity appeals, with advice to verify links and organizations, use trusted payment methods and contact companies directly.

Nov 18, 2025
Security Insights · huntress.com

Nine Layers to Consider in a Modern Cybersecurity Stack

A practical overview of nine cybersecurity stack layers, from security hygiene and identity protection to monitoring, recovery, and governance, with suggested controls for each.

Nov 17, 2025
Security Insights · darkowl.com

What Indicators of Attack Are and How Darknet Intelligence Can Reveal Them

Indicators of attack (IoAs) are behaviors that can signal an attack in progress or about to occur. The article describes darknet examples and how credential-exposure signals preceded three reported incidents.

Nov 13, 2025
Security Insights · threatfabric.com

Five Fraud Trends from 2025—and What to Expect in 2026

ThreatFabric reviews investment scams, NFC relay fraud, biometric data theft, criminal AI and intelligence-sharing in 2025, with predictions for 2026 and implications for financial institutions.

Nov 12, 2025
Security Insights · darkowl.com

What Discord Users Should Know About Scams, Malware, and Online Safety

An overview of Discord’s risks, including scam links, malware, harmful content, and harassment, with tips such as enabling 2FA, limiting messages, and avoiding unfamiliar links or files.

Nov 11, 2025
Security Insights · huntress.com

MFA for Businesses: Benefits, Bypass Risks, and Implementation Options

A business-focused guide explains MFA’s security benefits, adoption challenges, common bypass methods, and options ranging from SMS codes to hardware tokens. It also describes incidents observed by Huntress analysts.

Nov 7, 2025
Security Insights · huntress.com

Huntress CTF 2025 Retrospective Highlights Malware Analysis and Forensics Challenges

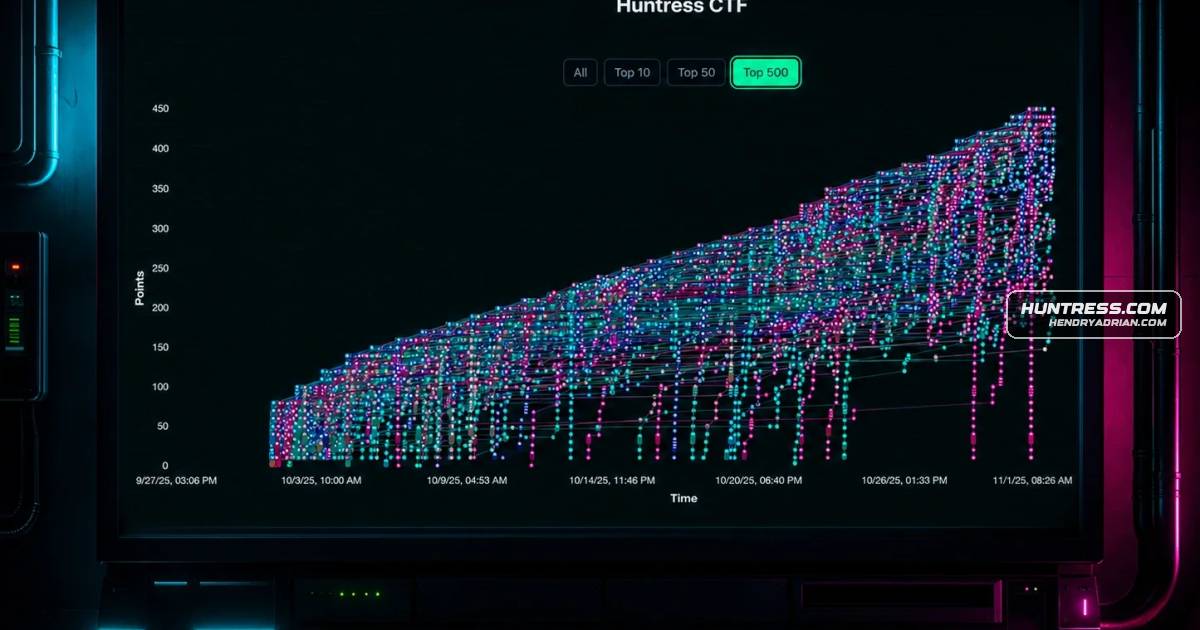
Huntress recaps its month-long 2025 CTF, featuring challenges in malware analysis, forensics, and threat hunting. The event drew 11,898 registered users; organizers also describe an early platform outage and antivirus alerts when some players analyzed malware outside V

Nov 6, 2025
Security Insights · darktrace.com

Darktrace Says Microsoft 365 API Plus Journaling Can Reduce Email Threat-Detection Delays

Darktrace says its API-plus-journaling integration for Microsoft 365 receives messages faster than API-only ingestion, reporting lower median and average latency in customer deployments and recommending the approach for organizations that can use journaling.

Nov 4, 2025
Security Insights · darkowl.com

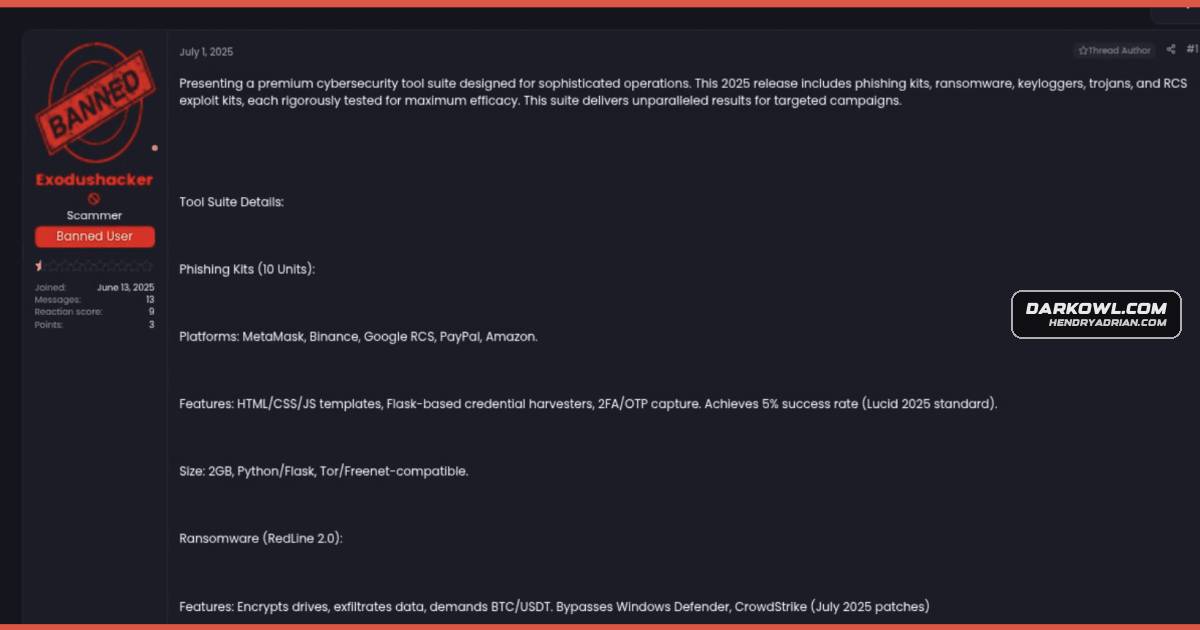
How Dark-Web Toolkits and AI Are Scaling Phishing and Social Engineering

The article explains how phishing kits, stolen data, and AI-assisted services help scale social-engineering attacks, outlines a typical attack chain, and recommends practical protections for organizations and individuals.

Oct 31, 2025
Security Insights · wiz.io

Wiz Proposes Policy and Technology Measures to Secure Cloud-Connected Critical Infrastructure

Wiz argues that cloud adoption changes critical-infrastructure risks and calls for adaptive regulations, continuous visibility, modernization funding, threat-information sharing, and coordinated government action.

Oct 30, 2025
Security Insights · wiz.io

CISOs’ 2026 Security Budget Priorities: Measure Risk Reduction and Simplify Spending

Wiz’s benchmark-based guidance urges CISOs to tie 2026 security budgets to measurable risk reduction, simplify cloud and tool environments, develop staff, and prioritize AI investments by expected outcomes.

Oct 29, 2025
Security Insights · darkowl.com

DarkOwl Maps Its Darknet Intelligence Coverage to MITRE ATT&CK Techniques

DarkOwl describes how its darknet monitoring can surface exposed credentials, account and token risks, infrastructure information, and leaked data across selected MITRE ATT&CK techniques.

Oct 28, 2025
Security Insights · deepweb.net

How to Access Tor on a Smartphone: VPN Setup, Browser Choices and iOS Traffic Leaks

A guide to accessing Tor on Android and iOS covers VPN safeguards, recommended browser apps, and iOS traffic that may bypass Tor, including media requests, WebRTC, and OCSP checks.

Oct 22, 2025
Security Insights · darkowl.com

How C2 Frameworks Hide Post-Exploitation Activity in Plain Sight

C2 frameworks help operators control compromised systems and conceal activity. The article describes tactics including Telegram communications, compromised trusted servers, and Discord-hosted payloads, and urges defenders to adapt monitoring.

Oct 21, 2025
Security Insights · darkowl.com

Webinar Explores AI Use in Investigations and Threat Actor Operations

A webinar discusses how investigators use AI and how threat actors apply it to phishing, fraud, deepfakes, and propaganda. Speakers stress human oversight, layered verification, and preparation for impersonation.

Oct 14, 2025
Security Insights · huntress.com

Eight Everyday Security Habits That Put Organizations at Risk—and What to Do Instead

A cybersecurity-awareness guide explains how reused passwords, phishing clicks, shared credentials, unapproved software, public Wi-Fi, delayed updates, local data storage and oversharing can expose organizations, and offers safer alternatives.

Oct 14, 2025
Security Insights · deepweb.net

Why Tails Is Often Chosen for Privacy and Security

The article explains Tails’ appeal for privacy and security, highlighting its live USB operation, optional encrypted persistent storage, bundled security tools, and comparatively simple design. It cautions that Tails does not replace user responsibility.

Oct 13, 2025
Security Insights · darkowl.com

What DDoS Attacks Are, How They Work, and How to Prepare

An explainer describes DDoS attacks, their use of botnets and common motives, examples affecting gaming, UK councils, X and BreachForums, and basic preparation measures such as response plans, network monitoring and capacity planning.

Oct 9, 2025
Security Insights · deepinstinct.com

Webinar Demonstrates Guardrail-Free LLM Creating Malware That Evaded 65 of 73 Legacy Security Tools

A promoted webinar demonstrates malware creation with a guardrail-free LLM and describes evasion techniques, DIANNA's analysis, and the vendor's claim that deep-learning prevention can catch malware missed by legacy tools.

Oct 8, 2025
Security Insights · huntress.com

Huntress Recommends Practical Alternatives to Common Cybersecurity Advice

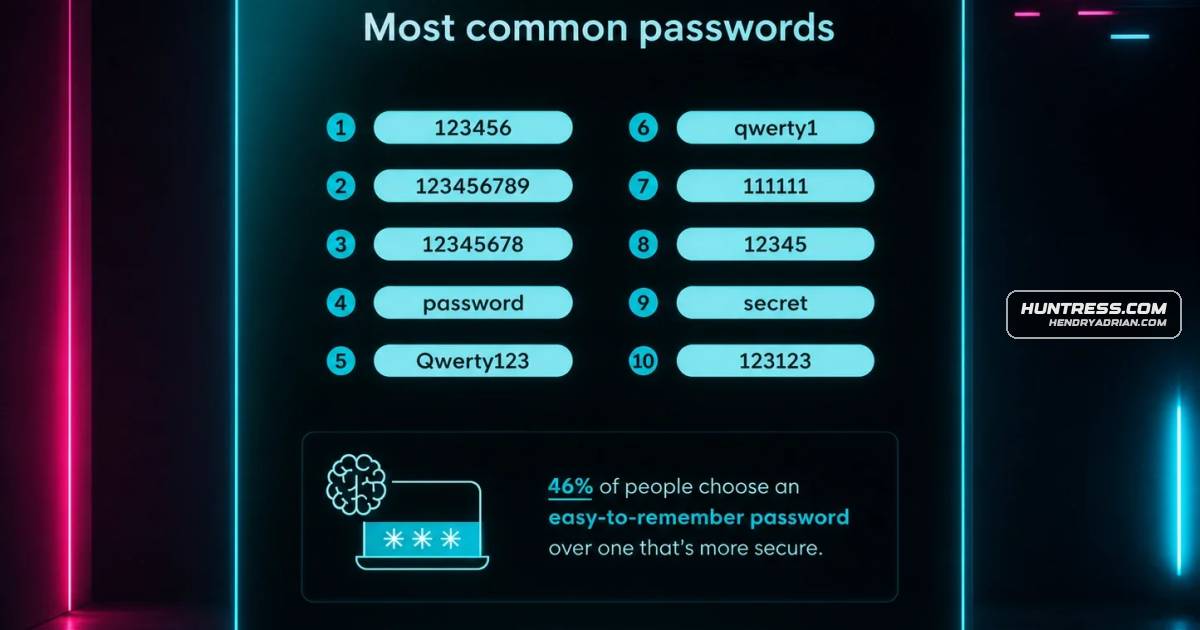
Huntress argues that vague security advice is ineffective and recommends practical measures such as password managers, independent verification of unexpected messages, automatic updates, stronger MFA, and technical controls that reduce reliance on user vigilance.

Oct 7, 2025
Security Insights · deepweb.net

How One-Time Notes Protect Secret Messages—and What Users Must Trust

An explainer on disposable notes describes unique links, HTTPS, and the limits of verifying a service’s security claims, including why open-source code can help users assess how a service works.

Oct 3, 2025
Security Insights · wiz.io

AI Security 101: Mapping the AI Attack Surface

An overview of AI security risks across data, models, pipelines, APIs and shadow AI, with practical steps for reducing exposure and examples of incidents Wiz says it uncovered or observed.

Oct 2, 2025
Security Insights · huntress.com

How Managed EDR Investigations Use Telemetry to Clarify Threats

Huntress explains how analysts use endpoint telemetry and forensic artifacts to trace attack origins, assess scope, and uncover related intrusions, with examples involving a tech-support scam, Akira ransomware, and activity linked to RedCurl TTPs.

Sep 22, 2025
PreviousPage 41 of 54 Next
© 2026 cyber.hendryadrian.com