How C2 Frameworks Hide Post-Exploitation Activity in Plain Sight
Summary
C2 frameworks help operators control compromised systems and conceal activity. The article describes tactics including Telegram communications, compromised trusted servers, and Discord-hosted payloads, and urges defenders to adapt monitoring.
Key points
- C2 frameworks let operators manage compromised systems and support capabilities such as persistence, privilege escalation, network pivoting, and data exfiltration.
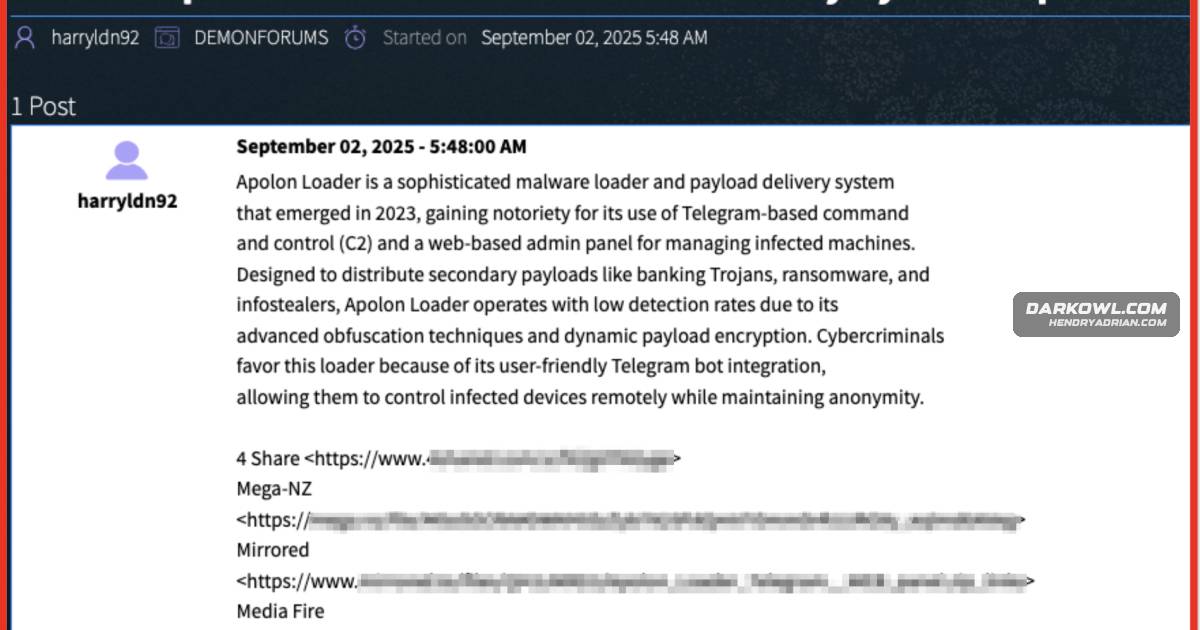
- Attackers may use Telegram bot traffic over HTTPS to make C2 communications appear benign.
- In the 2021 Outer Space operation, the suspected Iranian-backed Oil Rig group reportedly repurposed a compromised Israeli HR server as C2 infrastructure.
- The article says the Saint Bear group used Discord's content delivery network to host malicious files.
- Defenders should monitor for suspicious activity within otherwise trusted services and tune endpoint detection to recognize malicious traffic.
Article Details
- Topic
- Stealth and concealment techniques used by command-and-control frameworks and threat actors, including compromised infrastructure and trusted platforms for C2 communications and payload hosting.
Threat Actors
Malware
Products
Cobalt StrikeCobalt Strike is often regarded as the industry leader for production-grade post-exploitation operations due to its broad set of easy-to-use features, making engagements accessible even to less technically skilledCovenantOpen-source options are also widely available, with frameworks like Covenant, Sliver, Metasploit, and many others freely downloadable from GitHub.DarkOwl VisionDarkOwl Vision: Threat Intelligence on C2 DiscordSaint Bear, a Russian threat actor active against Ukraine and Georgia as early as 2021, frequently used Discord’s content delivery network for hosting malicious files.Metasploit FrameworkOpen-source options are also widely available, with frameworks like Covenant, Sliver, Metasploit, and many others freely downloadable from GitHub.SliverOpen-source options are also widely available, with frameworks like Covenant, Sliver, Metasploit, and many others freely downloadable from GitHub.Telegram“Small Sieve,” for example, uses the Telegram bot API to communicate over HTTPS and relay commands to and from malicious C2 servers.
Countries
GeorgiaSaint Bear, a Russian threat actor active against Ukraine and Georgia as early as 2021, frequently used Discord’s content delivery network for hosting malicious files.UkraineSaint Bear, a Russian threat actor active against Ukraine and Georgia as early as 2021, frequently used Discord’s content delivery network for hosting malicious files.