cyber.hendryadrian.com
Login
Navigation
HomeDashboardCyber Reports

Research

Threat ResearchVulnerability & ExploitDetection & DefenseSecurity Report

News

Security NewsCyber Attack & Data BreachRansom MonitorSecurity InsightsYouTube
Sources & Credits

Entities

CVEMalwarePeopleThreat ActorsMITRE ATT&CKVendorsProductsSecurity ToolsCountriesIndustries

Cyber Attack & Data Breach

Tracks cyberattacks, data breaches, compromised organizations, leaked data, and other security incidents

2317 articles

Cyber Attack & Data Breach · cloudsek.com

Exposed Bank Backup File Revealed Customer Data, Credentials and Cryptographic Keys

A security assessment found a publicly accessible backup file containing bank customer data, credentials, authentication tokens, cryptographic keys, logs and decompiled source code. The article recommends securing backups and rotating exposed credentials.
Apr 11, 2025
Cyber Attack & Data Breach · cloudsek.com

Exposed Apache Superset Dashboard Put $110M in Loan Data at Risk

An unauthenticated Apache Superset dashboard at a financial institution’s vendor exposed sensitive lending data, including records for over 2.6 million allocated accounts and $110 million in outstanding loans.

Apr 10, 2025
Cyber Attack & Data Breach · darktrace.com

Email Bombing and Fake IT Calls Lead to Credential Theft and Network Reconnaissance

Darktrace reports that email bombing and fake Microsoft Teams calls led a customer employee to disclose credentials via Quick Assist. The attacker then performed network reconnaissance and attempted SMB/NTLM access; security teams intervened.

Apr 10, 2025
Cyber Attack & Data Breach · cloudsek.com

Exposed Jenkins Instance Enabled Access to Servers, Credentials, and Production Data

CloudSEK reported that an unauthenticated Jenkins instance exposed multiple servers, credentials, and a production database containing customer and employee PII. The organization isolated servers, revoked exposed credentials, and strengthened access controls.

Mar 28, 2025
Cyber Attack & Data Breach · cloudsek.com

CloudSEK Says Exposed Supplier Credentials Put Banking Systems and Customer Data at Risk

CloudSEK says exposed supplier credentials enabled access to a communications portal, 32 cloud accounts, call recordings and transcripts, and tools to message over 50,000 users. The company reports that its discovery enabled mitigation.

Mar 27, 2025
Cyber Attack & Data Breach · cloudsek.com

CloudSEK Presents Evidence Supporting Alleged Oracle Cloud Breach After Oracle Denial

CloudSEK says a 10,000-line sample and other evidence support claims that Oracle Cloud customer data was stolen, affecting 1,500+ organizations. Oracle denied a breach; CloudSEK recommends credential rotation and investigation.

Mar 24, 2025
Cyber Attack & Data Breach · wiz.io

Compromised GitHub Action Exposed Secrets in Public Repository Logs

A compromised tj-actions/changed-files action ran malicious code in affected workflows, exposing secrets in logs. Wiz identified dozens of impacted public repositories; maintainers reverted the malicious commits, but exposed credentials may still require rotation.

Mar 15, 2025
Cyber Attack & Data Breach · wiz.io

Wiz Finds Exposed DeepSeek Database Containing Chat History and Secrets

Wiz found an unauthenticated DeepSeek ClickHouse database exposing over a million log entries, including chat history and secrets. Wiz disclosed the exposure, and DeepSeek secured it.

Jan 29, 2025
Cyber Attack & Data Breach · group-ib.com

Reich 5 Android Malware Gang Stole $930,000 Before Members Were Arrested

The Reich 5 gang used Svpeng Android malware to steal banking credentials and intercept SMS codes, taking more than 50 million rubles from over 30,000 bank clients before Russian authorities arrested four members in 2015.

Jan 7, 2025
Cyber Attack & Data Breach · wiz.io

Compromised lottie-player Versions Injected Malicious Crypto Wallet Prompts

Attackers reportedly used a maintainer’s stolen token to inject malicious code into lottie-player 2.0.5–2.0.7, prompting wallet connections on affected sites. The versions were removed; sites should update to 2.0.8 or revert to 2.0.4.

Oct 31, 2024
Cyber Attack & Data Breach · darktrace.com

Vishing Attack Compromises Hospitality Customer’s Network After Employee Approves MFA Prompt

A hospitality customer confirmed an attacker used caller-ID spoofing to trick a remote employee into approving MFA, then accessed the network through the VPN. Darktrace detected reconnaissance and attempted lateral movement and applied containment actions.

Oct 3, 2024
Cyber Attack & Data Breach · group-ib.com

PhishEye Banking Crew Stole More Than $320,000 from Russian Customers

Group-IB describes how the PhishEye group used banking Trojans, phishing pages, and phone scams to steal from thousands of Russian bank customers before its leaders and accomplices were arrested and sentenced.

May 16, 2024
Cyber Attack & Data Breach · darkowl.com

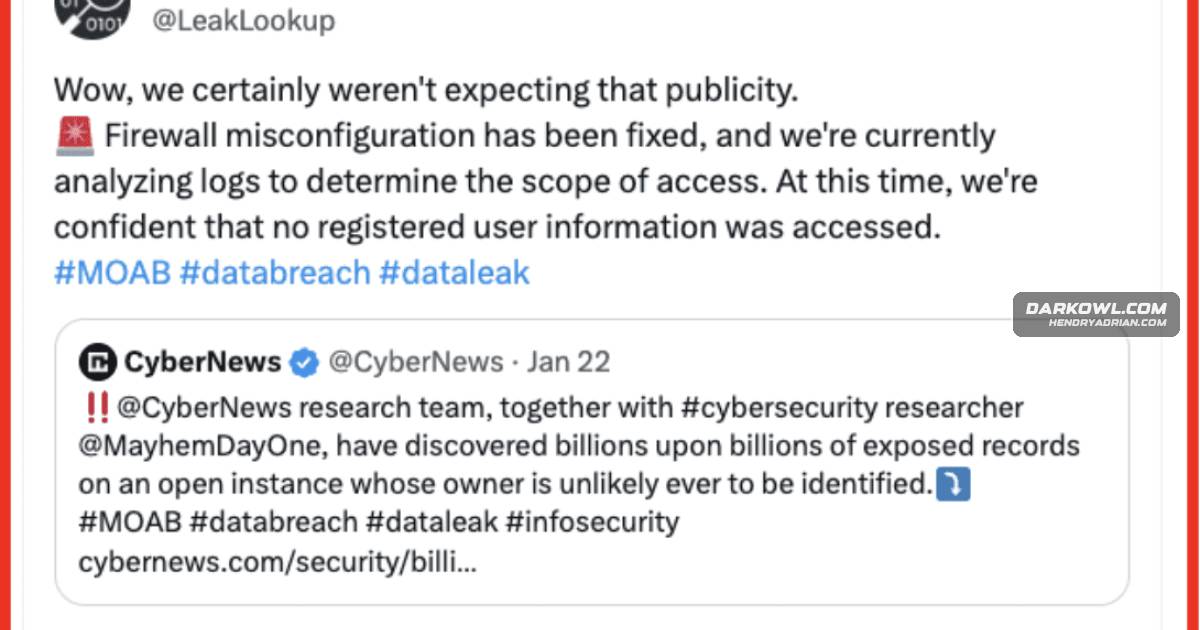
Leak-Lookup Misconfiguration Exposed Database Behind ‘Mother of All Breaches’

Leak-Lookup said a misconfigured server exposed its database of previously leaked records, prompting the “Mother of All Breaches” report. The company said it secured the server and that registered-user information did not appear compromised.

Feb 21, 2024
Cyber Attack & Data Breach · group-ib.com

CybSec Group Members Convicted Over DDoS Extortion Attacks on AnastasiaDate

AnastasiaDate suffered DDoS extortion attacks in 2015 and 2016. Group-IB and Qrator Labs helped identify two Ukrainian perpetrators, who pleaded guilty and received suspended sentences in 2018.

Jan 24, 2024
Cyber Attack & Data Breach · darkowl.com

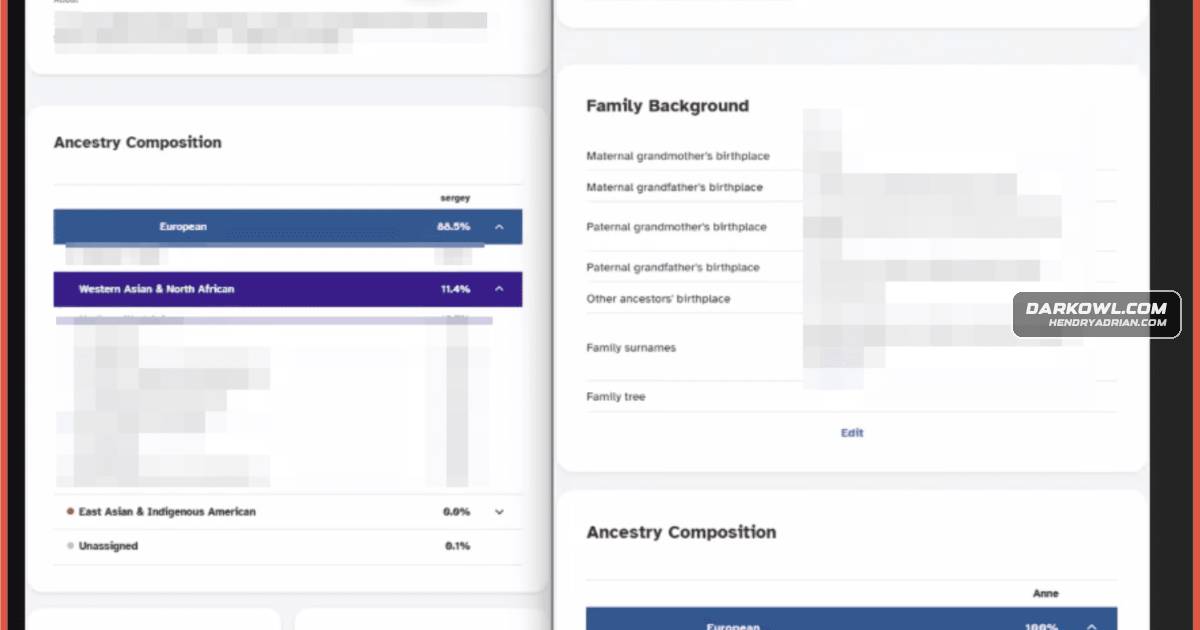
23andMe Genetic Data Allegedly Offered for Sale and Shared Online

Dark-web sellers and forum users claimed to offer and share 23andMe data, including personal and genetic details. 23andMe said the data was obtained through credential stuffing and reported no evidence of a breach of its IT systems.

Oct 20, 2023
Cyber Attack & Data Breach · wiz.io

Microsoft AI Research SAS Token Exposed 38TB of Private Data, Wiz Reports

Wiz says a Microsoft AI research SAS token exposed 38TB of private data, including workstation backups, credentials and Teams messages. Microsoft invalidated the token in June 2023.

Sep 18, 2023
Cyber Attack & Data Breach · huntress.com

Huntress Stops $103,000 BEC Scam After Vendor Email Accounts Are Compromised

Attackers used two compromised vendor email accounts to redirect a roughly $103,000 payment. Huntress stopped the transfer by calling to verify new bank details, and the vendor’s IT team investigated the compromise.

Aug 9, 2023
Cyber Attack & Data Breach · satsgroup.com

SATS ASA Investigates Signs of Broader IT Intrusion; Member Data Impact Unclear

SATS ASA says new indications may mean an earlier incident involving unauthorized access to part of its IT environment is more extensive than first assessed. The investigation continues; member-system involvement and data exposure have not been indicated.

Jul 20, 2023
Cyber Attack & Data Breach · huntress.com

One MSP’s Clients Hit by Three Microsoft 365 Compromises in 72 Hours

Huntress reported three Microsoft 365 compromises across one MSP’s clients in 72 hours, involving malicious inbox rules. In one case, an attacker abused administrative permissions to access multiple mailboxes.

Jun 27, 2023
Cyber Attack & Data Breach · stjames.wa.edu.au

St James’ Anglican School Reports Unauthorized Access and Personal Information Incident

St James’ Anglican School says unauthorized access to its systems involved personal information about members of its community. The school contained the incident, notified families and reported it to Australian authorities; its investigation is ongoing.

Apr 1, 2023
Cyber Attack & Data Breach · noticiassin.com

Ransom Home Demands $4.5 Million From Barcelona Hospital After Cyberattack

Catalan officials say Ransom Home demanded $4.5 million to prevent publication of information accessed in an attack on Hospital Clínic de Barcelona. The hospital will not pay; medical services were disrupted, with recovery underway.

Mar 10, 2023
Cyber Attack & Data Breach · huntress.com

Log4Shell Attackers Target VMware Horizon Servers, Huntress Reports

Huntress says attackers exploited Log4Shell to target VMware Horizon servers, affecting a Blue Tree Technology machine despite prior server patching. Its ThreatOps team identified malicious commands and helped partners remediate the threat that day.

Jun 28, 2022
Cyber Attack & Data Breach · huntress.com

Huntress Says Weak RDP Credentials Enabled Access to QA Environment

Huntress reported an unknown actor brute-forced an orphaned Windows QA VM using weak RDP credentials. The company said its investigation found no access to customer data or production systems and that it rebuilt the environment with security changes.

Nov 17, 2021
Cyber Attack & Data Breach · darkowl.com

REvil Says Its Tor Services Were Hijacked Using a Former Spokesperson’s Keys

A REvil spokesperson said the group’s Tor services were hijacked using keys held by former representative Unknown. The report describes the group’s disputed return and growing distrust among darknet forum users.

Oct 20, 2021
PreviousPage 96 of 97 Next
© 2026 cyber.hendryadrian.com