
REvil Says Its Tor Services Were Hijacked Using a Former Spokesperson’s Keys
Summary
A REvil spokesperson said the group’s Tor services were hijacked using keys held by former representative Unknown. The report describes the group’s disputed return and growing distrust among darknet forum users.
Key points
- REvil’s Happy Blog displayed a default nginx 404 page rather than simply failing to respond.
- Spokesperson 0_neday alleged that someone used former representative Unknown’s private Tor service keys to redirect the hidden service.
- The article does not independently verify the alleged hijacking or identify who carried it out.
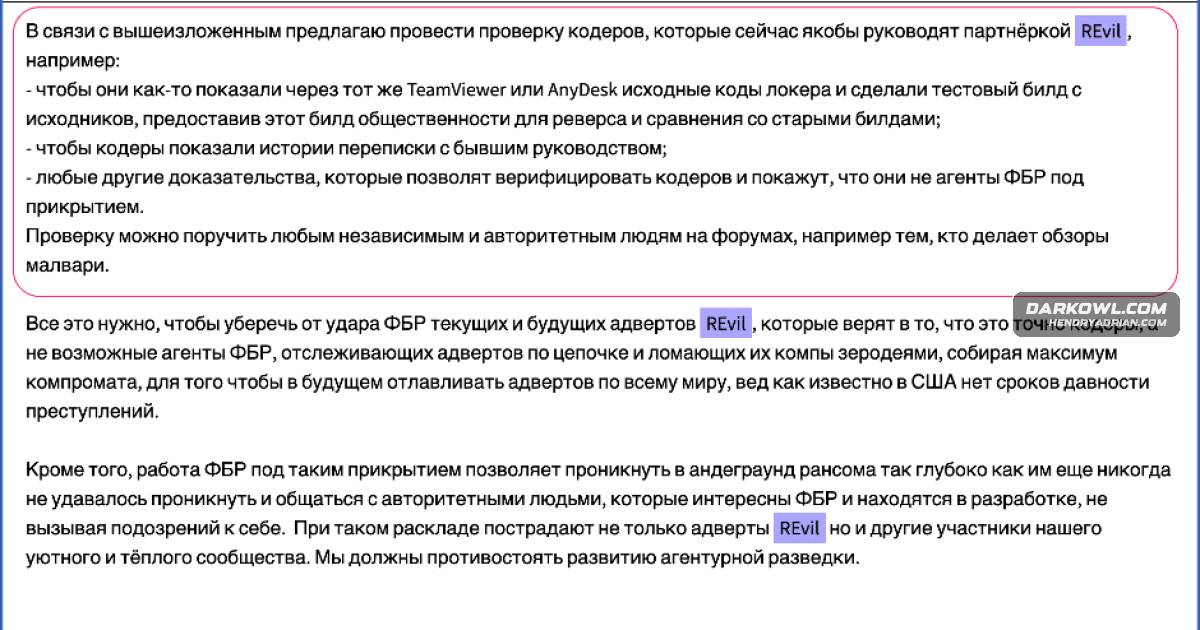
- After REvil’s services returned in September 2021, darknet users and rival ransomware representatives publicly questioned the group’s legitimacy and whether it had been compromised.
- The report recounts competing theories about REvil’s earlier shutdown, including law-enforcement action, voluntary closure, and an internal dispute.
- Darknet forum users also alleged that REvil had scammed affiliates through a cryptobackdoor; the article presents this as an unverified claim.
Article Details
- Victim Organization
- REvil
- Incident Type
- Alleged hijacking and compromise of REvil's Tor services using private keys associated with its former representative, Unknown/UNKN.
- Operational Impact
- REvil's Happy Blog displayed a default nginx 404 page instead of its usual content. A REvil representative alleged that the Tor service path had been changed and a different service raised; the article does not confirm who performed the change.
- Claim Status
- alleged