
Leak-Lookup Misconfiguration Exposed Database Behind ‘Mother of All Breaches’
Summary
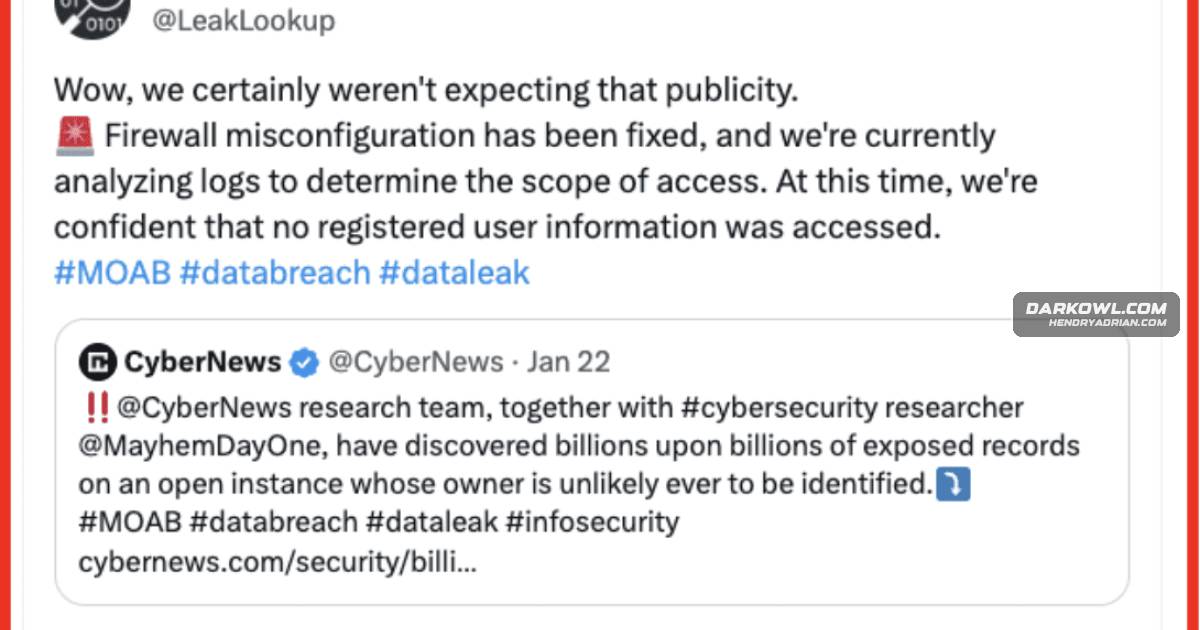
Leak-Lookup said a misconfigured server exposed its database of previously leaked records, prompting the “Mother of All Breaches” report. The company said it secured the server and that registered-user information did not appear compromised.
Key points
- Cybernews reported finding an open dataset containing 26 billion records and 12 TB of data, including records attributed to prior leaks.
- Leak-Lookup later claimed the exposure came from a misconfigured server that allowed IPv6 access to its “hot” cluster; it said access began around early December.
- The database contained leaks already publicly available, and DarkOwl assessed that it was unlikely to include substantial new data.
- Leak-Lookup said the exposed data did not appear to include compromised information belonging to its registered users.
- The server was secured, and DarkOwl reported no threat actor claiming access to the database during the exposure.
Article Details
- Victim Organization
- Leak-Lookup
- Incident Type
- Misconfigured server exposed a database of previously collected data leaks through IPv6 access.
- Disclosure Date
- 2024-01-23
- Data Types Exposed
- Previously reported data leaks, including records from LinkedIn, Twitter, and Weibo
- Affected Records
- The database was reported to contain 26 billion records; the article does not establish how many records were exposed from Leak-Lookup.
- Affected Data Size
- 12 TB
- Operational Impact
- The database was exposed due to a firewall/server misconfiguration and was reportedly secured after the issue was addressed. The article says it did not appear that registered users' information was compromised.
- Ransom Or Extortion
- None reported.
- Claim Status
- claimed