Windows Privilege Escalation via SeManageVolumePrivilege
Summary
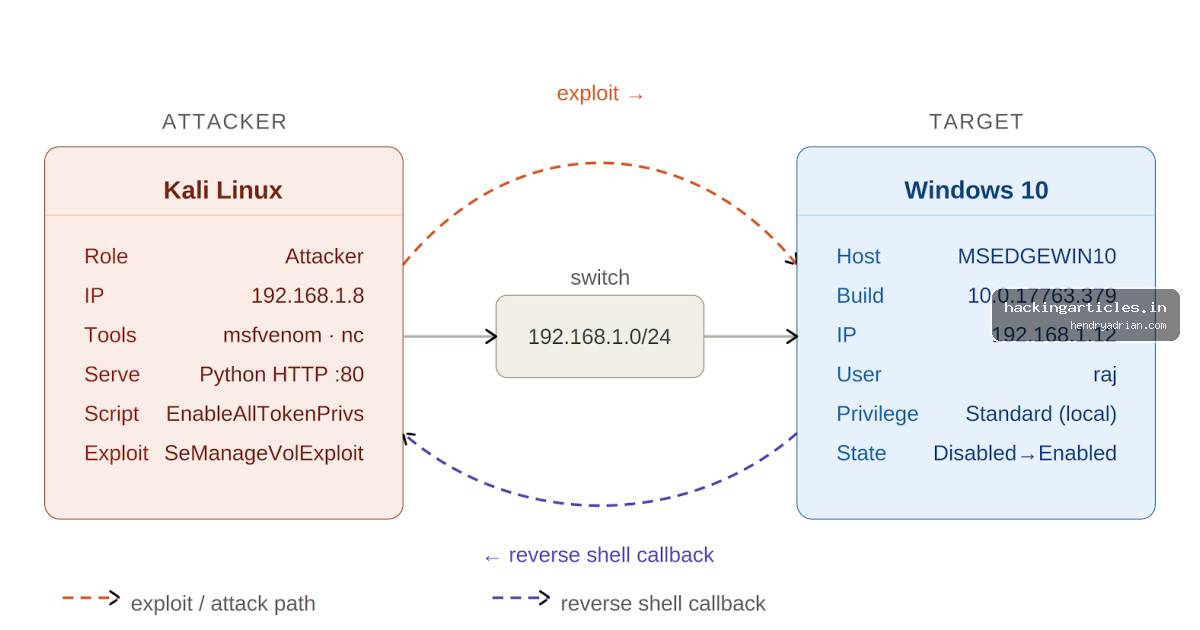
A walkthrough shows how a standard Windows user granted SeManageVolumePrivilege can enable it, rewrite Windows directory ACLs, and exploit DLL-loading paths in Print Spooler, WBEM, or Windows Error Reporting to reach SYSTEM.
Key points
- The demonstrated attack requires a standard user account to have the “Perform volume maintenance tasks” right, which corresponds to SeManageVolumePrivilege.
- After enabling the privilege in the process token, the attacker uses SeManageVolumeExploit to grant BUILTINUsers write access across the Windows directory tree.
- The walkthrough demonstrates three DLL-hijacking routes: Print Spooler and Windows Error Reporting for SYSTEM access, and WBEM for an NT AUTHORITY\NETWORK SERVICE shell.
- The WBEM route can provide a further escalation path because the service account has SeImpersonatePrivilege.
- The lab uses a Windows 10 target and a standard local account; the article presents the scenarios as demonstrations of a risky user-right misconfiguration.
- Recommended defenses include restricting the right to necessary service accounts, auditing user-right assignments and ACL changes, controlling DLL loads, and limiting unnecessary Print Spooler and Windows Error Reporting exposure.
Article Details
- Topic
- Windows privilege escalation through misconfigured SeManageVolumePrivilege and DLL hijacking
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| IPV4 | 192[.]168[.]1[.]8 | Attacker-controlled Kali Linux host used to stage exploit files and receive reverse-shell callbacks in the demonstration. |
| URL | hxxp[:]//192[.]168[.]1[.]8/EnableAllTokenPrivs[.]ps1 | Attacker-hosted script fetched to enable the target account's disabled privileges. |
| URL | hxxp[:]//192[.]168[.]1[.]8/phoneinfo[.]dll | Attacker-hosted reverse-shell DLL fetched for loading through Windows Error Reporting. |
| URL | hxxp[:]//192[.]168[.]1[.]8/Printconfig[.]dll | Attacker-hosted reverse-shell DLL fetched for Print Spooler hijacking. |
| URL | hxxp[:]//192[.]168[.]1[.]8/Report[.]wer | Attacker-hosted crafted error report fetched for the WerTrigger exploitation path. |
| URL | hxxp[:]//192[.]168[.]1[.]8/SeManageVolumeExploit[.]exe | Attacker-hosted exploit executable fetched to rewrite Windows directory permissions. |
| URL | hxxp[:]//192[.]168[.]1[.]8/tzres[.]dll | Attacker-hosted reverse-shell DLL fetched for WBEM hijacking. |
| URL | hxxp[:]//192[.]168[.]1[.]8/WerTrigger[.]exe | Attacker-hosted exploit component fetched to trigger Windows Error Reporting. |
MITRE ATT&CK
T1059.001 · PowerShellThe attacker uses PowerShell to execute the privilege-enabling script and trigger Print Spooler activity.T1105 · Ingress Tool TransferThe attacker downloads exploit components and DLL payloads from an attacker-hosted HTTP server to the target.T1222.001 · Windows PermissionsThe exploit changes Windows directory permissions to grant ordinary users write access.T1574.001 · DLLAttacker-planted DLLs in system paths are loaded by privileged Windows processes.
Vendors
Products
Tools
EnableAllTokenPrivsEnabling the Privilege with EnableAllTokenPrivsmsfvenomThe attacker uses msfvenom to generate a 64-bit reverse TCP shell DLL named Printconfig.dll, setting LHOST to 192.168.1.8 (Kali) and LPORT to 4444.netcatThe attacker starts a netcat listener on port 443 with the following command and then checks privileges.SeManageVolumeExploit#SeManageVolumePrivilege #SeManageVolumeExploit #Printconfig.dll #tzres.dllWerTriggerSpooler DLL hijacking, WBEM tzres.dll substitution, and Windows Error Reporting abuse via WerTrigger—highlighting the danger of misconfiguring the “Perform volume maintenance tasks” right.