Phishing Quote Requests Deliver Remcos RAT via Obfuscated PowerShell
Summary
AhnLab describes a quote-request phishing campaign that uses an obfuscated VBScript and PowerShell chain to bypass UAC and install Remcos RAT, which can remotely control systems and collect user data.
Key points
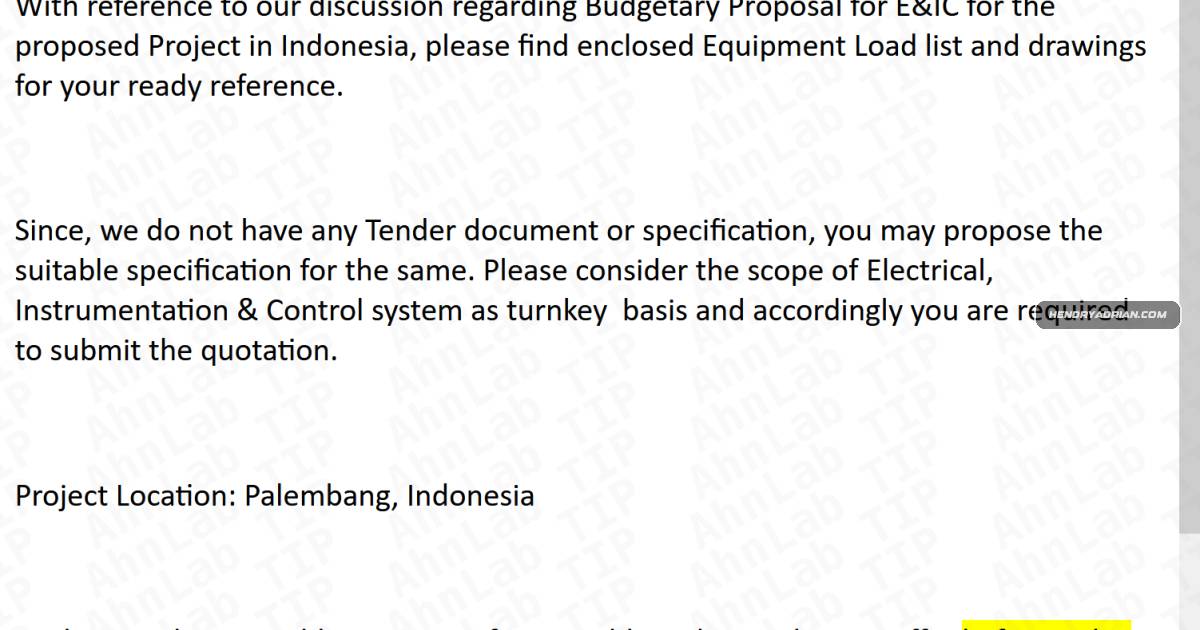
- The phishing email poses as a project quote request and urges recipients to open an attached compressed file.
- The archive contains a VBScript that constructs a PowerShell filename and uses token substitutions to deobfuscate and run commands.
- PowerShell downloads a multi-part payload from Google Drive and stores it under %APPDATA%\Maleic.For.
- A secondary PowerShell payload uses a ShellWindows COM object and explorer.exe to bypass UAC and launch further commands.
- The loader decrypts the payload with XOR and executes it in memory; the final payload downloads and injects Remcos RAT into MicrosoftEdgeUpdate.exe.
- Remcos RAT can run remote commands, log keystrokes, capture screens, manipulate files, and send collected information to its C2 server.
- AhnLab advises checking sender domains and suspicious attachments; the report lists the Remcos C2 address as 102.220.160[.]104:2404.
Article Details
- Attack Vectors
- Phishing emails disguised as project quote requests prompt recipients to download a compressed attachment containing a hidden VBScript.
- The VBScript constructs a PowerShell executable name from characters extracted from notepad.Exe; the resulting PowerShell code uses token substitution to reconstruct and execute commands.
- The script downloads a three-section payload from a specific Google Drive resource. A secondary PowerShell section runs first, followed by a loader that decrypts and executes the payload in memory.
- The secondary PowerShell payload uses a ShellWindows COM object and explorer.Exe ShellExecute path to bypass UAC and launch an elevated PowerShell process.
- The decrypted payload downloads Remcos RAT from a second Google Drive resource, decrypts it, and injects it into MicrosoftEdgeUpdate.Exe.
- Defensive Notes
- Verify that a sender's email address belongs to an official domain.
- Inspect links before clicking and check attachments for suspicious extensions, including .Exe, .Vbs, and .Js.
- Verify a page's official URL before entering credentials or other sensitive information; the source also advises checking its HTTPS security indication.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| IPV4 | 102[.]220[.]160[.]104 | Remcos RAT C2 address, reported with port 2404. |
| MD5 | af87821d3cb4f1d72bfb8002437593ec | MD5 listed in the article's threat-indicator section; the hashed artifact is not specified. |
| URL | hxxp[:]//drive[.]google[.]com/uc?Export=download&id=1ge2-tdX0-_A6ZU6FDMEFynhz1m0L5lHm | Specific Google Drive resource identified as the additional-payload download location. |
| URL | hxxp[:]//drive[.]google[.]com/uc?Export=download&id=1yJZysgMU6LZmCZtpko0y1uO1jsbYDIRO | Specific Google Drive resource identified as the Remcos RAT download location. |
| URL | hxxps[:]//drive[.]google[.]com/uc?export=download&id=1ge2-tdX0-_A6ZU6FDMEFynhz1m0L5lHm | Additional-payload download resource as written in the article's IOC list. |
| URL | hxxps[:]//drive[.]google[.]com/uc?export=download&id=1yJZysgMU6LZmCZtpko0y1uO1jsbYDIRO | Remcos RAT download resource as written in the article's IOC list. |
MITRE ATT&CK
T1027 · Obfuscated Files or InformationThe VBScript constructs 'powershell' from extracted characters, while PowerShell code uses token substitutions to conceal commands.T1041 · Exfiltration Over C2 ChannelRemcos RAT transmits collected information and execution results through communication with its C2 server.T1055 · Process InjectionThe payload injects decrypted Remcos RAT into MicrosoftEdgeUpdate.Exe for execution.T1056.001 · KeyloggingThe article identifies keylogging as one of Remcos RAT's information-collection functions.T1059.001 · PowerShellPowerShell scripts reconstruct and execute commands, run the secondary payload, and launch a subsequent elevated PowerShell process.T1059.005 · Visual BasicA VBScript in the compressed attachment constructs the PowerShell executable name and initiates subsequent execution.T1105 · Ingress Tool TransferThe scripts download an additional payload and, later, Remcos RAT from specified Google Drive resources.T1113 · Screen CaptureThe article identifies screen capture as one of Remcos RAT's information-collection functions.T1140 · Deobfuscate/Decode Files or InformationPowerShell restores obfuscated commands, and the loader XOR-decrypts a payload before executing it in memory.T1548.002 · Bypass User Account ControlA secondary PowerShell payload creates a ShellWindows COM object and uses the explorer.Exe ShellExecute path to bypass UAC.T1566.001 · Spearphishing AttachmentQuote-request phishing emails prompt recipients to download a compressed attachment containing a hidden VBScript.