
Huntress Reports Token-Replay Campaign Compromised 97 Microsoft 365 Accounts
Summary
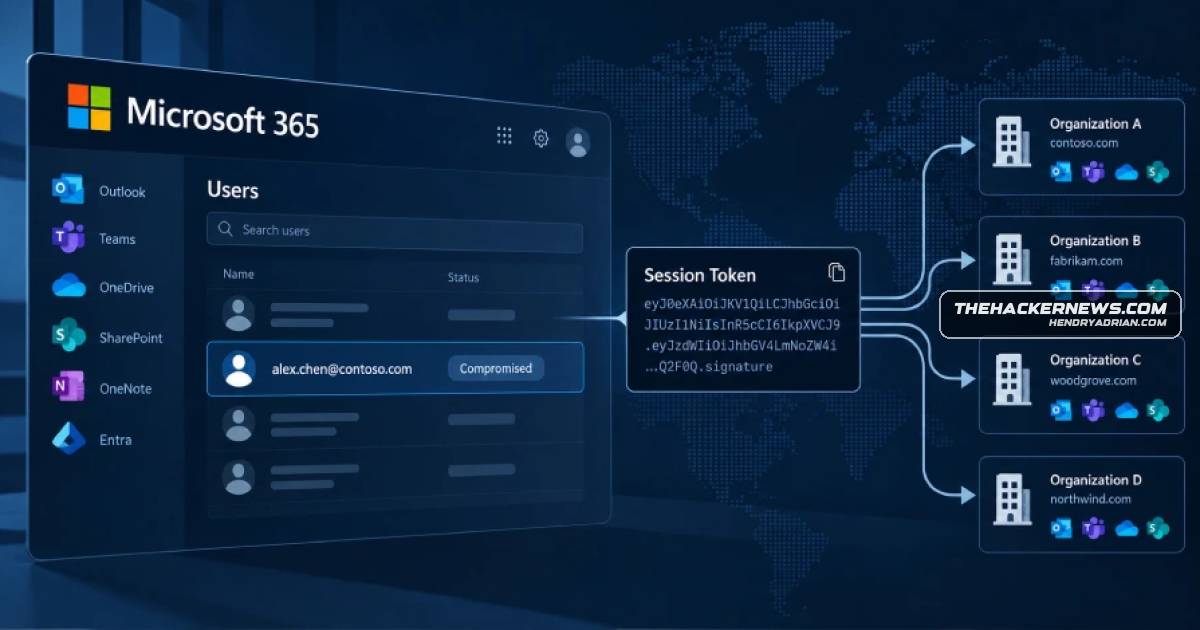
Huntress reports that a token-replay campaign compromised 97 Microsoft 365 accounts across 79 organizations, registered 48 rogue Entra devices, altered MFA methods and created hidden inbox rules.
Key points
- Huntress observed 497 successful Microsoft 365 sign-ins across 79 organizations, from more than 200,000 login attempts between July 14 and September 22, 2026.
- The attackers used adversary-in-the-middle pages and other methods to obtain sign-in tokens, then replayed them to access accounts without repeating MFA.
- Attackers registered 48 rogue Entra devices and, in at least 19 organizations, removed victims’ existing MFA methods and registered new ones.
- Hidden inbox rules were used to delete or conceal messages mentioning payroll, deposits or bonuses; one mailbox was also used to send spam.
- Huntress recommends revoking sessions, resetting passwords, auditing Entra devices and MFA methods, reviewing inbox rules and enterprise apps, and restricting device-code workflows with Conditional Access.
Article Details
- Event Type
- Microsoft 365 token-replay campaign using adversary-in-the-middle relays and other token-stealing methods
- Impact
- Huntress reported 497 successful sign-ins across 79 organizations from more than 200,000 login attempts, with 97 accounts compromised and 48 rogue Entra devices registered. Attackers also replaced MFA methods, created hidden inbox rules to delete or conceal messages, and used at least one compromised mailbox to send spam.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| IPV4 | 193[.]26[.]115[.]221 | Reported as the IP address from which the campaign was first observed; Huntress traced campaign login attempts to its surrounding IP range. |
MITRE ATT&CK
T1098.005 · Device RegistrationAttackers registered rogue devices in victim organizations' directories to obtain a more durable way to request tokens.T1550.004 · Web Session CookieAttackers replayed stolen sign-in session tokens to access Microsoft 365 accounts.T1557 · Adversary-in-the-MiddleThe campaign used an adversary-in-the-middle relay to capture credentials, MFA codes, and sign-in tokens.T1564.008 · Email Hiding RulesAttackers created hidden inbox rules to delete or move messages referencing payroll, deposits, and bonuses.
People
Andrea HatcherHuntress researcher who reported on the campaign's sign-in activity and token-replay method.Andrew SchwartzHuntress researcher who reported on the campaign's sign-in activity and token-replay method.Matt PotoHuntress researcher who reported on the campaign's sign-in activity and token-replay method.Susannah MattHuntress researcher who reported on the campaign's sign-in activity and token-replay method.
Malware
Vendors
Products
Entra200,000 login attempts, with the attackers ultimately compromising 97 accounts and registering 48 rogue Entra devices.Microsoft 365 Apps for EnterpriseCybersecurity researchers have disclosed a Microsoft 365 campaign that has been observed leveraging an adversary-in-the-middle (AitM) relay to capture sign-in sessions and then replay the stolen tokens to break intoMicrosoft Entra ID ProtectionThe mailbox was then used to send outbound spam to hundreds of external recipients before Microsoft Entra ID Protection rated the account high risk.