
Aurora Claims Benshaw, Inc. Data in Ransomware Leak
Summary
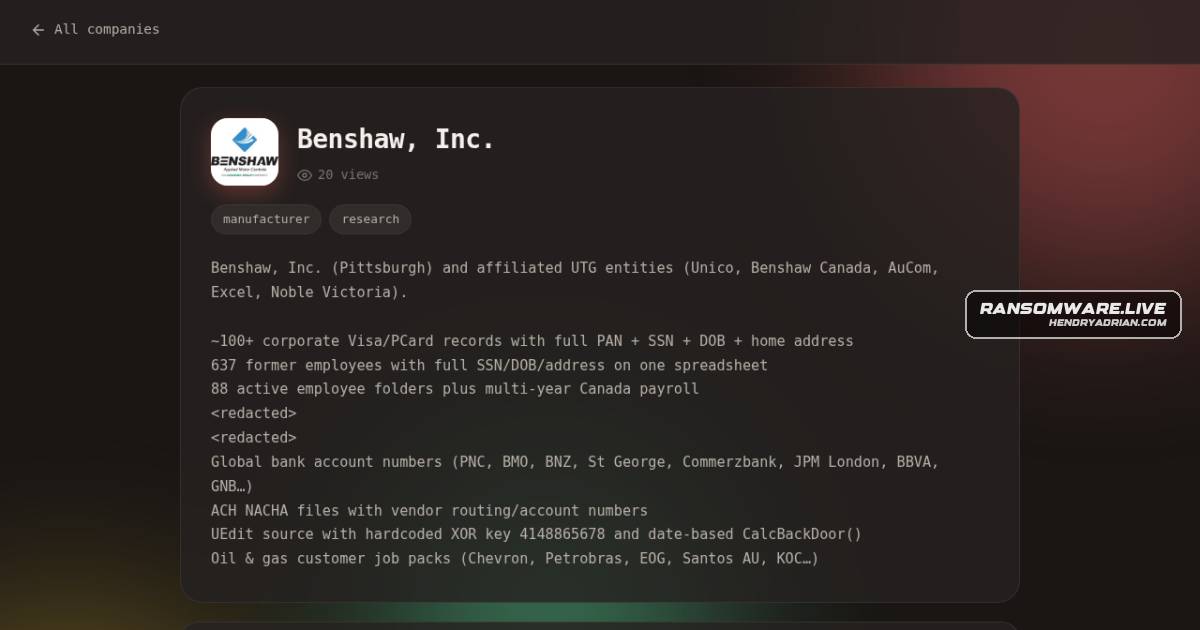
A ransomware.live monitoring post records an aurora claim involving Benshaw, Inc. The group allegedly exposed employee, payment, banking, payroll, and customer files; the post says it cannot confirm the claims.
Key points
- The ransomware.live post identifies Benshaw, Inc., a U.S. manufacturing company, as the victim and aurora as the claiming group.
- The post says aurora published its claim on August 27, 2026; the record lists discovery on September 7, 2026.
- Allegedly exposed information includes payment-card records, employee personal data, payroll files, bank account numbers, and vendor payment details.
- The post also lists source code and customer job packs among the claimed information.
- The post states that the claims are based on the ransomware group’s public statements and have not been independently confirmed.
Article Details
- Victim
- Benshaw, Inc.
- Claim Date
- 2026-08-27
- Encryption Status
- Unknown; the source does not report whether systems were encrypted.
- Exfiltration Status
- Unverified group claim; the source cannot confirm whether data was exfiltrated.
- Exfiltrated Data
- The claim reportedly lists corporate card records, employee personal information, payroll data, bank account details, ACH files, source code, and customer job packs. The source does not verify the data's authenticity.
- Ransom Demand
- Unknown; no ransom demand is reported.
- Leak Status
- A listing was published on the group's blog, but the source says the claims are unverified.