
Aurora Claims Theft of Sensitive Data from Jinny Beauty Supply
Summary
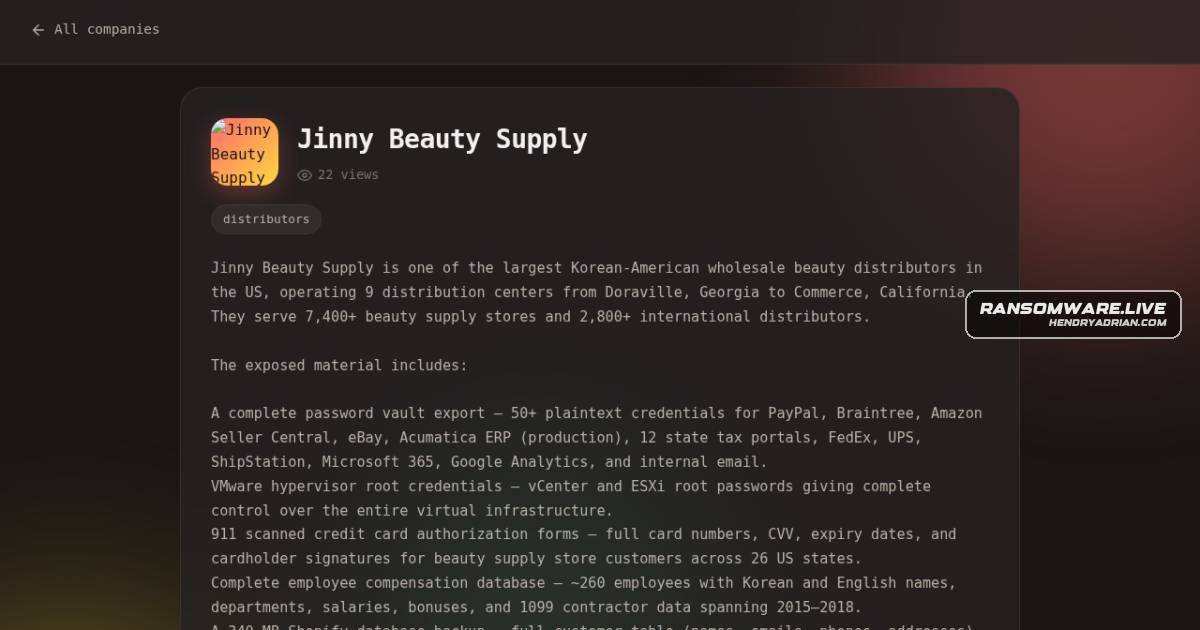
Aurora claims it stole credentials, payment-card forms, employee records, and business databases from Jinny Beauty Supply. The monitoring post says the group's claims have not been confirmed.
Key points
- The ransomware.live post attributes the claim to the Aurora group and lists Jinny Beauty Supply as the victim; it says the information could not be independently confirmed.
- Claimed data includes password-vault exports with credentials for business services and VMware vCenter and ESXi root accounts.
- The group allegedly exposed scanned customer credit-card authorization forms containing full card details and signatures.
- Other claimed data includes employee compensation and tax documents, including direct-deposit information.
- The post also lists Shopify and SQL Server backups and Active Directory enumeration data.
Article Details
- Victim
- Jinny Beauty Supply
- Claim Date
- 2026-09-07
- Encryption Status
- Unknown; the source reports a group claim of data theft but does not report encryption.
- Exfiltration Status
- Claimed by the ransomware group; not independently confirmed.
- Exfiltrated Data
- The group reportedly claimed exposure of credentials, password vault exports, VMware hypervisor credentials, scanned credit card authorization forms, employee and financial records, Shopify and SQL Server backups, and Active Directory enumeration data. The source says it cannot confirm the accuracy of the claims.
- Leak Status
- A group blog listing is cited as the source of the claims; the source does not establish whether data was published or whether the material is authentic.