
Researchers Find Patched ChatGPT Lockdown Mode Flaw That Could Enable Zero-Click Chat Exfiltration
Summary
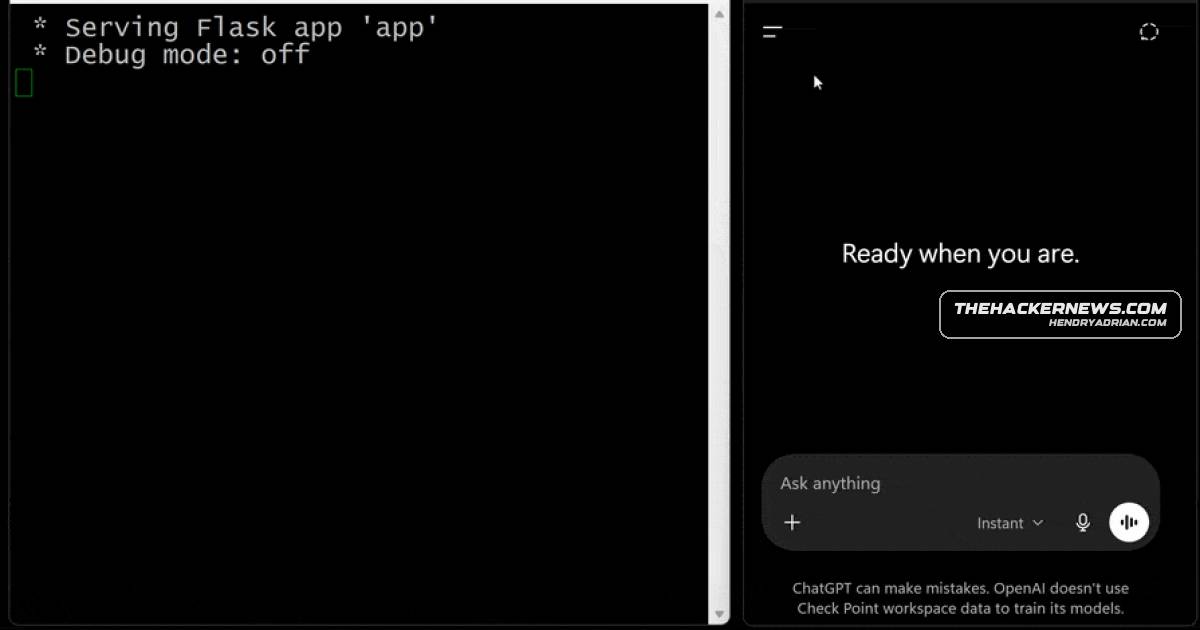
Check Point researchers said a flaw in ChatGPT HTML previews could bypass Lockdown Mode protections, enabling chat-data exfiltration or malicious payload delivery. OpenAI addressed the issue on September 18, 2026.
Key points
- The flaw affected HTML page previews in ChatGPT code blocks, where rendered content was sandboxed.
- Check Point said nested sandboxed frames and popup handling could let content escape the sandbox and bypass Lockdown Mode restrictions.
- A crafted prompt, malicious GPT, or shared chat could potentially be used to exfiltrate data or chat messages, or deliver malicious payloads.
- A popup controlled by an attacker could display social-engineering lures, such as a fake ChatGPT update, to trick users into downloading malware.
- OpenAI addressed the vulnerability on September 18, 2026, following responsible disclosure.
Article Details
- Vulnerability Types
- Sandbox escape through popup handling in HTML previews
- Lockdown Mode protection bypass
- Exploitation Status
- unknown
- Exploit Availability
- unknown
- Patch Status
- available
People
ELI SMADJAHead of research at Check Point; described the vulnerability and its potential for silent chat-data theft, phishing, and malware delivery.Mukul GoyalSecurity researcher who described a separate, previously disclosed ChatGPT sandbox and content-security-policy bypass involving shared links.