
INC Ransomware Reported as Dominant Actor Exploiting SonicWall SMA 1000 Flaws
Summary
Researchers link INC Ransomware activity targeting SonicWall SMA 1000 appliances to CVE-2026-15409 and CVE-2026-15410, with reported credential and session-data theft; attribution and victim claims remain partly unconfirmed.
Key points
- Resecurity reported increased INC Ransomware activity and multiple victims listed on the group’s data leak site; Ransomware[.]Live reported 885 claimed victims to date.
- The suspected exploitation involves CVE-2026-15409 and CVE-2026-15410, which could enable arbitrary command execution and device takeover; SonicWall released fixes in mid-July 2026.
- Rapid7 reported attackers used appliance access to extract credentials, active session databases, and TOTP MFA seed configurations, potentially supporting persistent access and lateral movement.
- Volexity attributed pre-disclosure exploitation beginning June 22, 2026, to UTA0533; reported tools include KNUCKLEBALL, Suo5, and the ORANGETAIL Java web shell.
- Resecurity said listed victims included government and private organizations in several countries, and reported that some received calls and emails from people claiming to help with ransomware issues.
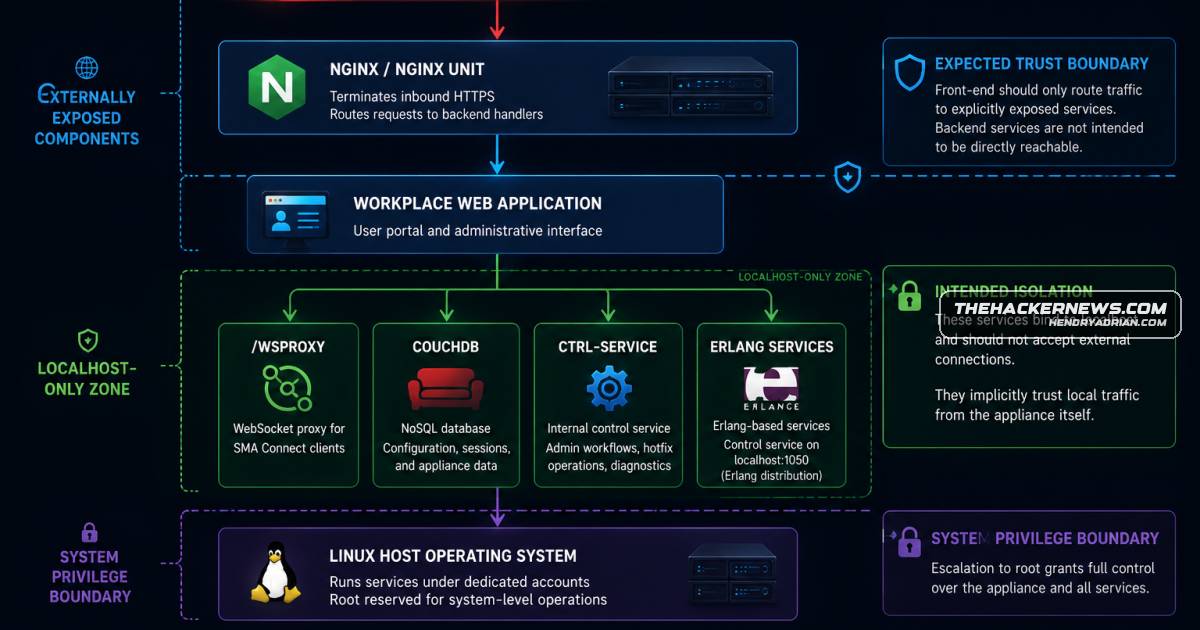
- Resecurity advised patching, threat hunting, credential rotation, and integrity checks, including reviewing /wsproxy activity and correlating it with authentication and lateral-movement activity.
Article Details
- Event Type
- Reported zero-day exploitation of SonicWall SMA 1000 VPN vulnerabilities by INC Ransomware and a threat cluster tracked as UTA0533.
- Impact
- The vulnerabilities could be chained to enable arbitrary command execution and device takeover. Rapid7 reported that attackers used their foothold to extract credentials, active session databases, and TOTP MFA seed configurations, with the aim of maintaining access and moving laterally into corporate networks. Resecurity reported victims across government and private organizations in several countries. SonicWall released fixes in mid-July 2026.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
info@helprans[.]com | Email supplied by a caller who claimed to represent hackers for ransomware negotiations. Resecurity described such victim contacts as pressure tactics, but did not confirm a link to INC Ransomware. |
MITRE ATT&CK
CVE
CVE-2026-15409INC Ransomware has become the dominant threat actor exploiting newly disclosed flaws in SonicWall SMA 1000 VPN appliances, with attacks linked to CVE-2026-15409 and CVE-2026-15410.CVE-2026-15410INC Ransomware has become the dominant threat actor exploiting newly disclosed flaws in SonicWall SMA 1000 VPN appliances, with attacks linked to CVE-2026-15409 and CVE-2026-15410.
People
Threat Actors
Malware
Vendors
Products
Tools
Countries
Australiasite between July 17 and August 1, 2026, include private sector and government organizations from Australia, the U.S., the U.A.E., Colombia, Switzerland, and other countries.Colombia1, 2026, include private sector and government organizations from Australia, the U.S., the U.A.E., Colombia, Switzerland, and other countries.Switzerlandinclude private sector and government organizations from Australia, the U.S., the U.A.E., Colombia, Switzerland, and other countries.U.A.E.17 and August 1, 2026, include private sector and government organizations from Australia, the U.S., the U.A.E., Colombia, Switzerland, and other countries.United StatesJuly 17 and August 1, 2026, include private sector and government organizations from Australia, the U.S., the U.A.E., Colombia, Switzerland, and other countries.