
Lazarus Uses Windows Zero-Day in Dream Job Campaign to Deploy Troy Backdoor
Summary
Check Point Research attributes attacks on defense and aerospace targets in four countries to Lazarus Group, reporting exploitation of Windows CVE-2026-68820 in Operation Dream Job to deliver Troy, MISTPEN, ForestTiger and FudModule 3.1.
Key points
- Check Point Research attributes the campaign to Lazarus Group and reports targeting of defense and aerospace organizations in France, Germany, Brazil and India.
- The campaign exploits Windows AFD.sys privilege-escalation flaw CVE-2026-68820, patched in Microsoft's August 2026 updates, to obtain SYSTEM privileges.
- Fake recruiter messages and trojanized PDF software are used to lure victims into installing malware.
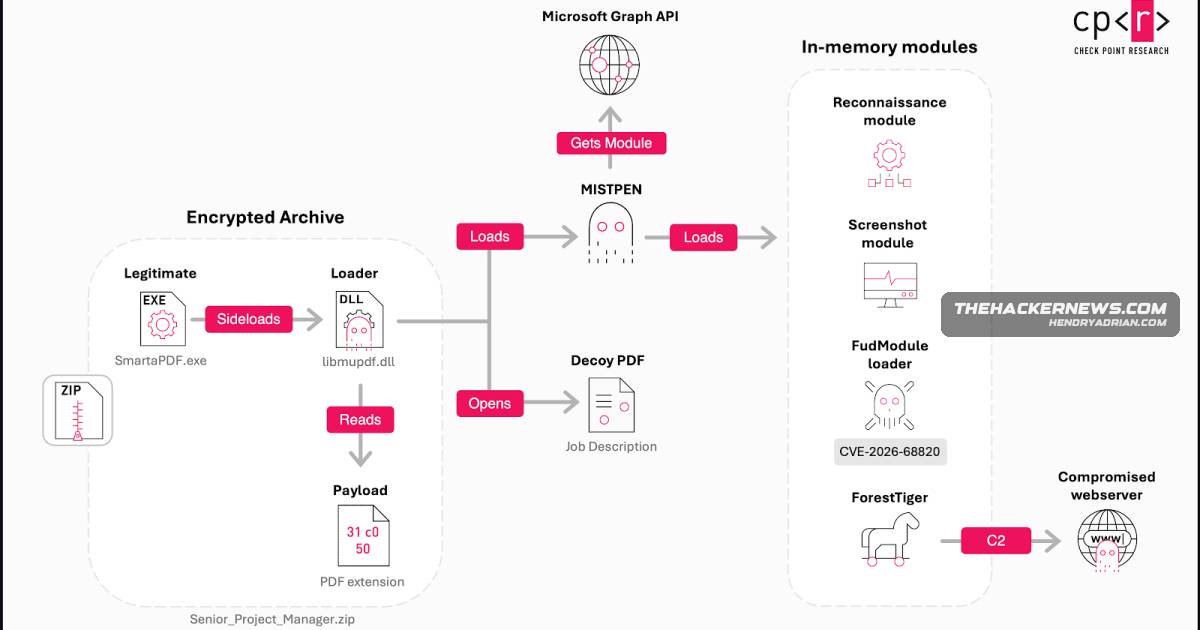
- One infection chain uses DLL side-loading to deliver MISTPEN, which retrieves modules and helps deploy ForestTiger.
- A trojanized SecurityPDF viewer can load the Troy backdoor into memory; Troy supports file operations, shell access and other operator commands.
- FudModule 3.1 reportedly tampers with Smart App Control, while MISTPEN modules collect host and process information and capture screenshots.
- The campaign reportedly uses compromised WordPress, SharePoint and Roundcube systems for command and control; some Roundcube servers were exploited via CVE-2025-49113 to install the RelayShell web shell.
Article Details
- Attack Vectors
- Fake recruiter messages and job offers were used to build trust and lure targets into opening a malicious PDF or installing a trojanized PDF viewer.
- A DLL side-loading chain used a malicious DLL to present a job-description lure and download and execute MISTPEN in memory.
- A trojanized SecurityPDF viewer decrypted and launched the Troy backdoor when it detected a specific marker in an opened PDF.
- MISTPEN used Microsoft Graph API and OneDrive to retrieve and run modules, including components involved in reconnaissance and privilege escalation.
- The attackers exploited CVE-2026-68820 in AFD.sys to obtain SYSTEM privileges and injected another MISTPEN instance into a SYSTEM process.
- Compromised WordPress and SharePoint sites and vulnerable Roundcube servers were used as ForestTiger command-and-control servers; attackers reportedly exploited CVE-2025-49113 to infect Roundcube servers with RelayShell.
- Defensive Notes
- Apply security updates promptly, including the August 2026 Windows update addressing CVE-2026-68820.
- Verify software through official channels rather than search rankings, and be cautious of recruiter messages, job-related PDFs, and purported PDF viewers.
- Extend zero-trust practices to legitimate-looking sites and partners, since compromised infrastructure was used in the campaign.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| DOMAIN | enveil[.]online | Domain reported to impersonate Enveil and distribute the trojanized SecurityPDF viewer. |
| DOMAIN | envell[.]xyz | Domain reported to impersonate Enveil and distribute the trojanized SecurityPDF viewer. |
| DOMAIN | uxtramine[.]org | Domain reported among sites impersonating Enveil to distribute the trojanized SecurityPDF viewer. |
MITRE ATT&CK
T1005 · Data from Local SystemTroy supports file enumeration and archiving, with file upload and exfiltration capabilities.T1041 · Exfiltration Over C2 ChannelMISTPEN exfiltrated collected host information through infrastructure using Microsoft Graph API and OneDrive.T1055 · Process InjectionTroy supports in-memory DLL injection, and another MISTPEN instance was injected into a SYSTEM process.T1057 · Process DiscoveryMISTPEN's PvPlugin collected details about running processes.T1068 · Exploitation for Privilege EscalationThe attackers exploited the AFD.sys local privilege-escalation flaw to obtain SYSTEM privileges.T1082 · System Information DiscoveryMISTPEN's GetInfoPlugin and LPE loader collected host information for reconnaissance.T1102.002 · Bidirectional CommunicationMISTPEN communicated with attacker-controlled infrastructure using Microsoft Graph API and OneDrive.T1105 · Ingress Tool TransferMISTPEN downloaded modules, and the campaign retrieved and ran payloads through its infection chains.T1113 · Screen CaptureMISTPEN's OneScreenCapture module captured desktop screenshots, including across monitors.T1204.002 · Malicious FileVictims were lured into opening a malicious PDF or installing a trojanized PDF viewer.T1562.001 · Disable or Modify ToolsFudModule 3.1 concealed malicious tools from security software and tampered with Smart App Control.T1566.003 · Spearphishing via ServiceLazarus Group used fake recruiter messages on platforms such as LinkedIn to approach targets with job offers.T1574.002 · DLL Side-LoadingOne infection sequence used DLL side-loading to trigger a malicious DLL and execute MISTPEN.
CVE
CVE-2025-49113Many of the Roundcube servers have been found to be vulnerable to CVE-2025-49113, with the attackers leveraging it to infect them with a previously undocumented PHP web shell codenamed RelayShell to enable the exchangeCVE-2026-68820Lazarus Group is exploiting a recently patched Windows zero-day, CVE-2026-68820, to deliver a new backdoor called Troy against defense and aerospace targets in France, Germany, Brazil, and India through Operation Dream
People
Threat Actors
Malware
ForestTigerThe campaign uses fake recruiter lures, trojanized PDF software, and compromised legitimate sites and servers to spread MISTPEN, ForestTiger, FudModule 3.1, and RelayShell while evading security controls.FudModule 3.1The campaign uses fake recruiter lures, trojanized PDF software, and compromised legitimate sites and servers to spread MISTPEN, ForestTiger, FudModule 3.1, and RelayShell while evading security controls.MISTPENThe campaign uses fake recruiter lures, trojanized PDF software, and compromised legitimate sites and servers to spread MISTPEN, ForestTiger, FudModule 3.1, and RelayShell while evading security controls.RelayShellThe campaign uses fake recruiter lures, trojanized PDF software, and compromised legitimate sites and servers to spread MISTPEN, ForestTiger, FudModule 3.1, and RelayShell while evading security controls.TroyGroup is exploiting a recently patched Windows zero-day, CVE-2026-68820, to deliver a new backdoor called Troy against defense and aerospace targets in France, Germany, Brazil, and India through Operation Dream Job.
Vendors
Products
Microsoft SharePointThe campaign also used compromised WordPress, SharePoint, and Roundcube systems for C2.Microsoft WindowsLazarus Group is exploiting a recently patched Windows zero-day, CVE-2026-68820, to deliver a new backdoor called Troy against defense and aerospace targets in France, Germany, Brazil, and India through Operation DreamRoundcube WebmailThe campaign also used compromised WordPress, SharePoint, and Roundcube systems for C2.SecurityPDFTrojanized “SecurityPDF” PDF viewer, in which victims are instructed to download SecurityPDF from a website impersonating Enveil.WordPressThe campaign also used compromised WordPress, SharePoint, and Roundcube systems for C2.
Countries
Brazilto deliver a new backdoor called Troy against defense and aerospace targets in France, Germany, Brazil, and India through Operation Dream Job.Francezero-day, CVE-2026-68820, to deliver a new backdoor called Troy against defense and aerospace targets in France, Germany, Brazil, and India through Operation Dream Job.GermanyCVE-2026-68820, to deliver a new backdoor called Troy against defense and aerospace targets in France, Germany, Brazil, and India through Operation Dream Job.Indiadeliver a new backdoor called Troy against defense and aerospace targets in France, Germany, Brazil, and India through Operation Dream Job.
Industries
Aerospacepatched Windows zero-day, CVE-2026-68820, to deliver a new backdoor called Troy against defense and aerospace targets in France, Germany, Brazil, and India through Operation Dream Job.Defensea recently patched Windows zero-day, CVE-2026-68820, to deliver a new backdoor called Troy against defense and aerospace targets in France, Germany, Brazil, and India through Operation Dream Job.