Chrome Extension Resumes Malicious Updates, Redirecting Users to Affiliate Links
Summary
Netskope reports that a relisted Chrome extension added affiliate redirects triggered by updates and uninstalls after earlier versions stole AI conversations. The extension remains available, and Netskope recommends removing it and restricting extension installs.
Key points
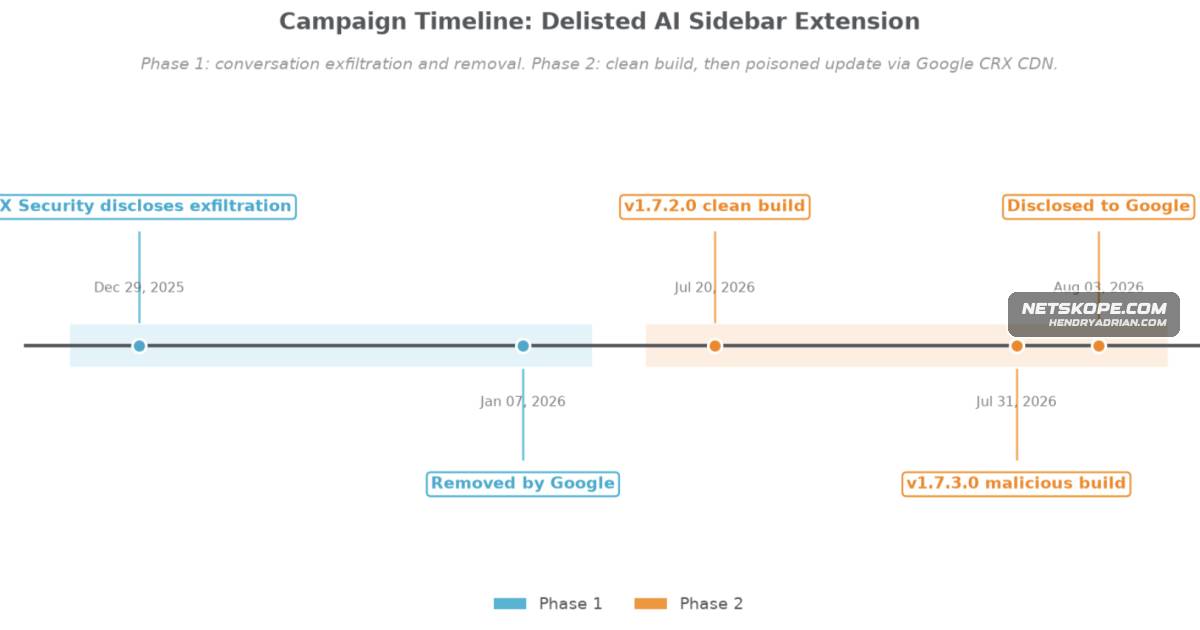
- The extension “AI Sidebar with DeepSeek AI” previously scraped ChatGPT and DeepSeek conversations; that exfiltration code was removed before version 1.7.x.
- After a clean predecessor, version 1.7.3.0 added a payload that opens an affiliate link in a foreground tab on extension updates and uninstalls.
- The uninstall behavior uses repeated writes to win a race for Chrome’s single uninstall URL; the affiliate destination can be changed through a Bitly redirect.
- Netskope says the extension was relisted and remains on the Chrome Web Store at version 1.7.4, with 200,000 users as of August 25, 2026.
- The extension’s ID is inhcgfpbfdjbjogdfjbclgolkmhnooop; Netskope says it has blocked the extension across its customers.
- Netskope recommends removing the extension, auditing browser policies, restricting installs to approved extensions, and inspecting extension packages.
Article Details
- Attack Vectors
- The extension used its update and uninstall events to silently open an affiliate redirect in a foreground browser tab.
- Earlier versions scraped ChatGPT and DeepSeek conversation content, base64-encoded it, and posted it to two domains identified as prior C2 infrastructure.
- The operator inserted the monetization payload into an otherwise similar extension build and distributed it through the Chrome Web Store and Google’s CRX infrastructure.
- Defensive Notes
- Maintain an inventory of installed browser extensions and use default-deny installation policies with explicit exceptions.
- Inspect extension packages inline, including packages delivered through vendor-owned CDNs.
- Treat removal of an extension from an official store as a prompt for internal remediation, not proof that the threat is resolved.
- Remove extension ID inhcgfpbfdjbjogdfjbclgolkmhnooop from managed browsers and verify it is not in force-install or allowlist policies.
- Use an extension allowlist or targeted blocklist policy to prevent the extension from running.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| DOMAIN | chatsaigpt[.]com | Identified as prior C2 infrastructure used by pre-1.7.x versions to exfiltrate AI conversation content; reported offline. |
| DOMAIN | deepaichats[.]com | Identified as prior C2 infrastructure used by pre-1.7.x versions to exfiltrate AI conversation content; reported offline. |
| SHA256 | 15ca814190c84c662bee1276dd39b504ae86fc7ee5e86b13775b77672242dc25 | CRX hash for the extension identified in the article; the article reports that version 1.7.4 retains the malicious capability. |
| SHA256 | 2a57de8abd0d15e92784280e5d39906d69a2ae7bb9b2875c77c626e9f0794e05 | Malicious version 1.7.3.0 CRX hash. |
| URL | hxxps[:]//bit[.]ly/3RPe03x | Affiliate redirect opened silently on extension updates and uninstall; the article says its destination can change. |
MITRE ATT&CK
Vendors
GoogleSince publication, telemetry extending back to March 5, 2026 shows the extension has been continuously delivered via Google’s CRX infrastructure across seven versions.NetskopeNetskope has blocked it across our customers.OX SecurityIn December 2025, OX Security published research showing that pre-1.7.x versions of this extension scraped ChatGPT and DeepSeek conversation content from the page and posted it, base64-encoded, to deepaichats[.]com and
Products
AI Sidebar with DeepSeek AIThe Chrome extension “AI Sidebar with DeepSeek AI” that Google removed from the Chrome Web Store in January 2026 for stealing AI conversation content resumed shipping code to enterprise endpoints in July 2026.BuzzyThe link resolves through Bitly to Buzzy, an AI video generation service that runs a public affiliate program paying 30% commission on referred subscriptions.ChatGPTAdditionally, it suppresses the redirection of DeepSeek users to ChatGPT.Chrome Web StoreAs of August 25, the extension remains live on the Chrome Web Store at version 1.7.4 with 200,000 users.DeepSeekThe Chrome extension “AI Sidebar with DeepSeek AI” that Google removed from the Chrome Web Store in January 2026 for stealing AI conversation content resumed shipping code to enterprise endpoints in July 2026.Google ChromeAs of August 25, the extension remains live on the Chrome Web Store at version 1.7.4 with 200,000 users.Netskope Advanced Threat ProtectionNetskope Advanced Threat Protection identifies the covert behavior: silent tab injection and uninstall-URL hijacking.Netskope Enterprise BrowserCustomers running Netskope Enterprise Browser (EB) can enforce extension policy at the browser layer: allowlist (only approved IDs load), blocklist (named IDs are blocked), or force-install (approved extensions areNetskope NG SWGNetskope NG SWG URL Filtering categorizes the Phase 1 exfiltration domains chatsaigpt[.]com and deepaichats[.]com as C&C Server and Malicious Site.Netskope Threat ProtectionIn July 2026, Netskope Threat Protection detected and blocked the latest version 1.7.3.0 of the .crx object arriving on enterprise endpoints from Google CDN.