
Aurora Ransomware Group Claims Chip 1 Exchange Breach, Citing Employee and Financial Data
Summary
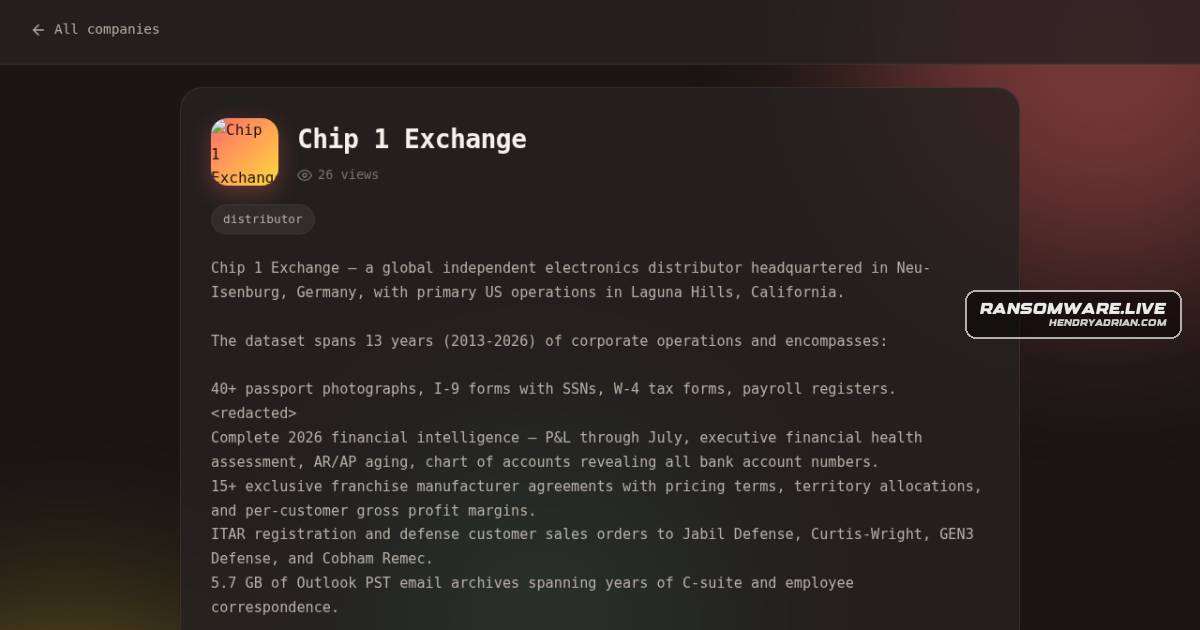
Ransomware.live reports that the aurora group claims to have compromised Singapore-based Chip 1 Exchange and exposed personnel, financial, defense-sales and email data. The claims are unverified.
Key points
- The ransomware.live record attributes the breach claim to the aurora group; the post says it cannot confirm the claims.
- The group reportedly claims exposure of passport photos, I-9 forms with SSNs, W-4 tax forms and payroll records.
- Allegedly exposed financial materials include bank account numbers, financial statements and accounts-receivable/payable records.
- The claim also cites franchise agreements with pricing terms and ITAR-related defense customer sales orders.
- The group reportedly claims to have obtained 5.7 GB of Outlook PST archives containing employee and executive correspondence.
Article Details
- Victim
- Chip 1 Exchange
- Claim Date
- 2026-09-02
- Encryption Status
- Unknown
- Exfiltration Status
- Claimed; unverified
- Exfiltrated Data
- The ransomware group reportedly claimed access to passport photographs, I-9 forms with SSNs, W-4 tax forms, payroll records, financial records and bank account details, manufacturer agreements, ITAR-related defense customer sales orders, and Outlook PST email archives. The article states that the claims could not be confirmed.
- Exfiltrated Size
- 5.7 GB of Outlook PST email archives, according to the claim
- Leak Status
- A claim was published on the ransomware group's blog; the article says the information could not be confirmed.