
Fake TARI Refund Pages Impersonate PagoPA to Harvest Personal and Card Data
Summary
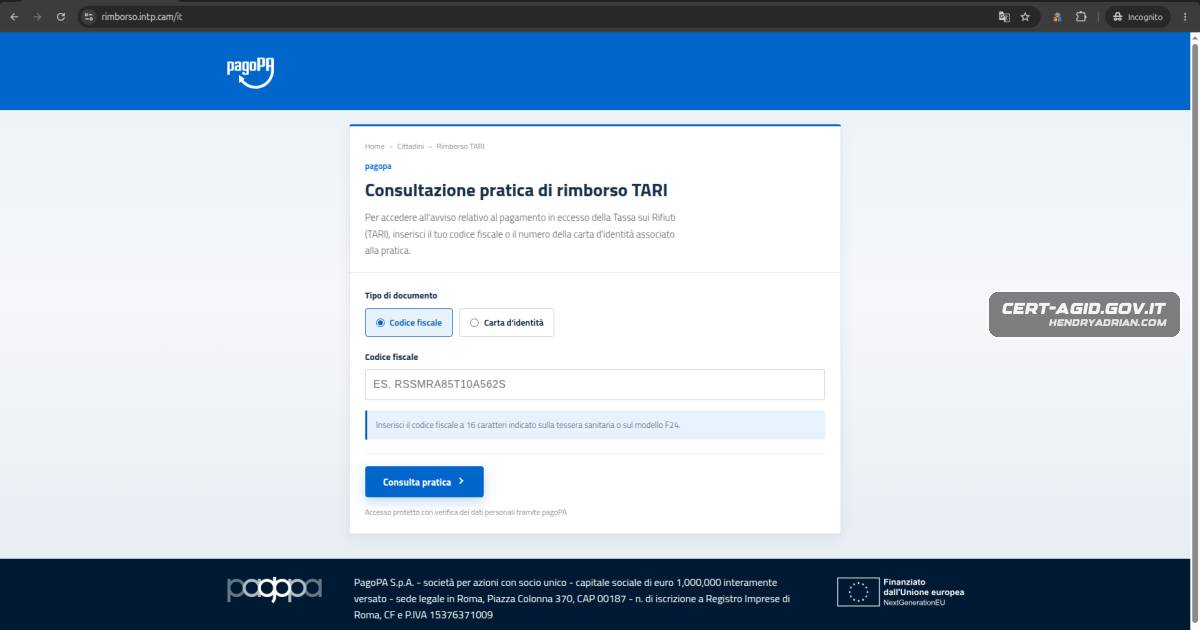
CERT-AGID reported fake PagoPA sites offering a TARI refund to collect identity, contact, and payment-card details for potential fraud and targeted phishing. It began takedown actions and shared indicators with accredited organizations.
Key points
- Fraudulent sites used PagoPA’s name, logo, and graphics to promote a supposed refund for a TARI overpayment.
- The staged workflow requested a tax code or identity-card number, then personal and contact details.
- The final step asked for payment-card details, including the card number, expiry date, and CVV.
- CERT-AGID said the collected information could enable fraudulent card transactions and future targeted phishing.
- CERT-AGID began takedown actions against identified malicious domains and shared indicators of compromise with accredited organizations.
Article Details
- Event Type
- Phishing campaign impersonating PagoPA with a fake TARI overpayment refund.
- Impact
- The fraudulent sites collected victims’ identity, contact, and payment card details, which could be used for fraudulent card transactions and future targeted phishing. CERT-AGID initiated takedown actions against the identified malicious domains and shared the IOCs with accredited organizations. The article does not provide the actual domains or URLs.
MITRE ATT&CK
T1005 · Data from Local SystemThe phishing pages requested identity and payment information from users.T1036 · MasqueradingThe sites impersonated PagoPA using its name, logo, and graphics.T1566.002 · Spearphishing LinkVictims were directed through a fake refund workflow to submit their information.T1583.001 · DomainsThe article states that attackers used malicious domains to host fraudulent PagoPA-themed pages.T1583.006 · Web ServicesThe campaign used web-hosted phishing pages to collect victims’ data.