
Researchers Find 2,539 Secrets in Public Repositories Containing Claude Code Configurations
Summary
Apiiro researchers found 2,539 secrets across 1,994 public repositories containing Claude Code configuration files. They did not test credentials; one organization confirmed an exposed key was live.
Key points
- Researchers scanned 104,185 public configuration-file copies from November 1–3, 2026; analysis of files, Git history, shared settings, and chat transcripts identified 2,539 secrets across 1,994 repositories.
- When users choose “Yes, and don’t ask again,” Claude Code can save the exact permitted command, including embedded credentials, in .claude/settings.local.json.
- A global Git ignore rule may not protect files if a folder later becomes a repository or is cloned; the rule is not added to the project’s .gitignore.
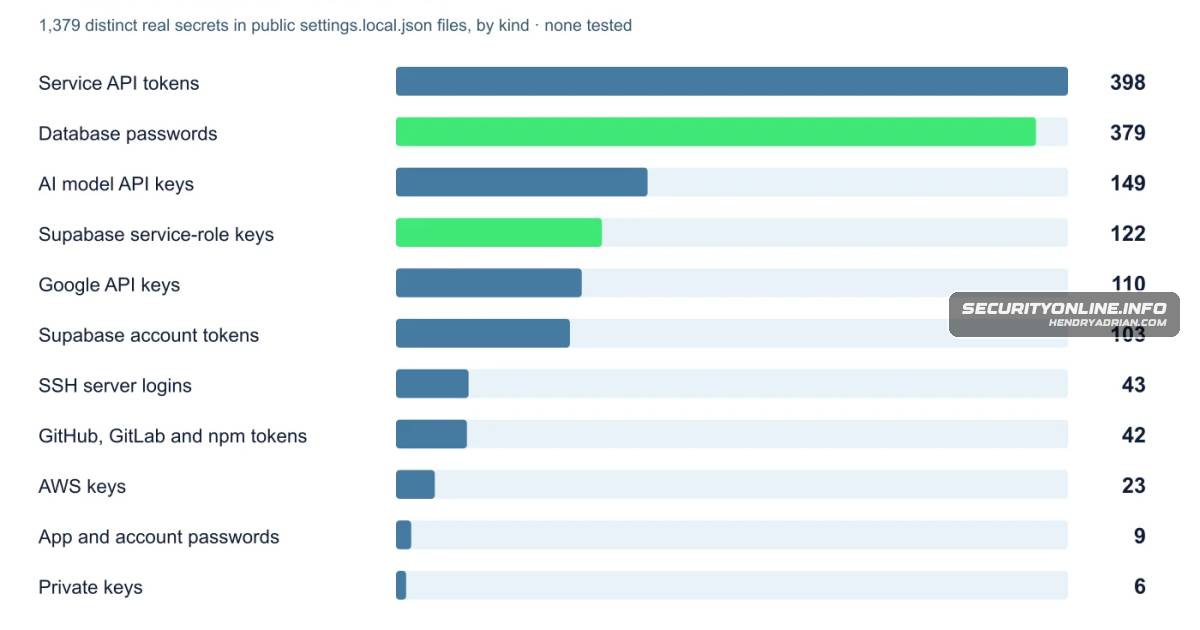
- The exposed credentials included API tokens, database passwords, AI model API keys, Supabase keys, Google API keys, and SSH logins.
- Researchers reported that Gitleaks and TruffleHog missed 215 of the 1,122 exposed files because ordinary inline passwords may lack recognizable token prefixes.
- Researchers did not test credentials or contact hosts; one affected organization confirmed its exposed key was live. Apiiro notified 63 organizations.
- Recommended steps include rotating exposed credentials, removing tracked configuration files, adding agent configuration folders to .gitignore, using environment variables, and scanning for inline command passwords.
Article Details
- Publisher
- Security Online Info
- Report Period
- 2026-11-01 to 2026-11-03
- Scope
- Researchers examined exposed Claude Code configuration files in public repositories and related Git history, shared settings, and agent chat transcripts.
- Sample Size
- 104,185 public copies of the configuration file scanned on GitHub.
- Key Statistics
- The broader analysis found 2,539 real secrets across 1,994 repositories.
- Researchers identified 1,379 distinct secrets on default branches across 1,122 active files.
- gitleaks and TruffleHog together completely missed 215 of the 1,122 exposed files.
- Apiiro notified 63 affected organizations on November 2 and 3, 2026.
- Researchers identified 211 public forks of affected repositories.
- Recommendations
- Search repositories and local machines for .claude/settings.local.json and .claude/settings.json; rotate exposed credentials before cleaning up files.
- Untrack exposed files with git rm --cached and add agent configuration folders to repository .gitignore templates.
- Use environment variables such as $DB_URL instead of entering raw passwords in commands.
- Update pre-commit scanners to detect inline command passwords as well as standard provider tokens.
People
Boris ChernyHead of Claude Code who responded to the exposure issue on Hacker News and said the team was considering ways to prevent it.Matan GiladiApiiro researcher who participated in the investigation of exposed secrets in public repositories.Shmulik CohenApiiro researcher who participated in the investigation of exposed secrets in public repositories.
Malware
Vendors
Products
Claude CodeClaude Code Leaking Secrets Across Nearly Two Thousand Public GitHub RepositoriesGitHubClaude Code Leaking Secrets Across Nearly Two Thousand Public GitHub RepositoriesGitLabBeyond GitHub, the researchers also spotted exposed configuration files on Hugging Face Spaces and GitLab.Hugging Face SpacesBeyond GitHub, the researchers also spotted exposed configuration files on Hugging Face Spaces and GitLab.
Tools
Industries
PaymentsThis exposure directly impacts 63 identified organizations, ranging from B2B startups and payments companies to universities and established software vendors.SoftwareThis exposure directly impacts 63 identified organizations, ranging from B2B startups and payments companies to universities and established software vendors.