
Apiiro Finds Secrets in 1,122 Public Claude Code Settings Files
Summary
Apiiro found secrets in 1,122 public copies of Claude Code’s settings.local.json. Researchers did not test whether most remain valid; one notified company confirmed its key was live. Git history and forks can retain the files.
Key points
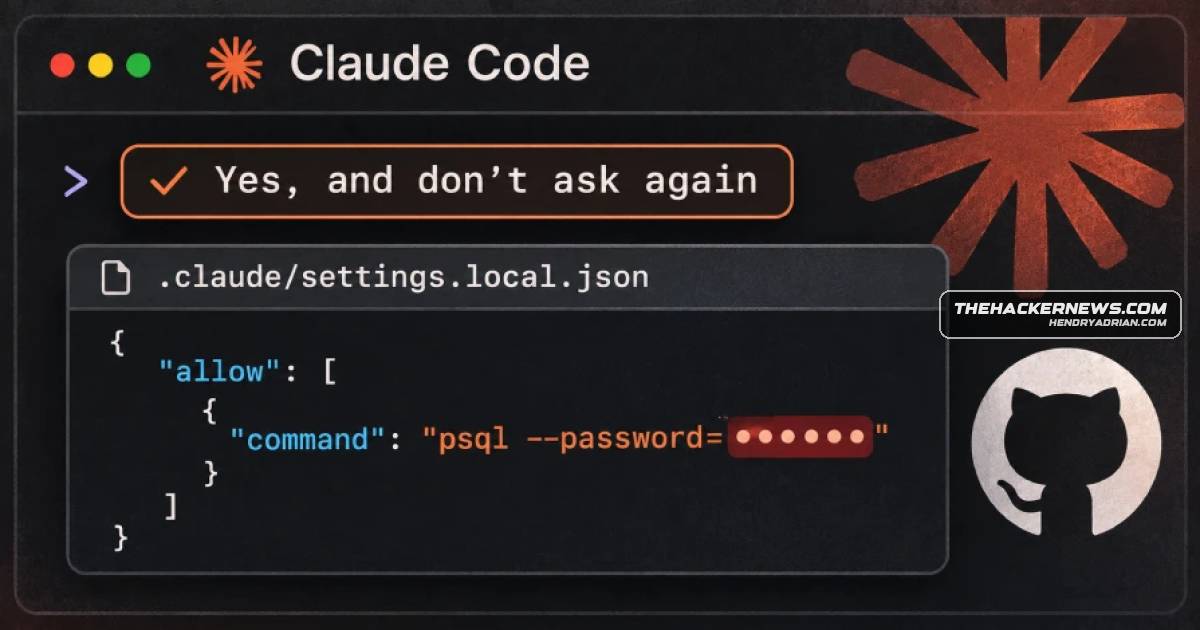
- Selecting “Yes, and don't ask again” can save an approved command verbatim in .claude/settings.local.json, including passwords or tokens typed into it.
- Apiiro found 104,185 copies of the file across 103,617 public repositories; 1,122 copies contained at least one secret, totaling 1,379 distinct secrets.
- One company notified by researchers confirmed its key had been live. Researchers did not test whether the other secrets still worked.
- The file is excluded through a user's global Git settings, but that protection does not apply to files already committed; deleting a file does not remove it from Git history or repository forks.
- Researchers found 734 additional secrets in older file versions across 509 repositories; 211 forks of 74 repositories carried the same secrets as their originals.
- Of 1,122 secret-bearing files, Gitleaks flagged 564 and TruffleHog flagged 643; neither flagged 215. Plain-text passwords in commands were a common reason scanners missed secrets.
- Researchers recommend rotating every password, token, and key the file has held before cleaning up exposed copies.
Article Details
- Publisher
- The Hacker News
- Scope
- Apiiro's analysis of exposed Claude Code settings files and secrets in public GitHub repositories.
- Sample Size
- 104,185 copies of .claude/settings.local.json across 103,617 public GitHub repositories.
- Key Statistics
- 1,122 of 104,185 copies (about 1.1%) contained at least one secret; the researchers identified 1,379 distinct secrets.
- The researchers identified 734 additional secrets in older file versions across 509 repositories that were absent from current copies.
- Including shared settings files, older versions, and saved agent chat logs, the researchers counted 2,539 secrets across 1,994 repositories.
- Of 1,122 files containing a secret, gitleaks flagged 564 and TruffleHog flagged 643; neither tool flagged 215.
- Recommendations
- Rotate every password, token, and key the file has ever contained, then clean up the exposed files.
Malware
Vendors
Products
Claude CodePasswords and API keys that developers typed into commands they approved in Claude Code are sitting in public GitHub repositories, where anyone can read them.Claude Opus 5.5In public files, the researchers found saved commands with the secret still inside, and they reproduced the behavior with the latest models, Opus 5.5 and Fable 5.1.Fable 5.1In public files, the researchers found saved commands with the secret still inside, and they reproduced the behavior with the latest models, Opus 5.5 and Fable 5.1.GitHubPasswords and API keys that developers typed into commands they approved in Claude Code are sitting in public GitHub repositories, where anyone can read them.
Tools
gitleaksCommon secret scanners miss many of these files. The researchers ran gitleaks and TruffleHog over every copy, without the tools' verification step. Of the 1,122 files with a secret, gitleaks flagged 564 and TruffleHogTruffleHoghas previously looked for secrets on developer machines. In September 2025, the Shai-Hulud worm ran the TruffleHog secret scanner over infected computers, and the scanner flagged more than half of the files as secret.